
 Do Son
Apache NiFi 2.9.0 fixes a high-severity RCE (CVE-2026-39816) in the Tinkerpop service. Secure your data pipelines and verify your annotations today!
rce
Apache Storm patches a critical RCE via unsafe deserialization and a stored XSS in its UI. Secure your data streams—upgrade to version 2.8.6 today!
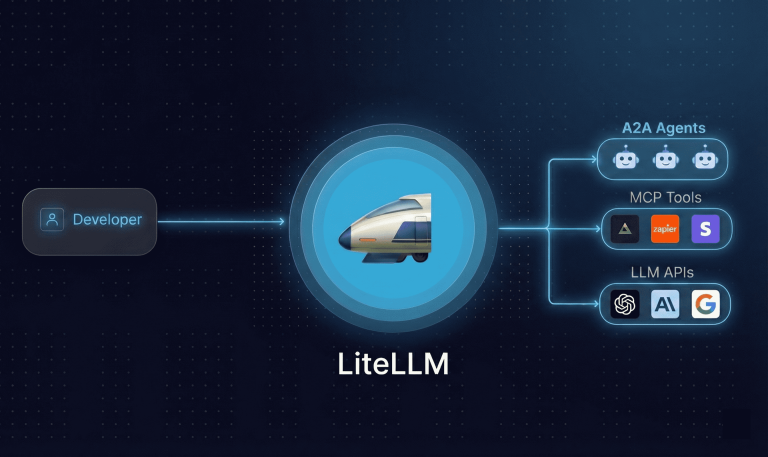
LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!

Sonatype patches a critical 9.4 CVSS RCE in Nexus Repository 3 (CVE-2026-3199). Secure your supply chain—upgrade to version 3.91.0 immediately!
Unauthenticated RCE in marimo (CVE-2026-39987) exploited in the wild in record time. Attackers gained root access in under 10 hours. Patch to v0.23.0 now!

Movable Type patches a critical 9.8 CVSS RCE vulnerability in its Listing Framework. Secure your CMS against Perl code execution and SQLi—update today!
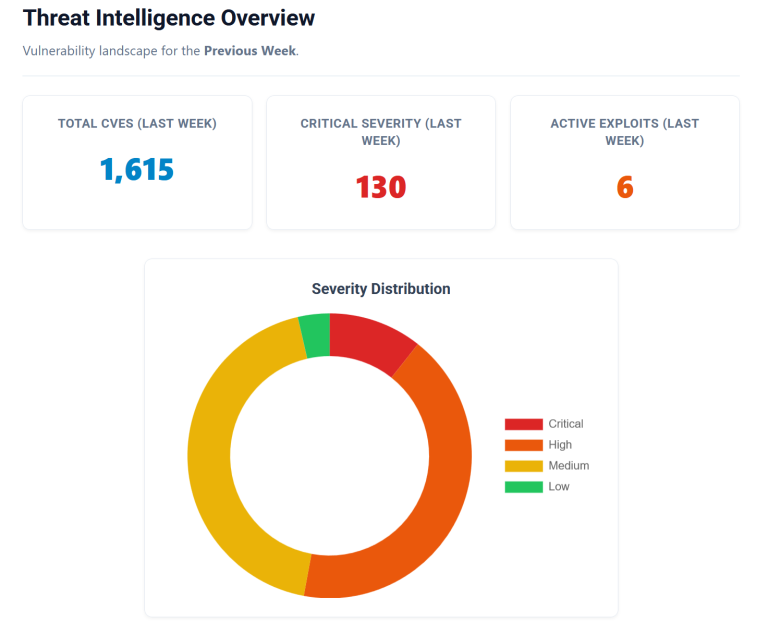
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.

A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!
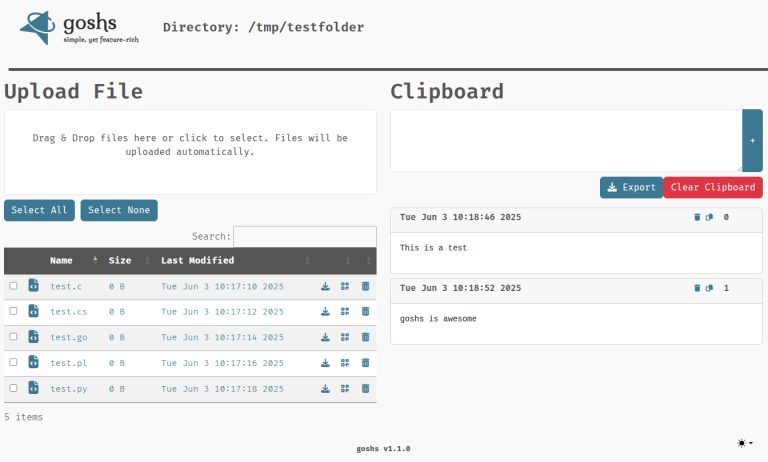
Critical 9.8 flaws in goshs v2.0.0-beta.2 allow unauthenticated attackers to write or delete any file on your system. Update to v2.0.0-beta.3 immediately!
Everest Forms patches a critical 9.8 CVSS PHP Object Injection vulnerability affecting 100,000+ sites. Update to v3.4.4 now to prevent full site takeover!

Critical 9.3 CVSS flaw (CVE-2026-34078) in Flatpak allows apps to escape sandboxes and access all host files. Secure your Linux system—update to v1.16.4 now!
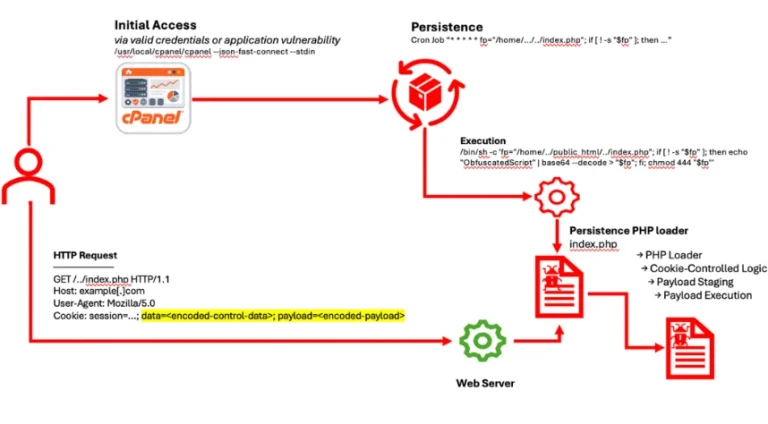
Microsoft Defender unmasks a stealthy PHP web shell hiding C2 logic in HTTP cookies. Learn how "cookie-gating" bypasses logs to maintain persistent RCE.

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!
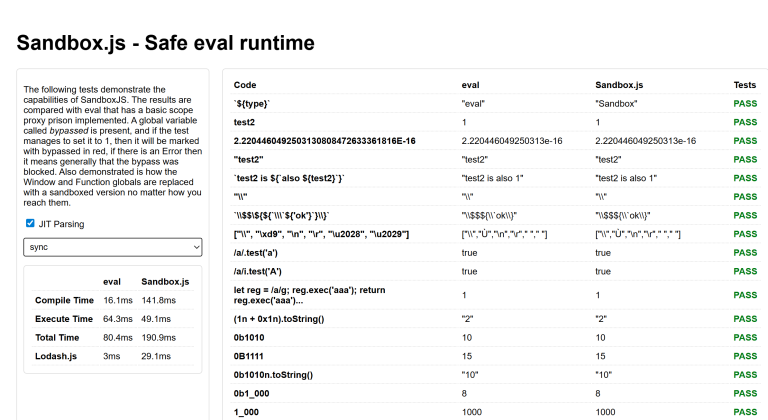
CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!


Weaver E-cology 10.0 faces a critical 9.3 CVSS RCE (CVE-2026-22679). Unauthenticated attackers can hijack servers via a debug endpoint. Patch immediately!

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!

A critical Adobe Reader zero-day allows attackers to steal local files and achieve system control via malicious PDFs. Learn how the unpatched exploit works.
Critical 9.6 CVSS flaws in Budibase allow unauthenticated RCE and data exfiltration via SSRF. Secure your internal tools—update to v3.33.4 now.

CVE-2026-34612: A critical 10.0 flaw in Kestra allows RCE via SQL injection in label searches. Protect your orchestration server—update to v1.3.7 now!

A critical 9.8 CVSS flaw in Ninja Forms - File Upload plugin allows unauthenticated RCE. 50,000+ WordPress sites are at risk. Update to v3.3.27 now!

CVE-2026-34838: A critical 10.0 flaw in GroupOffice allows authenticated users to trigger RCE via insecure deserialization. Update to v26.0.12 immediately!