
 Do Son
Apache MINA (CVE-2026-41635) suffers a critical 9.8 CVSS RCE flaw. Learn how a deserialization filter bypass puts servers at risk and how to patch today.
rce

Critical 9.8 CVSS RCE in Pipecat (CVE-2025-62373)! Unsafe pickle deserialization allows remote code execution. Patch to v0.0.94 immediately to secure agents.
New Spring Boot flaws (CVSS 9.1) bypass security filters and enable RCE via timing attacks. Impacting versions 2.7.x to 4.0.x—secure your Java apps now.
Critical RCE and XSS vulnerabilities hit Apache ActiveMQ (CVE-2026-41044, 40466). Authenticated attackers can hijack the JVM. Update to 5.19.6 or 6.2.5 now.

Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.

Python’s asyncio on Windows faces a high-severity RCE (CVE-2026-3298). A missing boundary check in ProacterEventLoop risks memory corruption. Update now.
Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!

PHPUnit CVE-2026-41570 allows RCE via invisible newline injection in CI/CD pipelines. Secure your build servers—update to 12.5.22 or 13.1.6 today.
Critical 10.0 CVSS flaw in Firebird Database allows RCE via path traversal in the engine loader. Attackers gain root/SYSTEM privileges. Patch to 5.0.4+ now.

Akamai SIRT warns of a new Mirai campaign weaponizing EOL D-Link routers via CVE-2025-29635. Protect your network from zombie botnets—retire old hardware now.

Atlassian Bamboo Data Center hit by critical 9.4 RCE (CVE-2026-21571). Attackers can hijack your build pipeline. Secure your supply chain—patch now!

Two critical CVSS 10.0 RCE flaws in Spinnaker's Clouddriver and Echo services allow full JVM and shell access. Patch your multi-cloud pipelines immediately.

SGLang faces a critical 9.8 CVSS RCE flaw (CVE-2026-5760). Malicious GGUF models can hijack AI servers via unsandboxed Jinja2 templates. Learn how to fix it.

Progress Software warns of 5 critical MOVEit WAF & ADC flaws. RCE and WAF bypass risks allow total system hijack. Upgrade to v7.2.63.0 now to stay secure.

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

ASUSTOR issues an urgent fix for CVE-2026-6644, a critical 9.4 CVSS flaw in ADM's VPN client allowing full NAS takeover. Patch to ADM 5.1.3.RGL1 now.

Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.

Apache Syncope CVE-2025-57738 allows root RCE via unsandboxed Groovy. Technical details and PoC are now public. Upgrade to v3.0.14 or 4.0.2 immediately.

Dolibarr ERP faces a critical 9.4 CVSS RCE flaw (CVE-2026-23500) in its PDF conversion logic. Unsanitized commands allow full system takeover. Upgrade to 23.0!
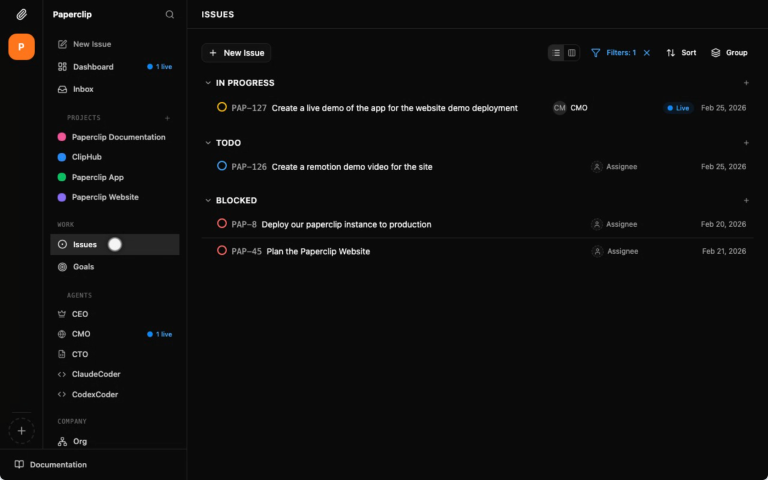
Paperclip’s 9.8 CVSS flaw and cross-tenant leaks expose AI agents to total takeover. Learn how a simple command could compromise your entire business.

Critical 9.1 CVSS flaw in FortiSandbox: Full PoC & details for CVE-2026-39808 are now public. Unauthenticated root RCE is possible. Upgrade to 4.4.9 immediately.
Thymeleaf 3.1.4 fixes two critical 9.1 CVSS vulnerabilities. Unauthenticated attackers can bypass security for SSTI. Audit your user input and patch today!