 Do Son
CERT@VDE warns of critical RCE and SQLi flaws in MB Connect Line's mbCONNECT24 (up to v2.19.4). Unauthenticated attackers can gain full system control. Patch now!
rce

Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!

Unit 42 reveals how GCP Vertex AI agents can become "double agents," exfiltrating data and accessing Google’s internal code. Learn why BYOSA is essential.

Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!
Artifex MuPDF faces a 7.8 CVSS integer overflow (CVE-2026-3308) allowing RCE via "crafted" PDFs. With no official patch, sandboxing is vital. Update now.

Progress ShareFile hit by critical 9.8 CVSS RCE flaws (CVE-2026-2699). Unauthenticated attackers can hijack configuration and execute code. Update to v5.12.4!

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20160) in SSM On-Prem. Unauthenticated attackers gain root access via exposed APIs. Update to 9-202601 now!

NocoBase patches a CVSS 10.0 RCE vulnerability (CVE-2026-34156). A simple console object bypasses the sandbox for root access. Update to 2.0.28 now!

NVIDIA fixes high-severity flaws (CVE-2026-24164) in BioNeMo. Attackers could execute code or disrupt AI drug discovery. Update to commit e5e58c8 now.

PolyShell Exposed: Public PoC and active exploitation disclosed for critical Magento RCE. With no official patch, your storefront is at risk. Secure it now!
Vim patches a critical 8.2 CVSS RCE (CVE-2026-34982). Malicious "modelines" can bypass sandboxes to execute commands. Update to 9.2.0276 immediately!
Public PoC exploit and details are out for Nginx UI’s 9.4 CVSS backup flaw (CVE-2026-33026). Attackers can hijack servers via tampered backups. Update now!
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!
Foreman patches a critical 8.0 CVSS command injection flaw (CVE-2026-1961). Malicious hostnames can trigger RCE via WebSocket proxies. Update to 3.18.1 now!
Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.
OpenTelemetry patches a critical 9.3 RCE flaw (CVE-2026-33701) in its Java agent. Unfiltered RMI deserialization allows full system takeover. Update to 2.26.1.

Researchers reveal critical RCE and ARM-specific flaws in libpng (CVE-2026-33636 & 33416). Affecting decades of apps, these bugs require an immediate update.
Vim patches a critical 8.2 CVSS bug chain in modelines and tabpanels. Opening a malicious file triggers instant RCE. Update to 9.2.0272 now to stay safe.
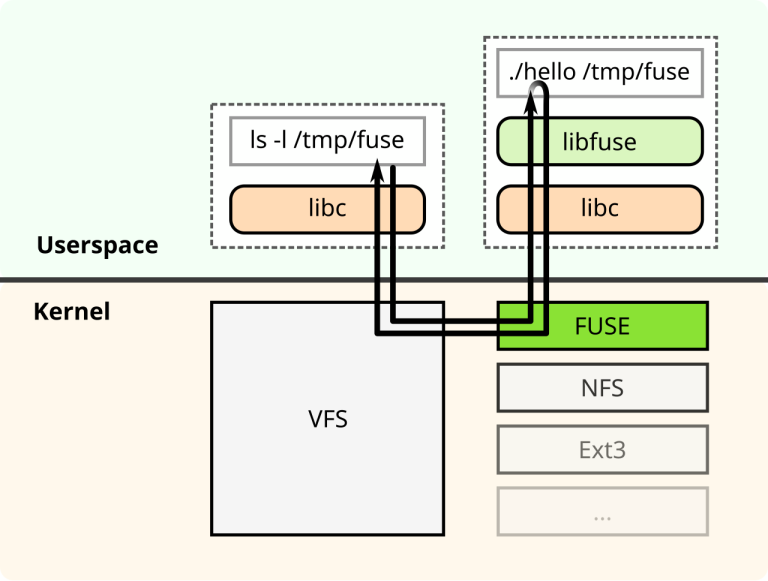
Researchers uncover two flaws in libfuse's io_uring transport (CVE-2026-33150 & 33179). Impacting Kubernetes CSI drivers, these bugs allow RCE and DoS. Patch now!

Grafana patches a critical 9.1 RCE (CVE-2026-27876) in SQL expressions that allows SSH hijacking. Update to 12.4.2 now to secure your monitoring host.
CISA adds F5 BIG-IP RCE (CVE-2025-53521) to its KEV Catalog. With a 9.8 CVSS score and active exploits, federal agencies must patch by March 30, 2026.