 Do Son
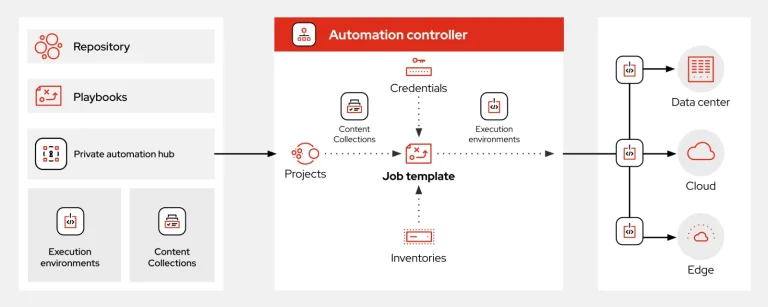
Patch these critical Ansible Automation Platform vulnerabilities to prevent privilege escalation. Ansible Automation Platform vulnerabilities expose secrets.
red hat
Broadcom's unexpected VDDK download removal has severely disrupted VMware migrations. Learn how this impacts Azure and Red Hat enterprise transitions.
CERN's Debian migration moves 2,200+ accelerator control machines off Red Hat, driven by RHEL's raised x86-64 CPU baseline.
A Keycloak account takeover flaw, CVE-2026-18963, lets attackers reset any user's password with no email verification. Update to 26.7.2 now.
CVE-2026-67567 (CVSS 9.9) leads three Red Hat privilege escalation flaws in ACM and FreeIPA. Two FreeIPA bugs can reach full domain compromise.
Red Hat ACM privilege escalation flaws (CVE-2026-70496, CVSS 9.9) let attackers seize full cluster control. See the three Kubernetes bugs.
Red Hat fixes RHACM remote code execution flaws, including CVE-2026-72526 and CVE-2026-73268, both CVSS 9.9. See patch and mitigation steps.
CVE-2026-10090 lets an edit-scoped user gain cluster-admin in Red Hat ACM for Kubernetes. Privilege escalation rated CVSS 9.9.
CVE-2026-15378 is a blind SSRF in Red Hat OpenShift AI. The guardrails-detectors flaw exposes cloud credentials and Kubernetes secrets.
CVE-2026-1207 is a Django SQL injection flaw (CVSS 8.3) in PostGIS raster lookups. Canada's CCCS says it is exploited in the wild. Patch now.
A missing authorization flaw in Event-Driven Ansible (CVE-2026-11807, CVSS 9.6) leaks credentials like OAuth tokens, vault passwords, and SSH keys.
Red Hat RHEL 10.2 & 9.8 arrive with NIST Post-Quantum Cryptography, AI-driven Ansible upgrades, and MCP servers for natural language system governance.

OpenStack patches CVE-2026-22797 (Privilege Escalation). Flaw in OAuth2 middleware allows header forgery for admin access. Update keystonemiddleware now.

A critical Linux KVM flaw allows guests using Intel AMX to trigger host kernel panics. Fixes are underway for modern kernels (5.17+) to prevent host DoS.

Red Hat confirmed a breach of its consulting arm's GitLab instance. Hackers stole 570 GB of data, including Customer Engagement Reports that detail client network infrastructure.

A critical flaw (CVE-2025-10725) in Red Hat OpenShift AI allows low-privileged users to escalate to full cluster admin privileges, risking complete platform compromise.
Qualys reveals two critical Linux vulnerabilities (CVE-2025-5054, CVE-2025-4598) in Apport & systemd-coredump, risking sensitive data exposure. Patch now!

Red Hat's new llm-d project, with industry leaders, aims to revolutionize large-scale generative AI inference for enterprises using Kubernetes and vLLM.

Red Hat and AMD expand their partnership to deliver agile and optimized AI and virtualization solutions for enterprise hybrid cloud and generative AI.
Discover the critical vulnerabilities impacting Red Hat OpenShift's security posture. Learn about CVE-2024-45496 and CVE-2024-7387 and their potential impact on the platform.
Critical security advisory: Learn about CVE-2024-7923, an authentication bypass flaw in Red Hat Pulpcore affecting Satellite deployments.

CVE-2024-6409, has been found to expose systems to potential remote code execution (RCE) due to a race condition in signal handling