
 Do Son
A new GST phishing campaign targets Indian taxpayers. This operation delivers Remcos RAT malware using an embedded bitmap payload to steal user credentials.
Remcos RAT

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.
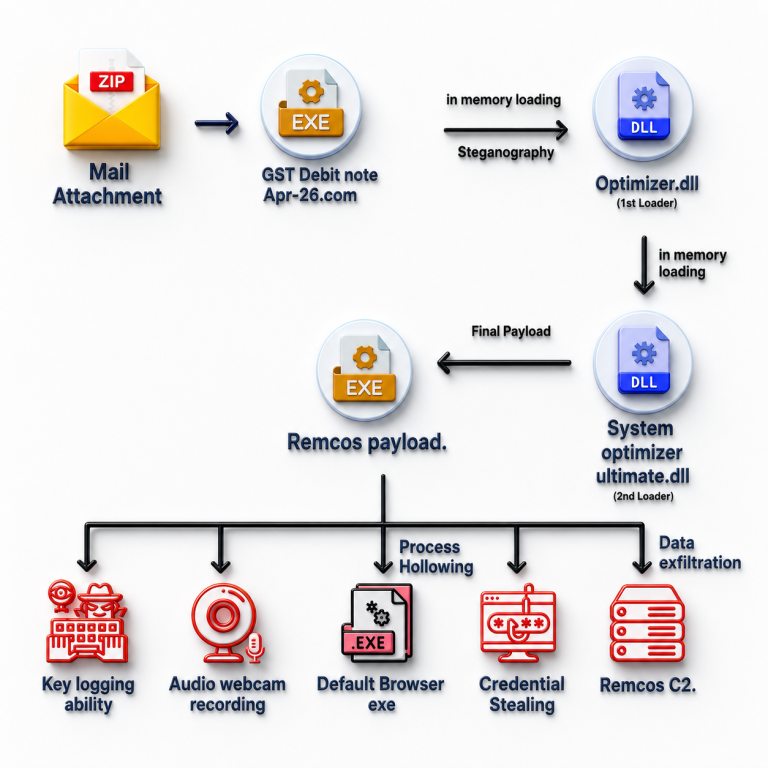
A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.
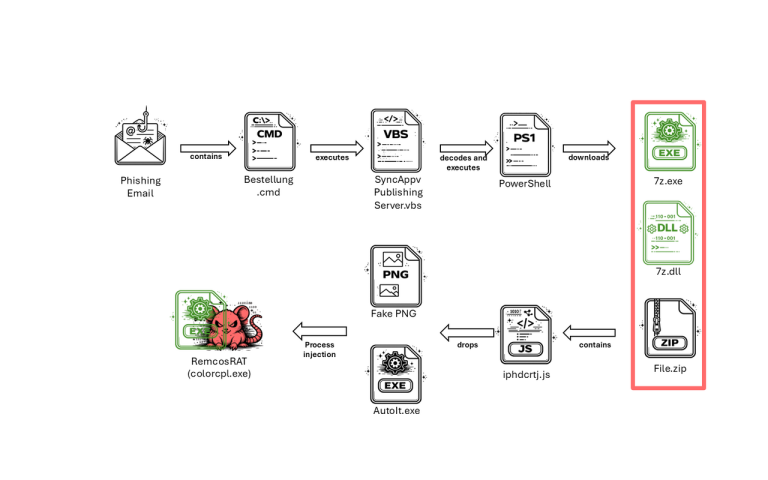
G Data uncovers a new Remcos RAT variant using DonutLoader shellcode and trusted LOLBins to bypass Windows security filters.
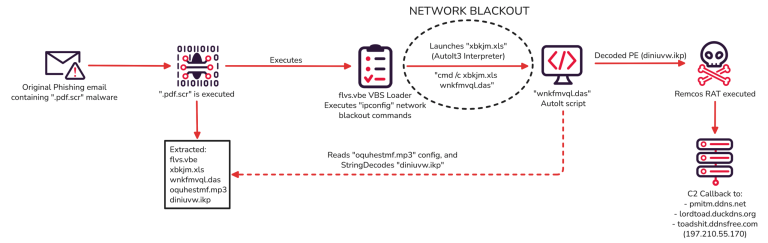
A novel Remcos RAT phishing campaign utilizes a network blackout technique to evade defense systems. Learn how to protect your enterprise network.
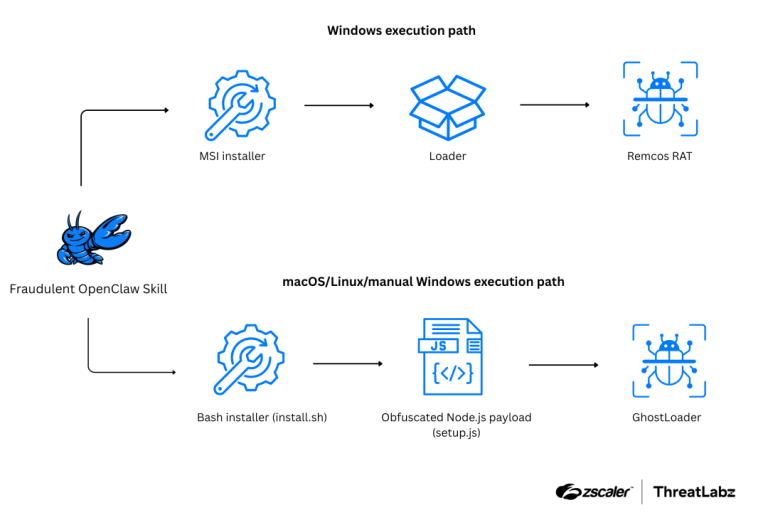
Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!
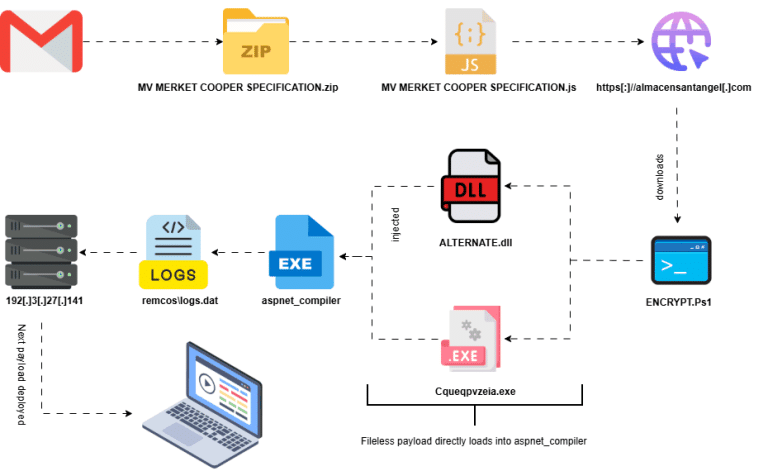
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.

LevelBlue SpiderLabs unmasks the PhantomVAI framework: a multi-stage, fileless attack hiding XWorm and Remcos RAT inside obfuscated VBS and PNG files.
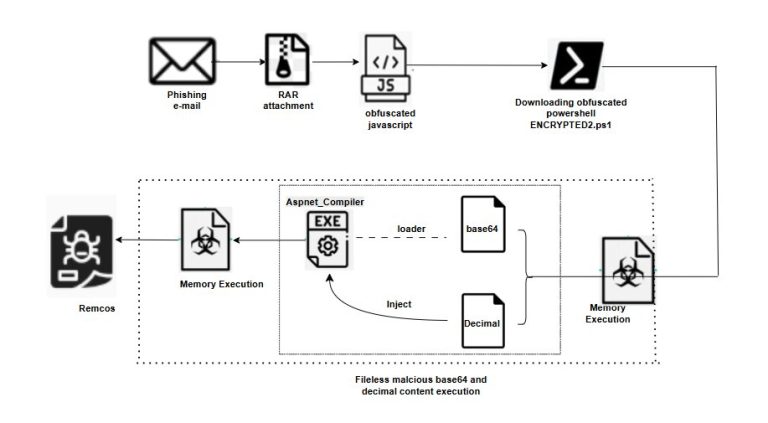
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.

New fileless Remcos RAT campaign uses a "[virus detected]" shipping lure to inject malware into memory via process hollowing. See how to spot it.

Securonix reveals SHADOW#REACTOR: A stealthy framework using "text-only" fragments to deploy Remcos RAT in memory via MSBuild. Avoids disk detection.

New phishing campaign uses fake layoff warnings to drop Guloader and Remcos RAT. Learn how this HR-themed scam exploits workplace anxiety to steal data.

Cyble reveals a unified commodity loader targeting Europe & Middle East. It uses steganography and a unique UAC bypass to deploy multiple RATs.

IBM X-Force warns that Russian-aligned Hive0156 is intensifying spear-phishing campaigns against Ukrainian government and military, delivering Remcos RAT via LNK/PowerShell files.

Remcos RAT campaign evades antivirus using PowerShell-based in-memory execution. Steals data, bypasses UAC, and avoids detection with stealthy tactics.

Unit 42 uncovers a sophisticated phishing campaign using multi-layered tactics to deliver malware like Agent Tesla, evading detection.

Explore how the Blind Eagle group has evolved since 2018, employing advanced tactics like Remote Access Trojans to conduct cyber espionage.

Stay informed about the latest phishing campaign using the Remcos RAT. Learn how the CVE-2017-0199 vulnerability is exploited to gain remote access to victims' computers.

Learn about a critical vulnerability in Secure Email Gateways and Antivirus scanners. Find out how to protect your organization from malicious VHD files.
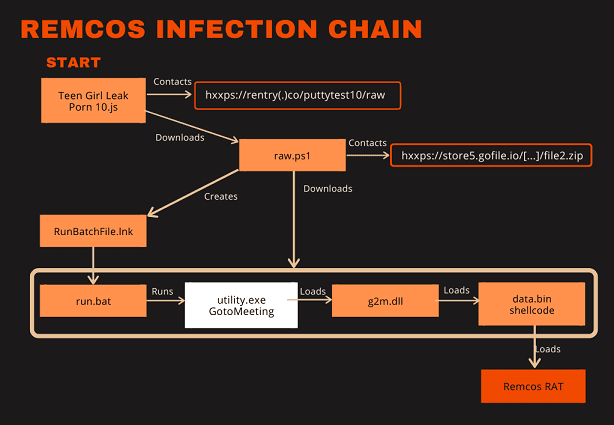
Beware of a new tax extension malware campaign exploiting GitHub links. Find out how threat actors are bypassing security defenses and distributing the Remcos RAT.

Uncover the sophisticated fileless malware campaign delivering Remcos RAT. Learn how attackers exploit CVE-2017-0199 to infiltrate systems undetected.