 Do Son
Patch two Barracuda vulnerabilities, CVE-2026-116606 and CVE-2026-111560, that allow attackers to gain Barracuda root access across multiple appliances.
root access

VMware Fusion CVE-2026-41702 allows local users to gain root access via a TOCTOU race condition. Secure your host and update to 26H1 immediately!
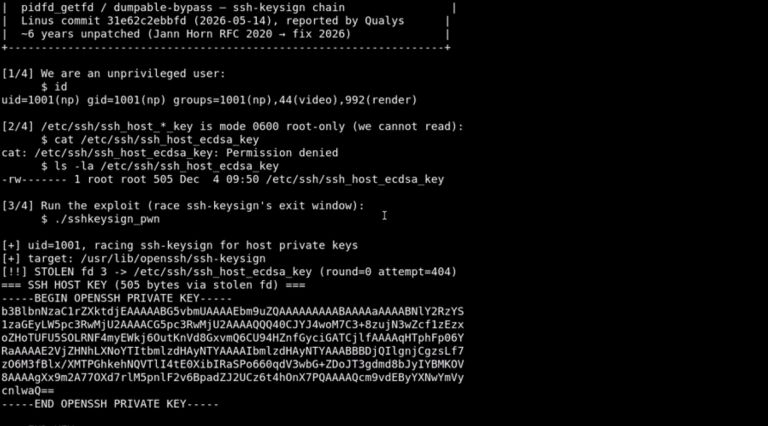
Technical details and PoC exploits disclosed for Linux Kernel ptrace flaw. Unprivileged users can steal root file descriptors. Patch to May 14 release!

Urgent: Public PoC for OPNsense CVE-2026-44194 and CVE-2026-45158. Critical flaws allow root command execution via DHCP and User sync. Update to 26.1.8 now!
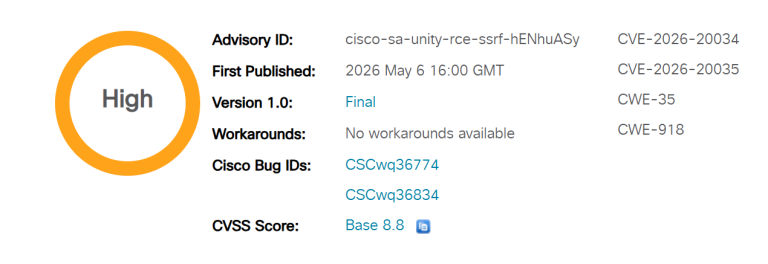
Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!
Critical 9.2 CVSS flaw in WattBox 800/820 controllers (CVE-2026-41446) allows root RCE using plaintext hardware labels. Upgrade to firmware v2.10.0.0 now.

Critical 9.0 CVSS RCE in Nginx UI (CVE-2026-42238) exploits a 10-minute unauthenticated window. Attackers can seize root control. Patch to the latest version now.

Apache Syncope CVE-2025-57738 allows root RCE via unsandboxed Groovy. Technical details and PoC are now public. Upgrade to v3.0.14 or 4.0.2 immediately.

Critical 9.1 CVSS flaw in FortiSandbox: Full PoC & details for CVE-2026-39808 are now public. Unauthenticated root RCE is possible. Upgrade to 4.4.9 immediately.
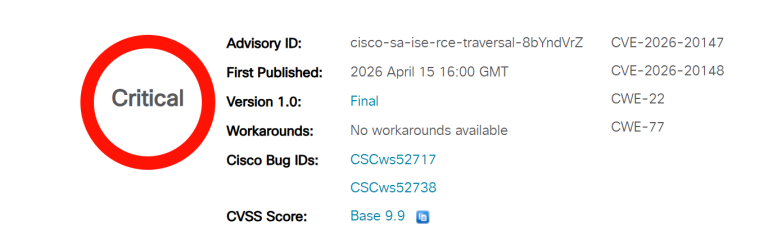
Cisco warns of a critical 9.1 RCE flaw in Identity Services Engine (ISE). Attackers can escalate to root access—apply official security patches now!
Nix patches a critical 9.0 CVSS sandbox escape. Learn how CVE-2026-39860 allows unprivileged users to seize root control via symlink manipulation. Update now!
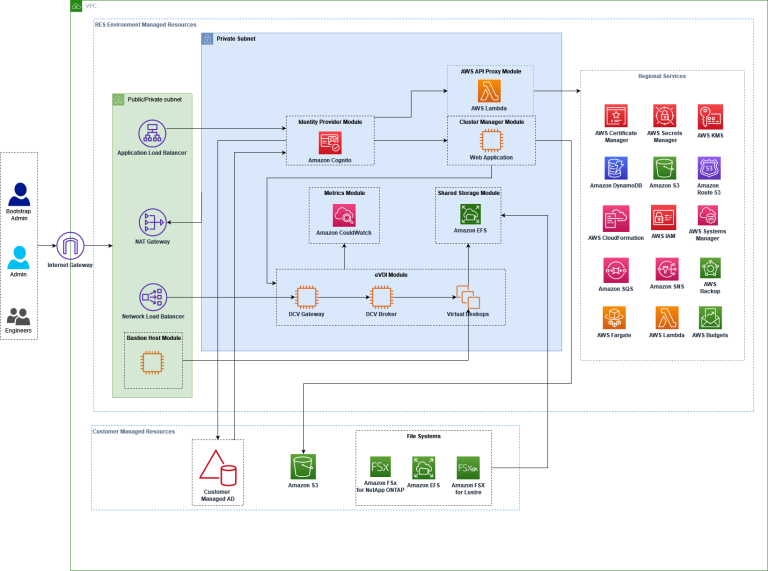
AWS patches critical RES flaws (CVE-2026-5707/8/9) allowing root access and instance profile hijacking. Protect your cloud lab—update to v2026.03 now.

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20160) in SSM On-Prem. Unauthenticated attackers gain root access via exposed APIs. Update to 9-202601 now!

NocoBase patches a CVSS 10.0 RCE vulnerability (CVE-2026-34156). A simple console object bypasses the sandbox for root access. Update to 2.0.28 now!

Samsung's OneUI 8.5 update has disabled third-party custom fonts like zFont 3 due to a "cryptographic signature" security fix. Is your Galaxy's style at risk?

CISA warns of a 9.8 CVSS flaw in Pharos Mosaic Show Controllers (CVE-2026-2417). Unauthenticated attackers can gain root access. Update to version 2.16 now.

A critical Sudo vulnerability in the exec_mailer function allows local attackers to bypass security restrictions and escalate privileges to root access.
A critical 10.0 CVSS zero-click flaw (CVE-2026-20079) in Cisco Secure FMC gives unauthenticated attackers root access. Patch your systems immediately.

Juniper Networks warns of a critical 9.8 CVSS root vulnerability (CVE-2026-21902) in PTX Series routers. Unauthenticated attackers can gain complete control.
Researcher Justin Swartz uncovers a regression of the 1999 telnetd flaw. Remote attackers can bypass authentication and seize root control via environment variables.

SolarWinds patches four critical 9.1 CVSS RCE vulnerabilities in Serv-U. Attackers can create admin users and execute code as root. Update to 15.5.4 now!