 Do Son
A Roundcube security update fixes 20 flaws, including IMAP command injection and header injection. Upgrade to 1.6.20 or 1.7.5 now.
Roundcube
An exploited Roundcube Webmail vulnerability allows SQL injection attacks. Learn how CVE-2026-48842 impacts servers and apply the latest patches immediately.
The Roundcube security update fixes 12 webmail flaws, including a zero-click stored XSS and an SSRF bypass. Update to 1.6.19 or 1.7.4 now.

Roundcube fixes a webmail RCE flaw and an SSRF filter bypass in versions 1.6.18 and 1.7.3. Update your mail server now.
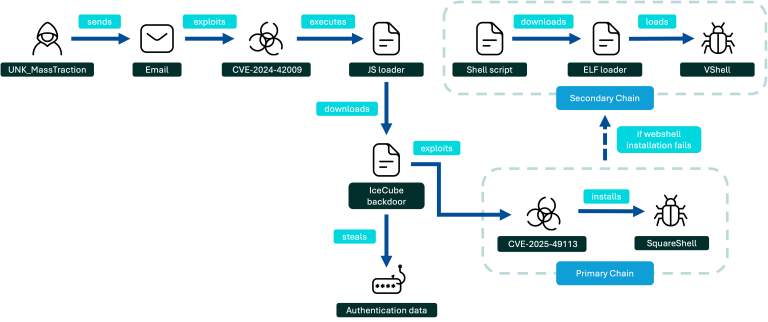
UNK_MassTraction, a suspected China-aligned actor, exploits Roundcube webmail flaws to steal credentials and deploy the VShell backdoor at universities.

A Roundcube zero-click XSS, CVE-2026-54433, lets an email run script with no click. Roundcube 1.7.2 also fixes a second stored XSS. Update now.
New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.

Roundcube patches two High-severity flaws: an SVG-based XSS and a CSS sanitizer bypass. Protect your inbox—update to v1.6.12 or v1.5.12 now.
CISA adds two critical vulnerabilities to KEV: Erlang/OTP (RCE) and Roundcube (XSS). Actively exploited, these flaws pose severe risks to systems and email accounts.
CERT Polska warns of a critical Roundcube XSS flaw (CVE-2024-42009) exploited by UNC1151 in spear phishing, stealing credentials and compromising Polish organizations.

A critical RCE flaw (CVE-2025-49113) in Roundcube is under active exploitation with PoC sold on forums. Patch immediately to v1.5.10 or v1.6.11!

Roundcube Webmail has patched a critical RCE vulnerability (CVE-2025-49113) allowing remote code execution post-authentication. Update to 1.6.2 or 1.5.10 immediately!

Don't overlook the risks! Learn about actively exploited flaws in Cisco devices & Roundcube webmail software: CVE-2024-37383 & CVE-2024-20481

The new vulnerability, as revealed by ESET specialists, is identified as CVE-2023-5631 and has a CVSS score of 5.4.