 Do Son
The DOJ charged 17 Iranians in a Mabna Institute cyber theft campaign that stole 31TB of research from universities for the IRGC.
Spearphishing
Gamaredon targets critical systems by exploiting WinRAR vulnerability CVE-2025-8088 to drop GammaDrop malware. Secure your entry points now!
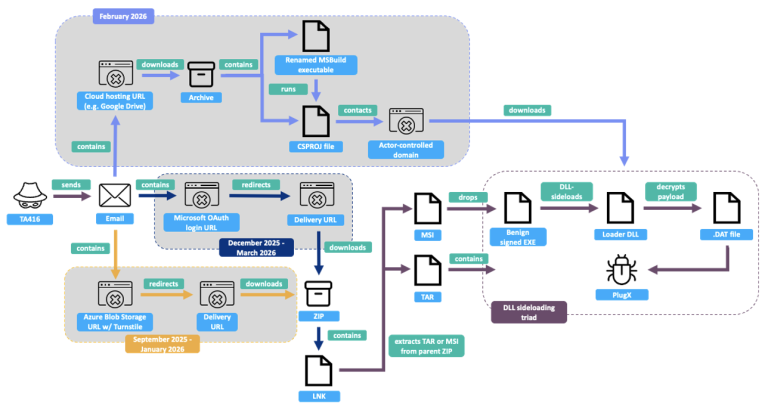
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.

BlueVoyant uncovers a shift in Mercenary Akula (UAC-0050) tactics, targeting European financial institutions via spoofed judicial lures and RMS malware.

MuddyWater APT deploys new "RustyWater" malware against Middle East targets. CloudSEK reveals how the group is ditching PowerShell for stealthy Rust tools.

A Chinese APT used fake Cloudflare verification pages and malicious LNK files to inject PlugX via DLL sideloading into a Serbian aviation agency, aiming for long-term espionage.

A new report reveals Chinese threat actor TA415 is targeting U.S. policy organizations with sophisticated spearphishing campaigns to gather intelligence.
North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.

Israeli hacker-for-hire Aviram Azari was sentenced in the Southern District of New York to 80 months of incarceration for orchestrating