 Do Son
A Skynet LLMjacking agent hijacks exposed AI models to scan, hack servers and mine crypto for 100,000 steps, while victims pay the bill.
Symantec

APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
Symantec reveals the Aoki infostealer. The Aokigahara Aoki infostealer steals API keys and session files from Claude, Codex, Cursor, and Gemini.
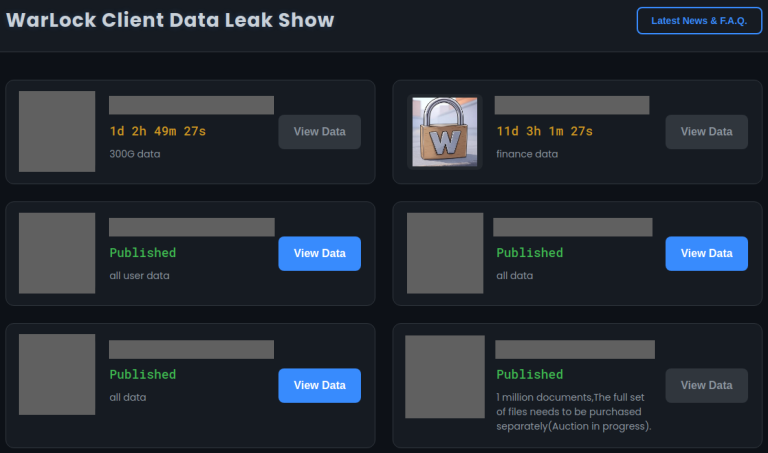
The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
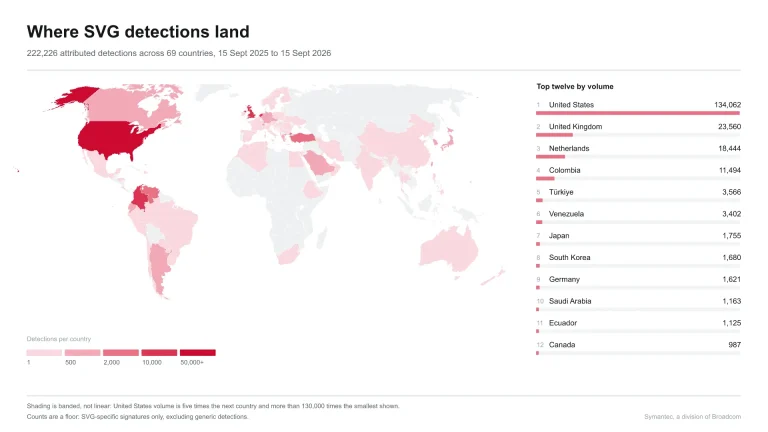
SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.

Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.

Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.
GodDamn ransomware is the latest Beast ransomware rebrand from Hyadina. It uses a Microsoft-signed malicious kernel driver, PoisonX, to disable EDR.

Discover how stealthy Outlook mailbox theft fueled a 5-month executive espionage campaign at a global stock exchange using trusted cloud tools.

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.

Researchers reveal Infostealer.Speagle, a "parasitic" malware hijacking Cobra DocGuard infrastructure to mask the theft of sensitive ballistic missile data.

Black Basta ransomware now embeds a vulnerable NsecSoft driver (BYOVD) to silently kill antivirus processes like Sophos & CrowdStrike.

New Osiris ransomware hits Southeast Asia, linking to Inc & Medusa groups. It uses BYOVD tactics to disable defenses. Unrelated to the 2016 variant.

Symantec's report reveals LockBit is using evolved tactics, including DLL sideloading and process masquerading with legitimate executables, to evade detection and deploy payloads.

A critical RCE flaw (CVE-2025-5333) in Symantec Endpoint Management (Altiris) allows unauthenticated attackers to execute arbitrary code via insecure .NET Remoting deserialization.

Symantec reports a Fog ransomware attack on an Asian bank that used unusual tools like employee monitoring software and an APT-linked backdoor, suggesting possible espionage.

Symantec reveals popular Chrome extensions like Browsec VPN & DualSafe Password Manager are leaking sensitive user data over unencrypted HTTP, risking privacy.

Symantec found over 21 million Chrome extension users at risk due to hardcoded API keys and secrets, potentially leading to data manipulation and financial loss.

The Billbug group targeted Southeast Asian organizations using advanced tools & DLL sideloading. This report details their sophisticated espionage campaign.

This summer, Apple will gradually begin to no longer trust the Symantec CA, and will initially cease...