 Do Son
A persistent Windows 11 Universal Print bug breaks printer queues after OS upgrades, displaying error 0x80004005 and requiring queue reinstallation.
SysAdmin
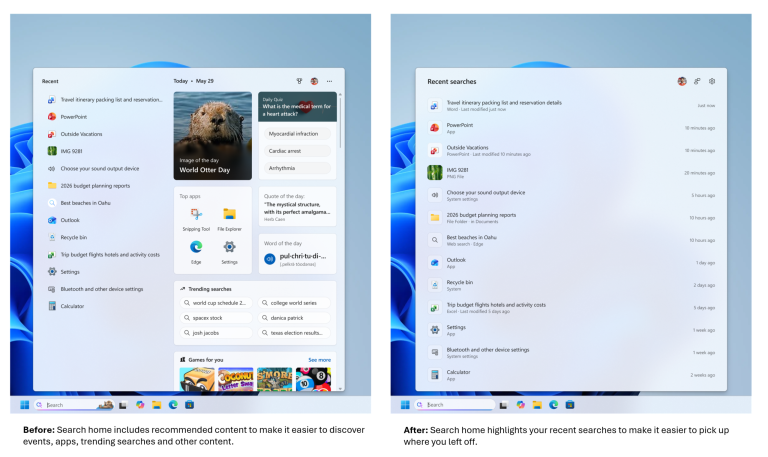
Discover the new Windows search box improvements in Windows 11. Learn how to disable Bing search distractions and prioritize local file search results.

Technical details and a functional Python PoC exploit have been released for CVE-2026-4802, a critical Cockpit flaw giving low-privilege users root.
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
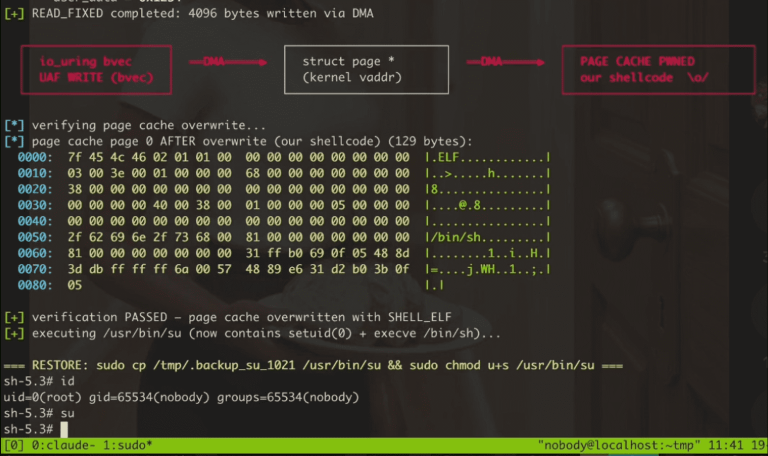
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
Technical details and a working PoC exploit are public for PinTheft, a critical Linux local privilege escalation bug. Block the RDS module now.

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.
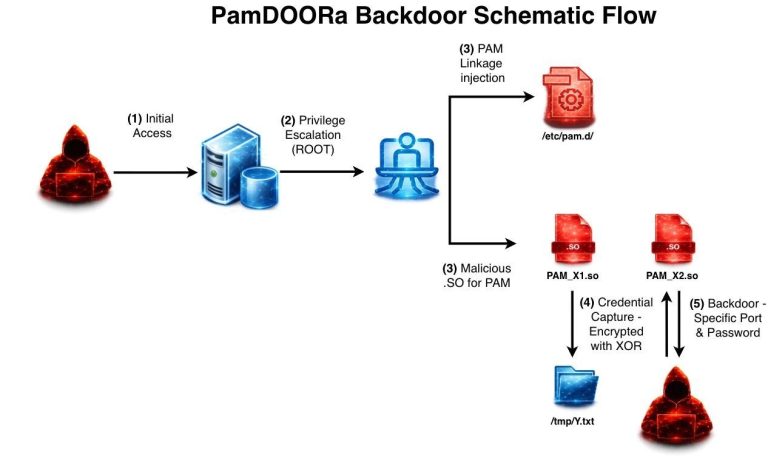
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.
PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!
Red Hat RHEL 10.2 & 9.8 arrive with NIST Post-Quantum Cryptography, AI-driven Ansible upgrades, and MCP servers for natural language system governance.

May 13 Deadline: Let’s Encrypt launches 45-day certs, freezes mTLS, and moves to Gen Y intermediates. Is your automation ready for the triple-threat update?

Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!
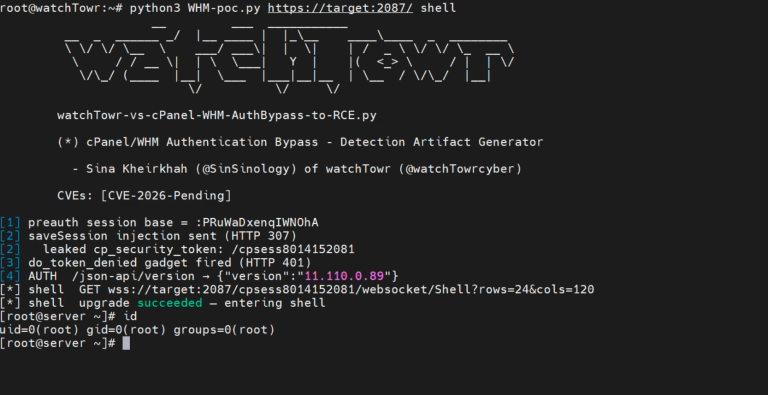
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.

Microsoft resolves the bug causing Windows Server 2019/2022 to auto-upgrade to 2025. Learn about the KB5082063 fix and the 10-day rollback window.

Use-after-free flaw in Rsync versions 3.0.1–3.4.1 allows DoS and info leaks via malicious xattr traffic. Learn how a simple qsort fix secures your syncs.
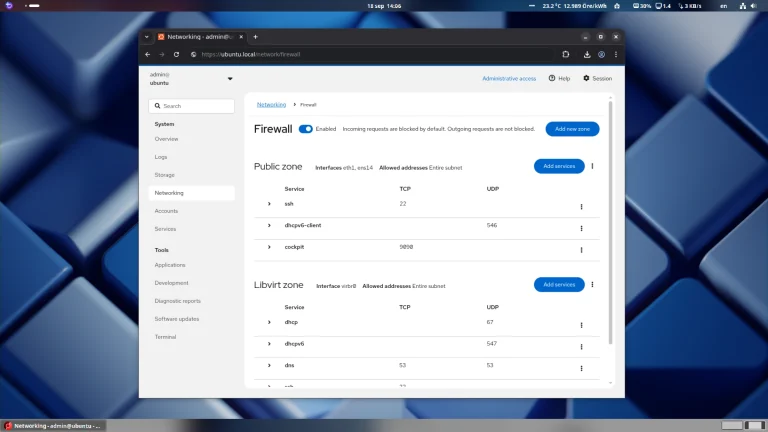
Cockpit CVE-2026-4631 allows unauthenticated RCE on Linux servers via SSH injection. Stop the unauthorized takeover—upgrade to Cockpit version 360 now!
Checkmk patches a critical 9.3 CVSS local privilege escalation flaw in the 'omd' command. Stop site users from seizing root access—update your sites today!
Vim patches a critical 8.2 CVSS bug chain in modelines and tabpanels. Opening a malicious file triggers instant RCE. Update to 9.2.0272 now to stay safe.

Microsoft Feb 2026 update fixes 61 flaws, including critical DWM zero-day CVE-2026-21519 exploited in the wild. Patch now to stop SYSTEM takeover.

Microsoft finds hackers using SolarWinds WHD to run hidden QEMU VMs. The attack uses DLL sideloading for full domain compromise. Patch immediately.

Fortinet warns of critical SQL injection CVE-2026-21643 in FortiClient EMS 7.4.4. Unauthenticated attackers can execute code. Update to v7.4.5 now.

Critical Lexmark printer flaws CVE-2025-65078 (CVSS 9.3) & CVE-2025-65077 allow remote code execution. Update firmware immediately to protect your network.
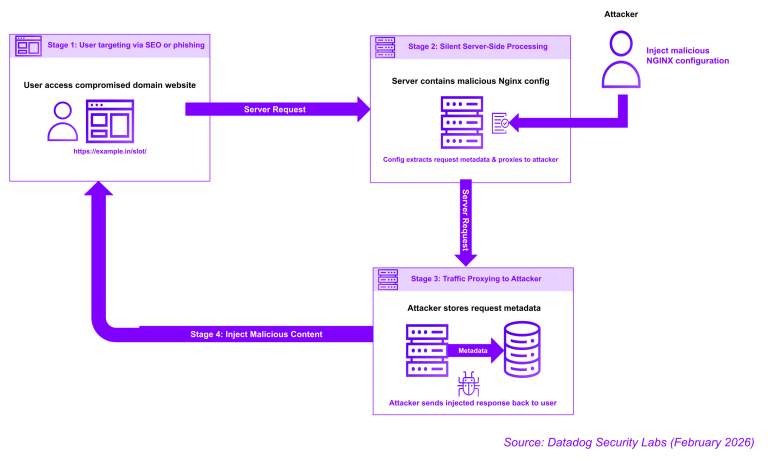
Hackers are hijacking NGINX servers via malicious config injections. Datadog warns of silent traffic redirection for SEO poisoning. Check your proxy_pass.