 Do Son
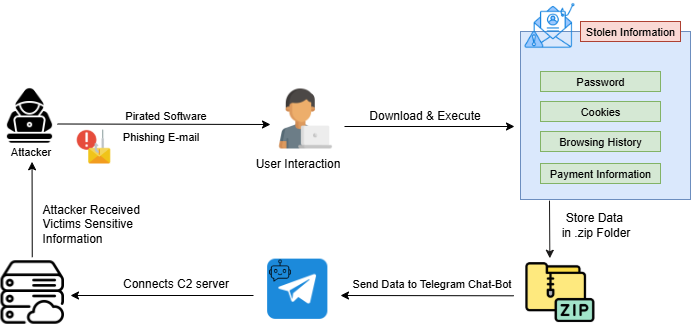
A new malware called Raven Stealer is emerging, targeting individuals and businesses by stealing credentials and data, and exfiltrating it via Telegram.
Telegram

A new Go-based remote access trojan, ZynorRAT, is targeting Linux and Windows. Its unique command and control is managed entirely through a Telegram bot.

A new Group-IB report reveals ShadowSilk, a hybrid Chinese and Russian-speaking threat cluster that uses Telegram bots for cyber espionage against Central Asian governments.
A new regulation in Russia will require all smartphones and tablets sold in the country to come pre-installed with MAX, a state-backed messaging app.

SentinelLABS and Beazley expose PXA Stealer, a Python-based infostealer campaign targeting 62 countries with stealthy DLL sideloading, decoy files, and Telegram-based data exfiltration.

Elastic Security Labs exposes NOVABLIGHT, a NodeJS-based infostealer-botnet MaaS disguised as an "educational tool," actively distributed via Telegram and targeting victims with fake game installers.

Cyfirma reveals Raven Stealer, a new, lightweight MaaS infostealer built in Delphi/C++, using reflective process hollowing and Telegram bots for stealthy data exfiltration from browsers.

Group-IB exposes MaisonReceipts, a subscription service selling fake receipts for major brands via Telegram and TikTok, fueling widespread digital fraud.

Kimsuky's AppleSeed campaign targets Korean Facebook, email, and Telegram users with evolved social engineering and stealthy malware.

Blitz malware infects gamers via backdoored Standoff 2 cheats, stealing data and cryptojacking. It uses Hugging Face for C2 and targets Windows users globally.

Socket uncovers malicious RubyGems impersonating Fastlane plugins, stealing sensitive CI/CD data by rerouting Telegram API calls. Beware of fastlane-plugin-telegram-proxy!

Netskope reveals a surge in phishing on Glitch, abusing the platform to bypass MFA and steal credentials, mainly targeting Navy Federal Credit Union members.

New lightweight PupkinStealer malware silently steals browser data, messaging sessions, and desktop files, sending it all via Telegram.

Telegram rejects France's request for a backdoor to access private messages, citing security risks. CEO Durov prioritizes privacy over market share.

Explore the Morphing Meerkat phishing operation that uses DNS techniques to target victims with tailored attacks.

Explore the Telegram Zero-Click vulnerabilities and their bounty tiers from Operation Zero, ranging up to four million dollars.

Uncover the details of the Phantom Goblin malware campaign that uses social engineering to steal browser credentials.

Beware of threats related to the DeepSeek AI Client. Discover how fraudsters exploit its popularity through malware.

Learn about EvilLoader and its impact on Telegram for Android. Discover how it enables the distribution of malware.

Uncover the details of Operation SalmonSlalom, a sophisticated malware campaign targeting critical infrastructure in Asia-Pacific.

Uncover the GitVenom campaign targeting GitHub users with malicious repositories designed to steal credentials and cryptocurrency.
Explore the emerging threat of Golang Backdoor malware, using Telegram for command-and-control and executing remote commands.