 Do Son
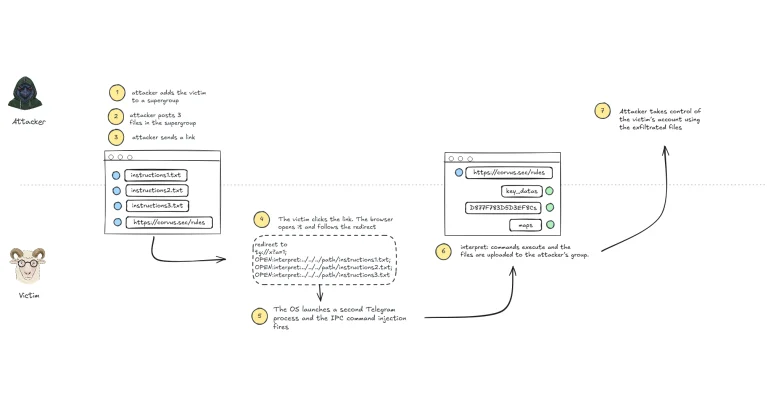
A critical Telegram Desktop account takeover vulnerability (CVE-2026-107181) exposes users to session hijacking. Exploit details and PoC are now public.
Telegram

Telegram has applied to ICANN for its own .gram domain, which would let every user claim a personal address like landian.gram tied to their account.

XCSSET v40 malware infects macOS developers through poisoned Xcode projects on GitHub, then hides in memory. Unit 42 found 17 modules and Chrome hijacking.
The t.me domain is in serverHold status, taking down all Telegram contact and share links. Telegram falls back to telegram.me for new links.
The new macOS Gaslight malware, a North Korean Rust backdoor, targets analysts with LLM prompt injection and steals sensitive keychain data.
Telegram launches Manager Mode! Now bots can create and manage sub-bots, enabling developers to deploy multi-tenant AI agent services with zero user setup.

Socket identifies 108 malicious Chrome extensions stealing Telegram sessions and Google IDs. 20,000 installs hit—audit your browser extensions immediately!

Telegram’s new "Bot-to-Bot" mode allows AI agents to talk to each other. Automate complex tasks by pairing "executor" and "overseer" bots in a single chat.
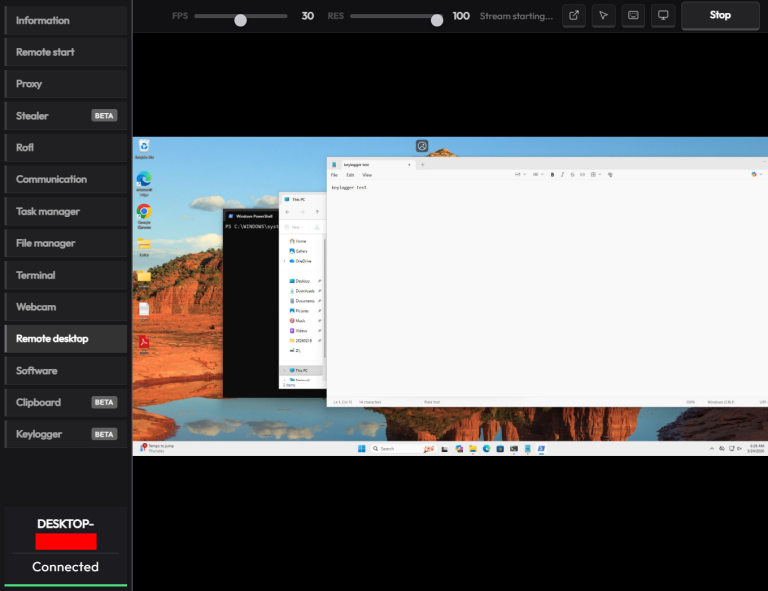
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!

A critical 9.8 CVSS zero-click flaw (ZDI-CAN-30207) hits Telegram, affecting 1 billion users. No interaction needed for full system hijack. Patching now!

Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.
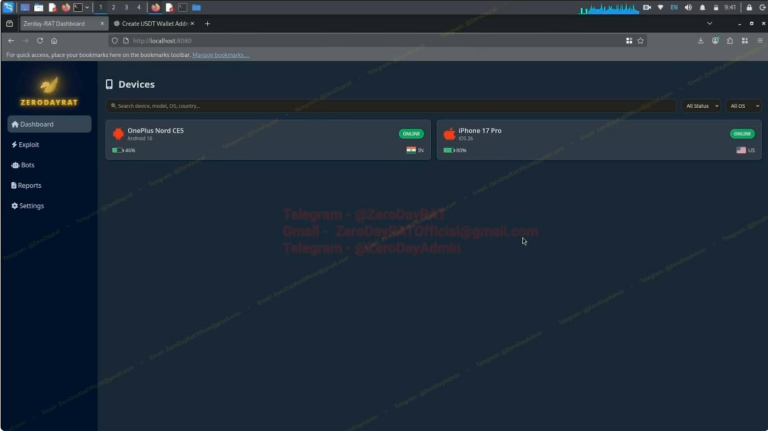
ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

Telegram confirms a January 2026 flaw where clicking "proxy links" can leak your real IP. A new warning prompt is coming to protect Android & iOS users.

Telegram's first 2026 update adds AI channel summaries powered by the private Cocoon network and a gorgeous Liquid Glass redesign for iOS.

Unit 42 unmasks VVS Stealer, a Python-based threat using Pyarmor obfuscation to bypass AV, hijack Discord sessions, and steal browser credentials.

A dangerous new Android malware called SeedSnatcher targets crypto users with overlay phishing on MetaMask/Trust Wallet. It uses BIP 39 validation to steal seed phrases and supports remote command execution for total device control.

Telegram is developing passkey authentication to replace unreliable SMS codes. The move promises a far more secure login, leveraging biometrics (Face ID/fingerprint).

India's DoT mandated SIM-binding for all messaging apps (WhatsApp, Telegram, Signal). Users must re-verify every six hours to combat cybercrime and cross-border fraud.

Kaspersky exposed Tomiris APT using a "polyglot" strategy (Go/Rust/Python) and Telegram/Discord for covert C2. The group targets foreign ministries with implants that steal file paths and reconnaissance data.

Unit 42 exposed Scattered LAPSUS$ Hunters pivoting to Extortion-as-a-Service (EaaS) after Salesforce leaks. The group is recruiting insiders and teasing SHINYSP1D3R ransomware on Telegram.

Forescout found pro-Russian hacktivist group TwoNet fabricated critical infrastructure attacks after compromising a honeypot, exploiting a default login, and pushing the false claim on Telegram.