
 Do Son
Rockwell Automation issues an urgent warning: disconnect industrial controllers from the internet immediately to protect against active threat actors.
threat intelligence
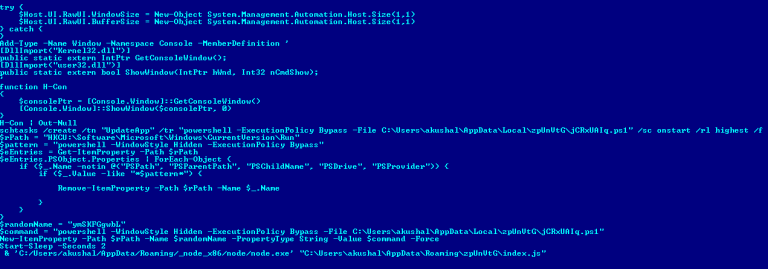
Bitdefender uncovers a malicious Windsurf IDE extension using the Solana blockchain as an unblockable C2 to steal developer credentials and source code.
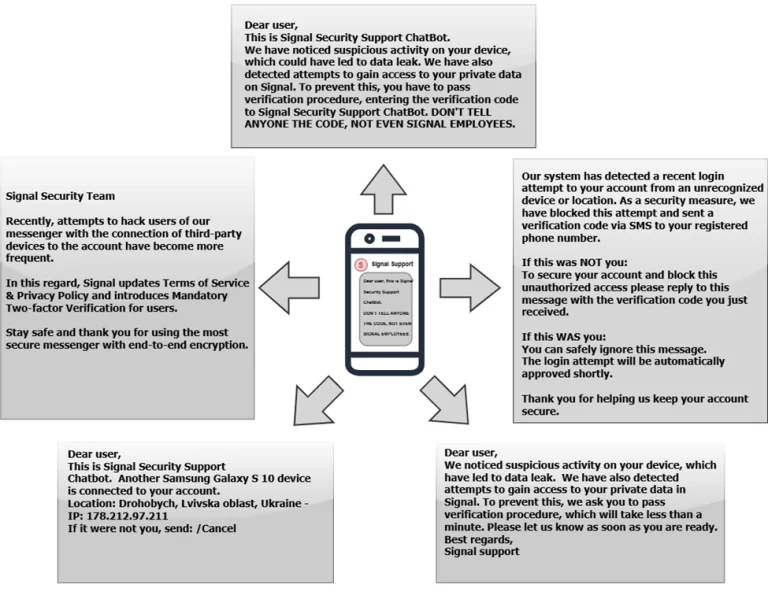
The FBI and CISA warn that Russian Intelligence is using sophisticated phishing to hijack Signal and other messaging apps via linked device features.
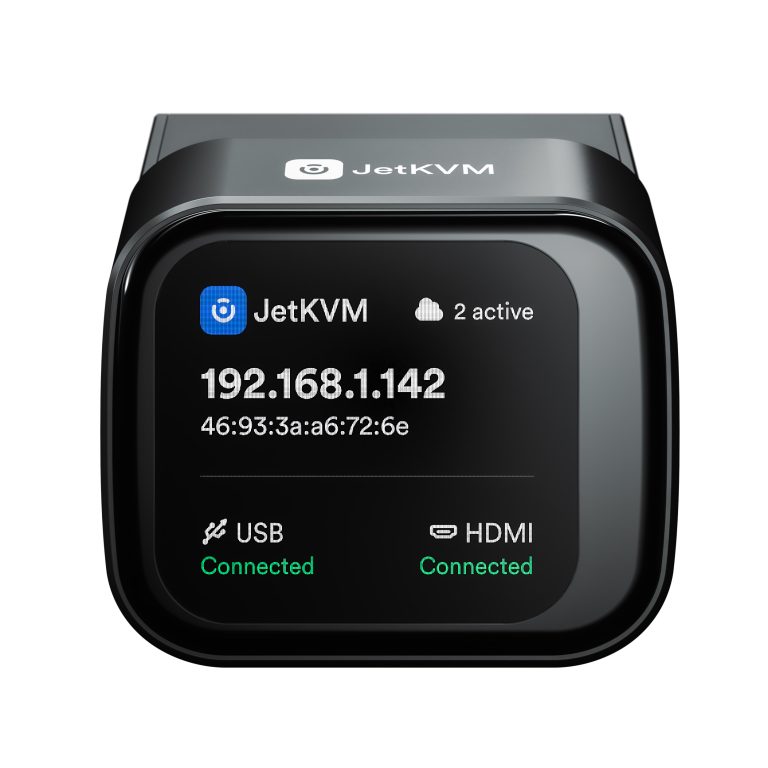
Eclypsium researchers reveal how compromised IP-KVM switches bypass EDR and software security to grant attackers total, BIOS-level system takeover.

Netwrix issues an urgent advisory for critical vulnerabilities in its Password Secure platform allowing arbitrary code execution. Update to v26.3.100 now.

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.

Acronis uncovers a massive campaign targeting gamers with fake cheats to deliver Vidar Stealer 2.0, a highly evasive malware stealing crypto and passwords.
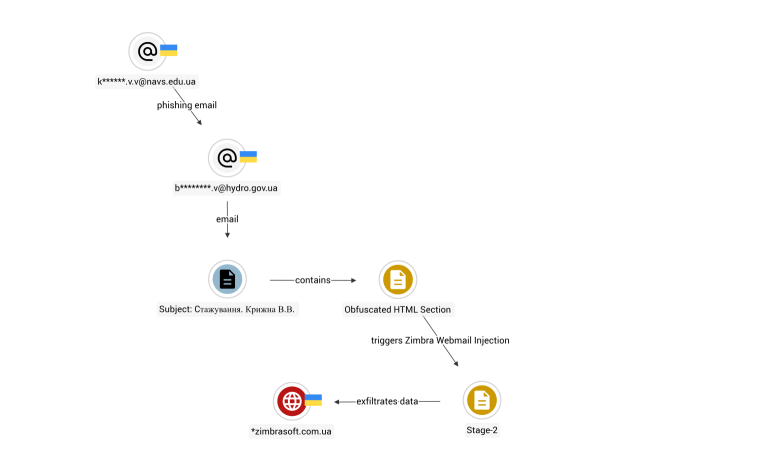
Seqrite Labs uncovers Operation GhostMail, an APT28-linked campaign using a zero-click XSS flaw in Zimbra to silently hijack Ukrainian government webmail.

Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.

The US DOJ, alongside Canada and Germany, has dismantled four massive IoT botnets responsible for record-breaking 30 Tbps DDoS attacks worldwide.

BI.ZONE uncovers Forbidden Hyena using AI-generated code to deploy the new BlackReaperRAT and Milkyway ransomware in highly evasive cyberattacks.

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.
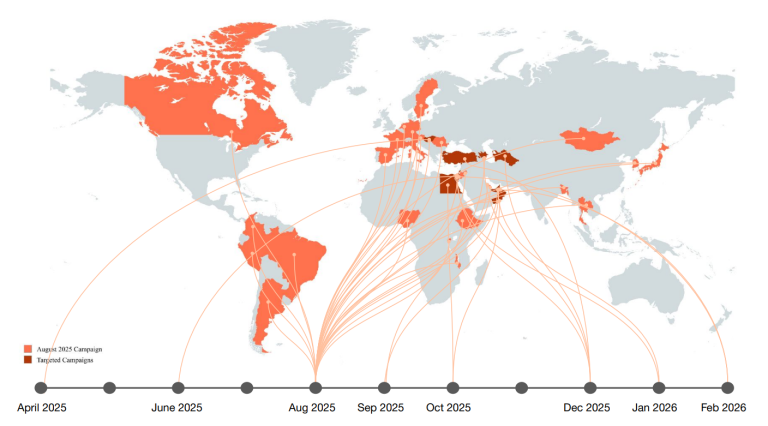
Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.
Two critical flaws in Langflow (CVE-2026-33017 & CVE-2026-33309) allow unauthenticated remote code execution and arbitrary file writes. Secure servers now.

In a move to protect the nation’s critical infrastructure, the Cybersecurity and Infrastructure Security Agency (CISA) has...

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.
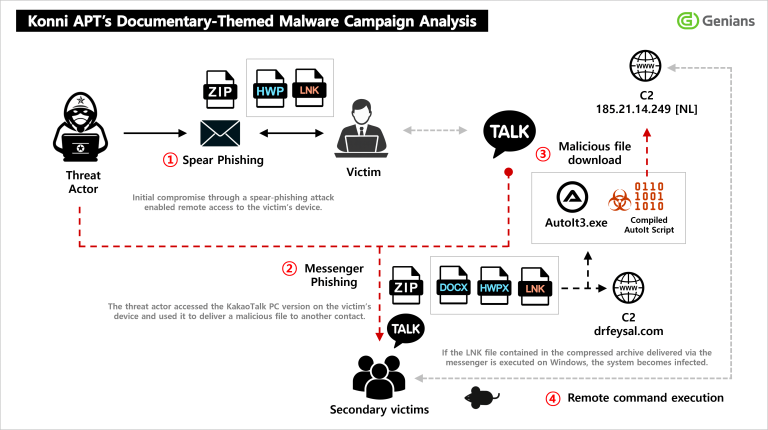
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.

StepSecurity uncovers a supply chain attack where a verified GitHub org, dev-protocol, was hijacked to spread malicious Polymarket bots and steal crypto.

Rapid7 exposes a global ClickFix campaign hijacking WordPress sites with fake Cloudflare CAPTCHAs to deliver stealthy infostealers and drain digital wallets.

Aryaka Threat Labs exposes BlackSanta, a Russian-linked malware targeting HR teams with fake resumes to deploy an EDR-killer and steal crypto wallets.

Qualys discovers CVE-2026-3888, a critical Local Privilege Escalation (LPE) flaw in Ubuntu Desktop. Learn how a 30-day time window exposes root access.