 Do Son
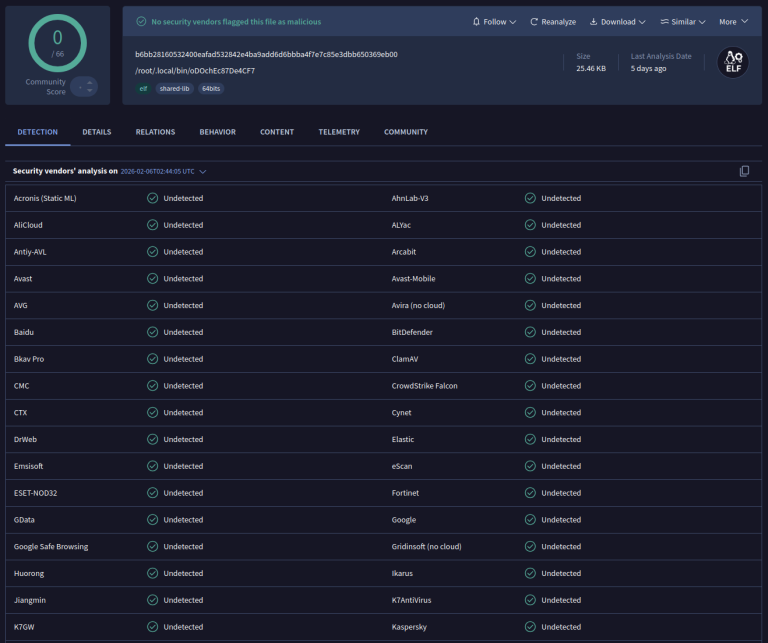
Cyble Research unmasks ClipXDaemon, a C2-less Linux malware that silently hijacks cryptocurrency wallet addresses in X11 clipboard environments.
threat intelligence
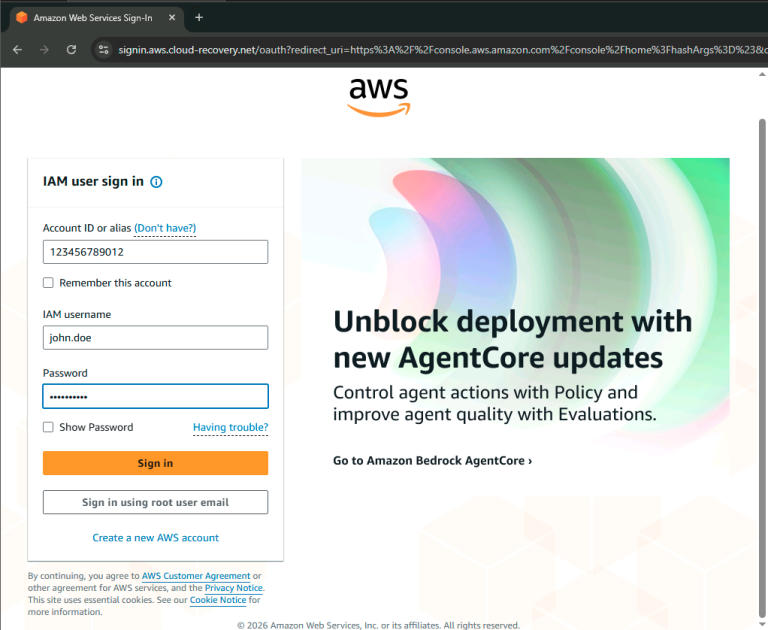
Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.

Researchers uncover a massive campaign by a Vietnamese operator using GitHub and Polygon blockchain smart contracts to distribute the StealC infostealer.

Unit 42 reveals the first real-world cases of Indirect Prompt Injection (IDPI), where hackers weaponize website content to bypass AI security filters.

Researcher @goyaramen reveals how PRC threat actors like Mustang Panda use expired domains and Cloudflare to mask their PlugX C2 infrastructure.

Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.

Cybersecurity researchers uncover OCRFix, a Russian-linked botnet using EtherHiding and fake CAPTCHAs to mask its C2 servers in blockchain smart contracts.

A critical 10.0 CVSS flaw (CVE-2026-20127) in Cisco Catalyst SD-WAN is actively exploited in the wild. A public PoC is now available. Patch immediately!

Microsoft and Europol lead a global coalition to dismantle Tycoon 2FA, a massive AiTM phishing platform that bypassed MFA for over 500,000 organizations.
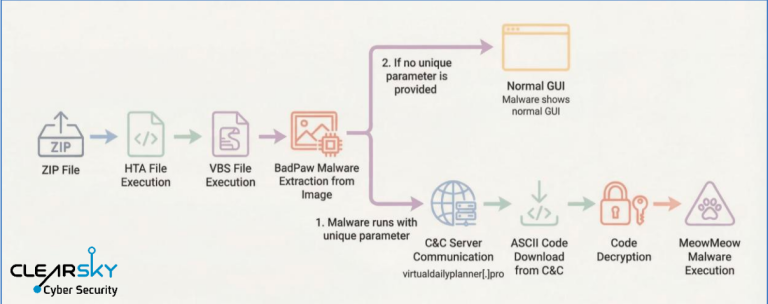
ClearSky uncovers a Russian campaign targeting Ukraine with BadPaw and MeowMeow malware, using steganography and feline decoys for stealthy espionage.

Check Point Research uncovers Silver Dragon, an APT41-linked group using the GearDoor backdoor and Google Drive for stealthy cyber espionage.

Critical authentication flaws (CVE-2026-26288) in Everon's OCPP backend allowed hackers to hijack EV chargers, forcing a complete platform shutdown.

A new Data Abyss report reveals how PRC-affiliated entities systematically exploited U.S. IARPA research to advance China's military capabilities.
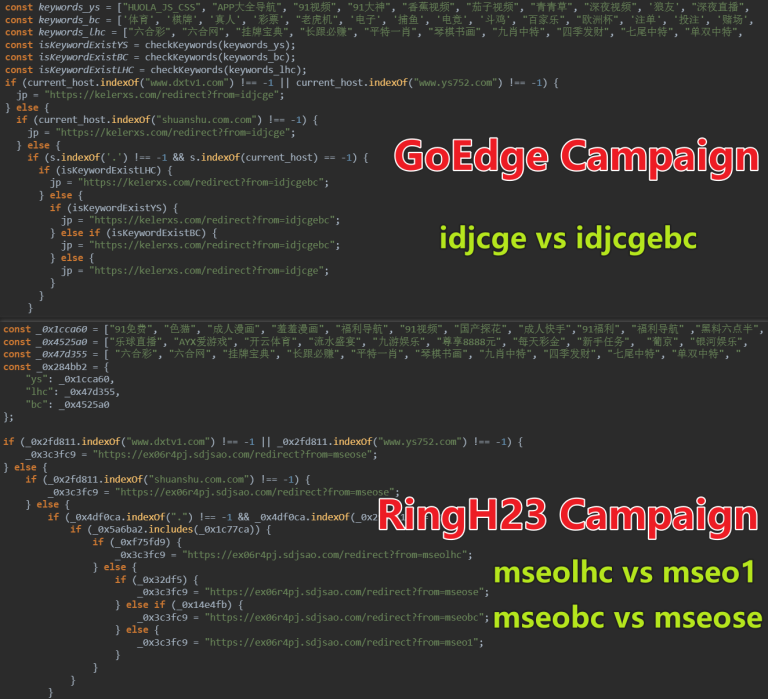
XLab researchers reveal the return of OFAC-sanctioned Funnull. The group is using the new RingH23 framework to hijack CDNs and poison supply chains.

Sophos X-Ops CTU warns of a surge in Iranian hacktivist cyber retaliation, including DDoS and targeted doxxing, following Operation Epic Fury.
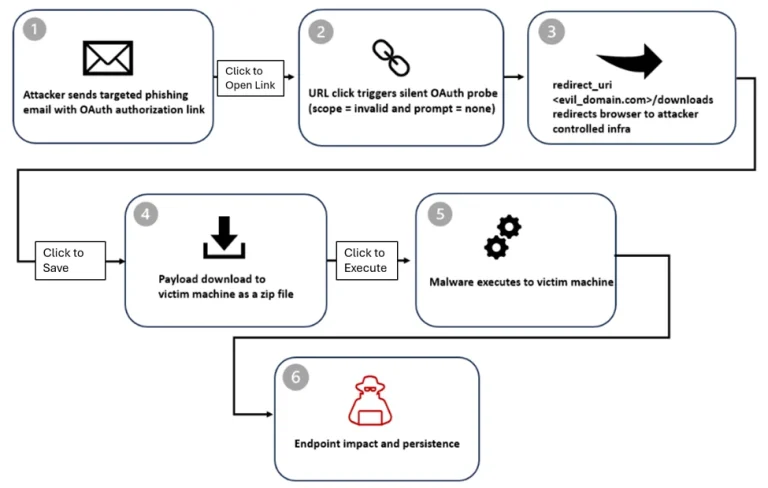
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.
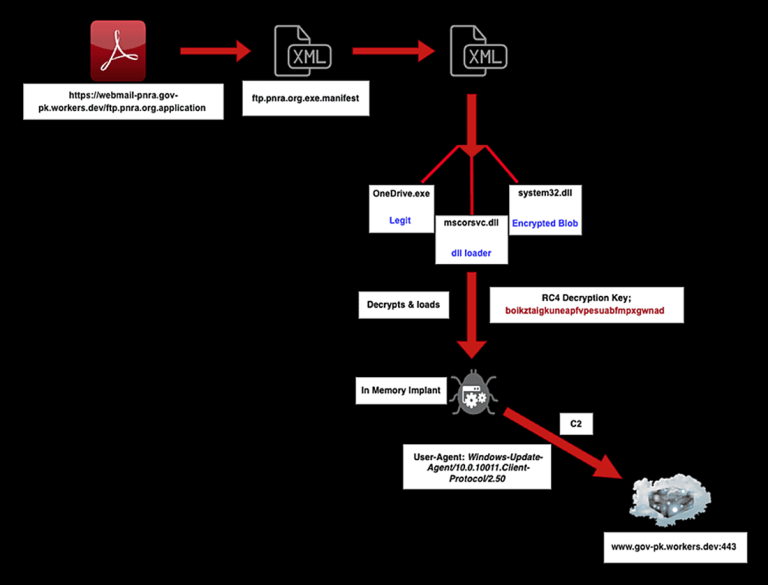
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.

Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

Unit 42 details the cyber fallout of Operation Epic Fury. Despite internet blackouts, autonomous hacktivists claim breaches of Israeli defense networks.