 Do Son
Group-IB analysts have released new intelligence on MuddyWater, the Iranian state-sponsored APT linked to Tehran’s Ministry of...
threat intelligence

CYFIRMA has released a detailed threat intelligence assessment of XillenStealer, an emerging open-source, Python-based malware family that...

GitLab Threat Intelligence has published a detailed analysis of a new malware campaign linked to North Korean...

First emerging in 2011, SmokeLoader (also known as Smoke or Dofoil) has remained one of the most...

Cybercriminals are increasingly relying on malware loaders to gain initial access, evade defenses, and deliver sophisticated payloads....

Okta Threat Intelligence has published a detailed analysis of VoidProxy, a previously unreported Phishing-as-a-Service (PhaaS) platform that...

Threat analysts at Silent Push have identified dozens of previously unreported domains tied to Salt Typhoon, a...

Cyfirma’s Threat Intelligence team has released a technical analysis of Inf0s3c Stealer, a Python-based information grabber designed...

Researchers at CYFIRMA have released an in-depth analysis of a newly observed Windows malware family dubbed the...

Researchers at DomainTools have uncovered a persistent SpyNote Android Remote Access Trojan (RAT) campaign, where threat actors...

Recently, threat hunters at Huntress observed two separate incidents involving a new ransomware variant dubbed Cephalus. The...
The Cybersecurity and Infrastructure Security Agency (CISA) has added three new vulnerabilities to its Known Exploited Vulnerabilities...

Security intelligence firm GreyNoise has sounded the alarm over a massive spike in Microsoft Remote Desktop (RDP)...
Droppers—seemingly harmless apps that secretly deliver malware—have long been a key part of Android cybercrime. But according...

The Pakistan-linked threat group APT36—also known as Transparent Tribe, Mythic Leopard, Earth Karkaddan, or Operation C-Major—has re-emerged...

Last week, the leak site DDoSecrets.com published a data dump allegedly from a workstation of a threat...

The threat landscape in South Asia has taken a new turn with the resurgence of APT36 (Transparent...

The Android ecosystem continues to face persistent threats from sophisticated banking trojans. The Zscaler ThreatLabz team, which...

FortiGuard Labs has been closely tracking a stealthy new malware strain known as Gayfemboy. Initially disclosed by...

A new ransomware strain has entered the cybercrime marketplace, blending technical sophistication with aggressive marketing. Researchers at...

The open-source ecosystem has once again been exploited to distribute malicious software. Socket’s Threat Research Team has...
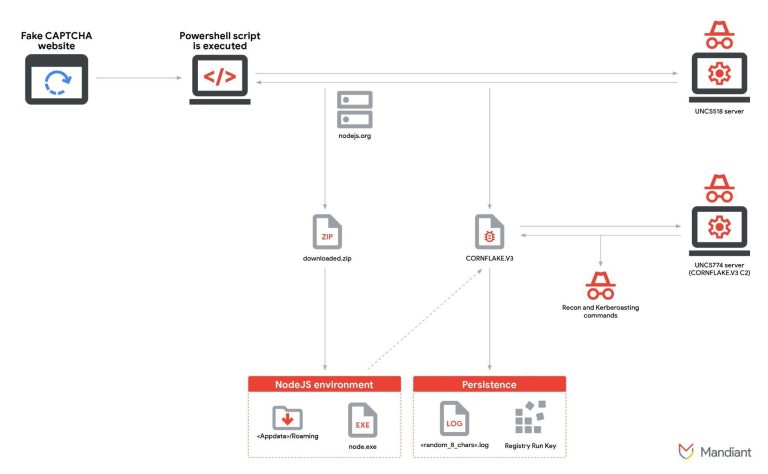
Mandiant researchers have uncovered a sophisticated cybercrime operation where compromised websites are weaponized with fake CAPTCHA pages...