
 Do Son
Unit 42 exposes CL-STA-1087, a suspected Chinese state-sponsored cyber espionage group using custom backdoors to infiltrate Asian military networks.
threat intelligence

Trend Micro exposes KongTuke's new "CrashFix" tactic, which tricks enterprise users via fake Chrome errors into deploying the fileless modeloRAT backdoor.

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.

Splunk warns of a high-severity RCE flaw (CVE-2026-20163) in its REST API. Attackers with edit_cmd rights can execute arbitrary commands. Patch immediately.
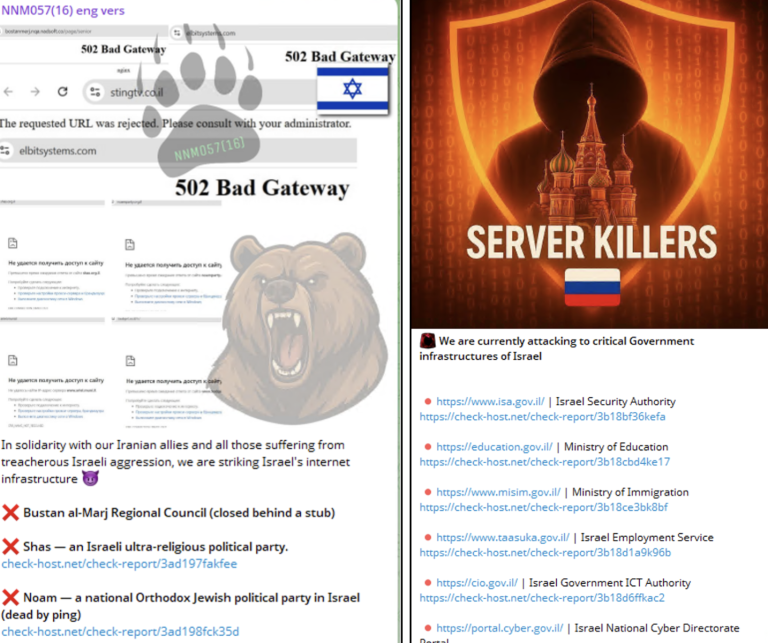
Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.
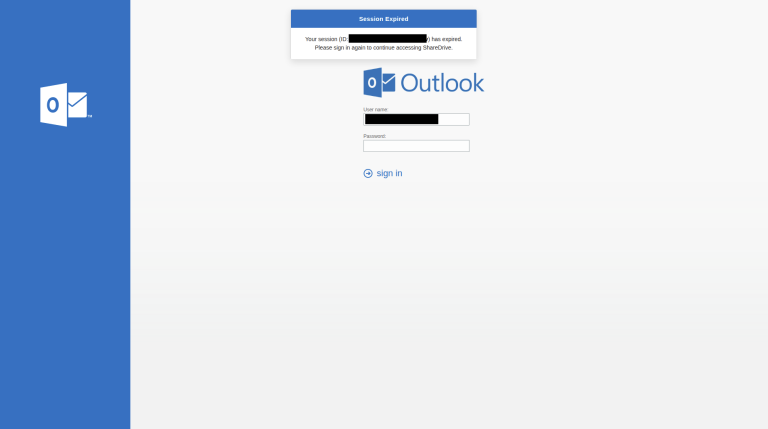
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.
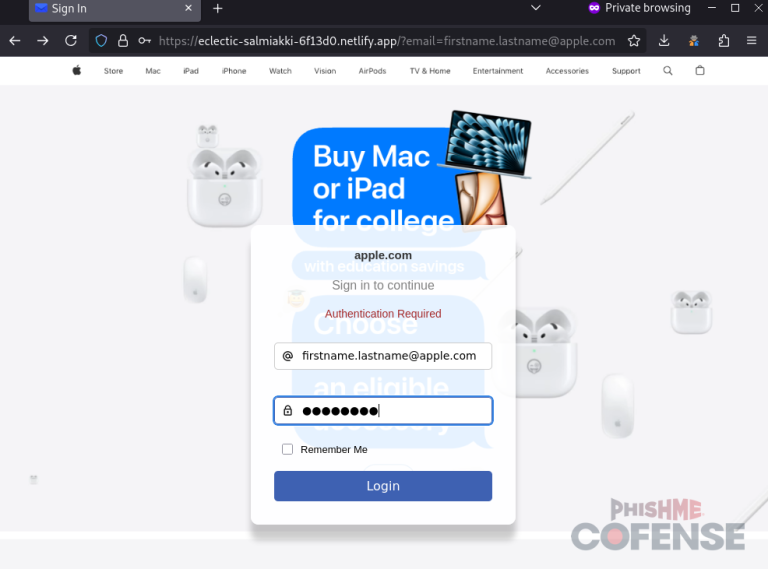
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.
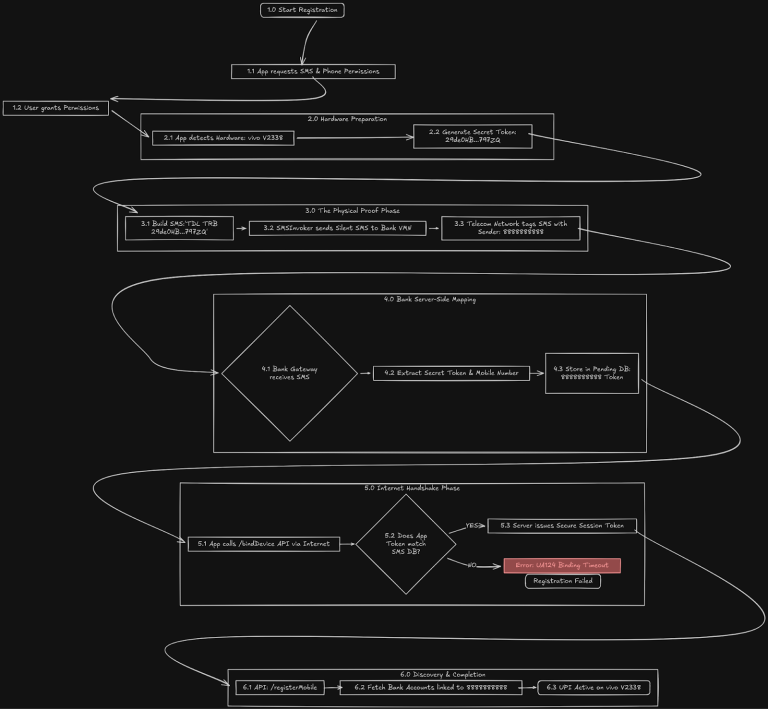
CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.
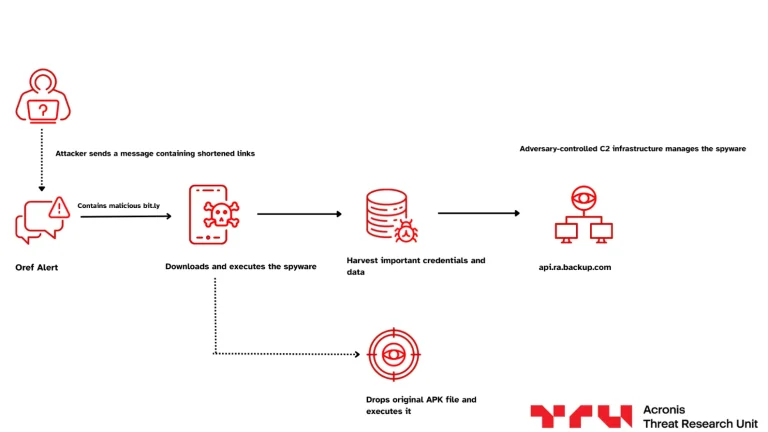
Acronis TRU uncovers a trojanized Red Alert rocket warning app targeting Israelis. Linked to APT-C-23, this Android malware steals data while alerting users.
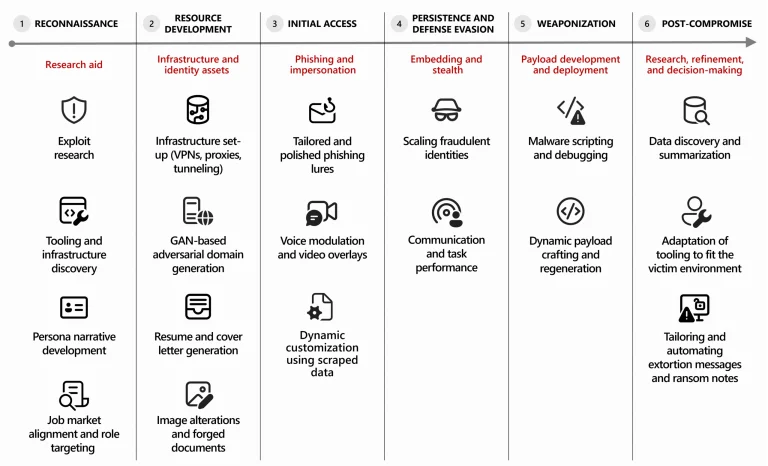
Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.
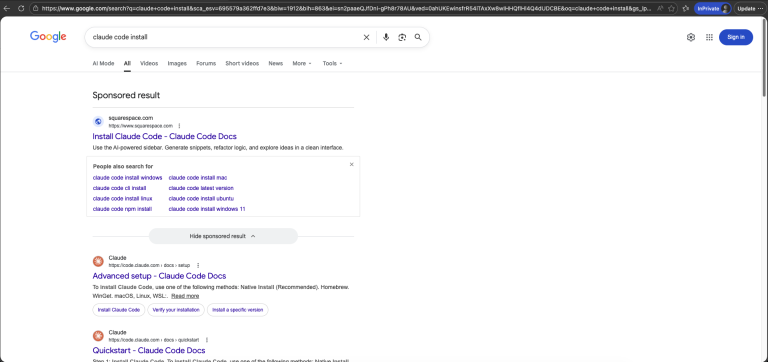
Hackers are targeting AI developers with a fake Claude Code "InstallFix" malvertising campaign, using malicious terminal commands to drop Amatera malware.

Zscaler ThreatLabz reveals a surge in Middle East conflict-themed cyberattacks, uncovering 8,000+ malicious domains, LOTUSLITE backdoors, and scams.
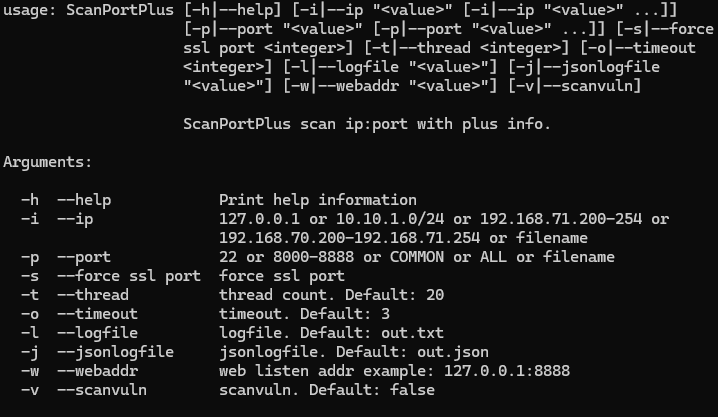
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Dutch intelligence (MIVD/AIVD) warns of a global campaign using social engineering to silently hijack Signal and WhatsApp accounts of high-profile targets.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.

Discover how attackers use shadow archives (CVE-2026-0866) to bypass AV and EDR by malforming ZIP metadata, keeping malware hidden but executable.
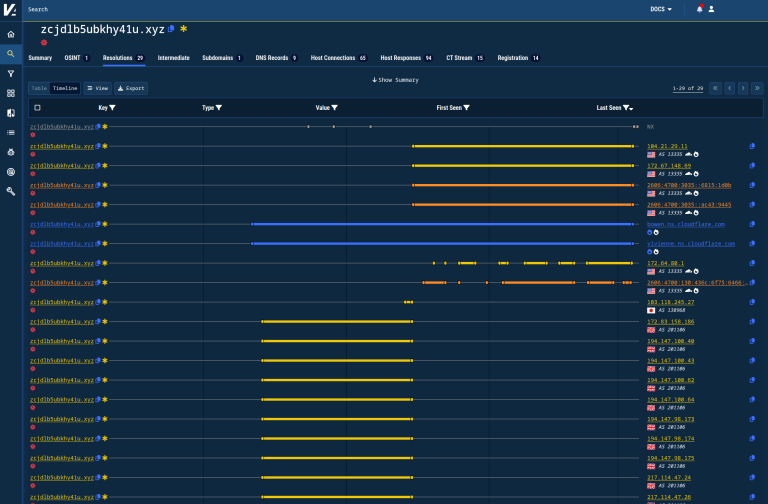
Validin reveals how the Coruna iOS exploit kit evolved from targeted surveillance to mass crypto-draining and geopolitical watering hole attacks.
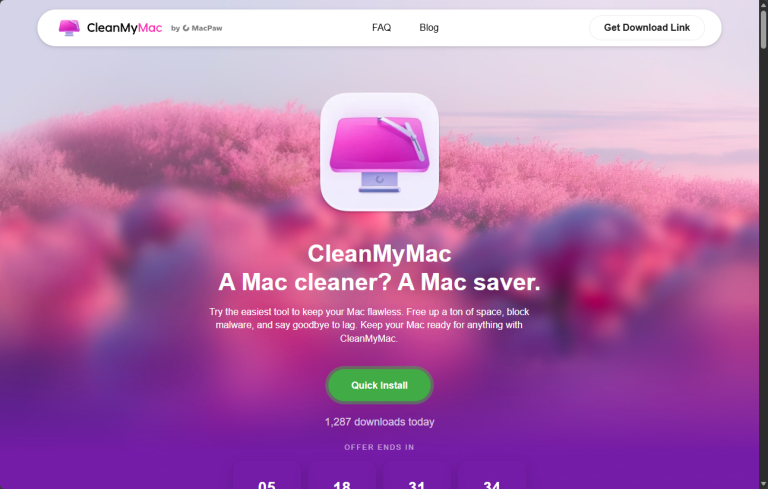
A fake CleanMyMac website is using ClickFix tactics to trick macOS users into installing SHub Stealer, a potent malware targeting passwords and crypto.

A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.
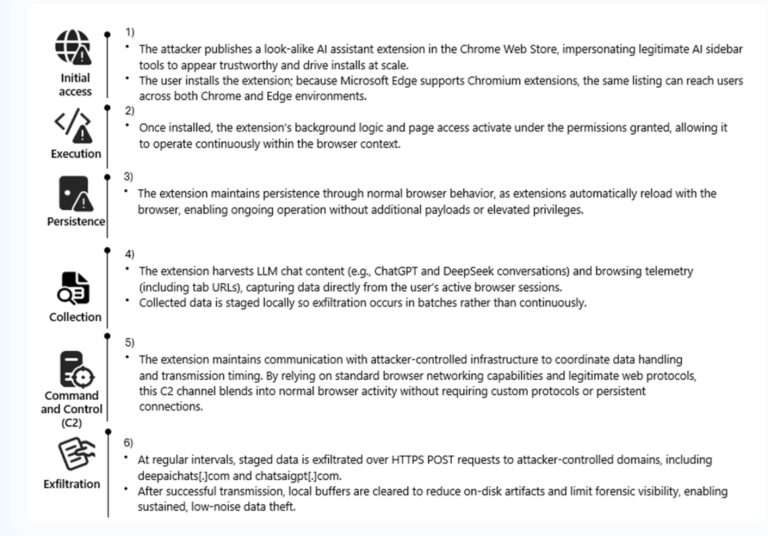
Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.
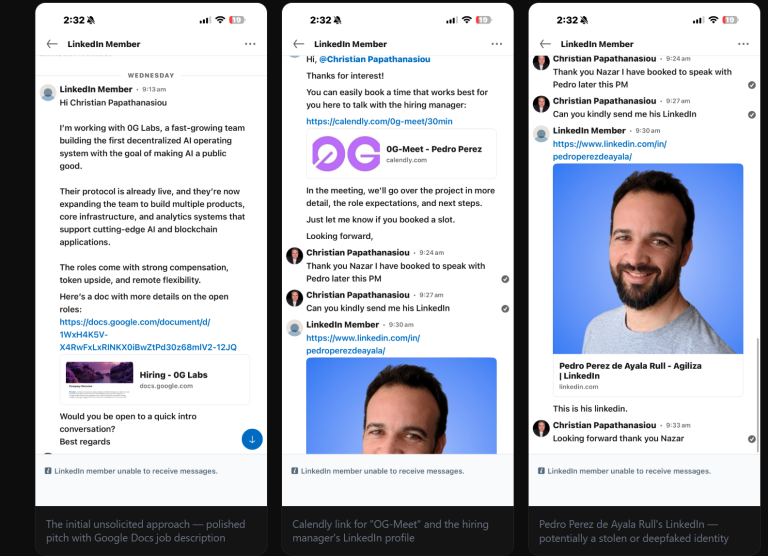
A fake LinkedIn recruiter and a poisoned GitHub repo: See how a CEO uncovered the North Korean "Contagious Interview" malware targeting Web3 developers.