
 Do Son
Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.
threat intelligence
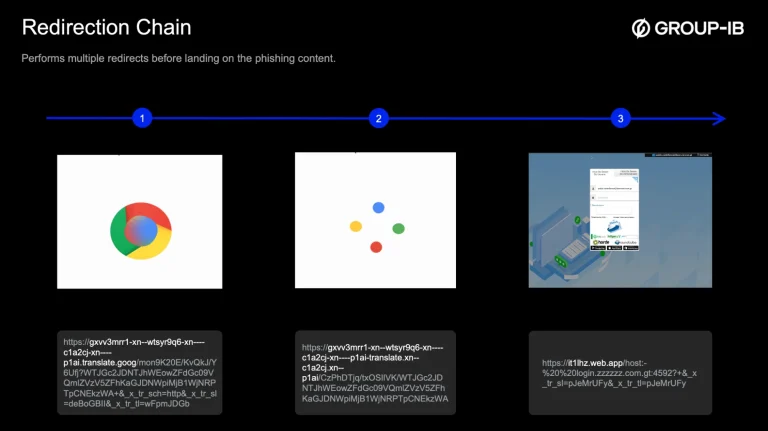
Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.

GreyNoise detects a coordinated surge in SonicWall reconnaissance. With over 84,000 scans, attackers are mapping VPNs for Akira and Fog ransomware strikes.
Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.

Researcher @goyaramen exposes "ARXON," an AI-automated pipeline using LLMs to manage simultaneous global attacks on Fortinet devices. The future of scale is here.
FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.
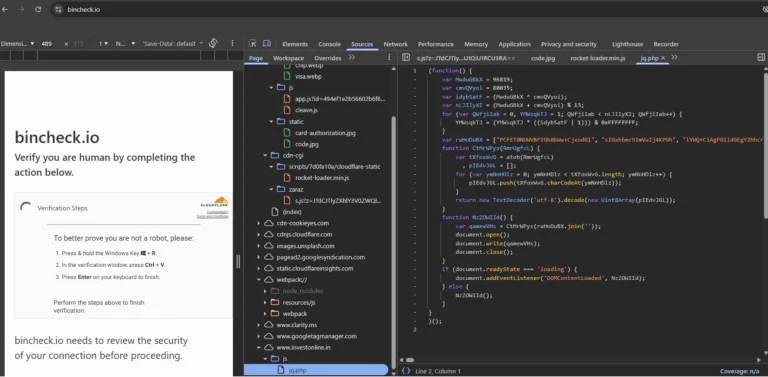
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.
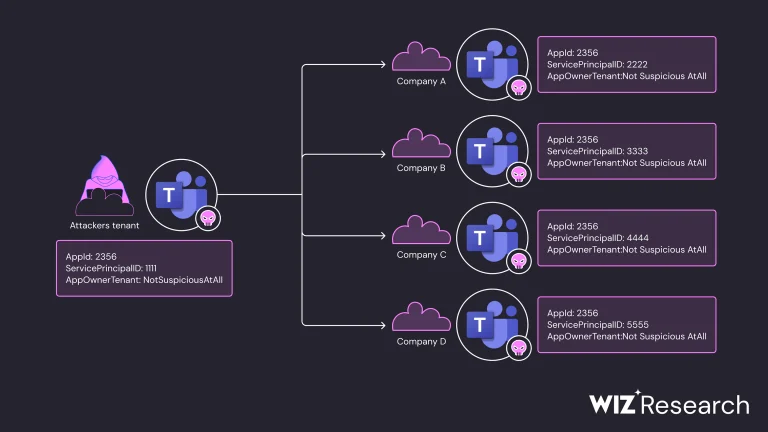
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
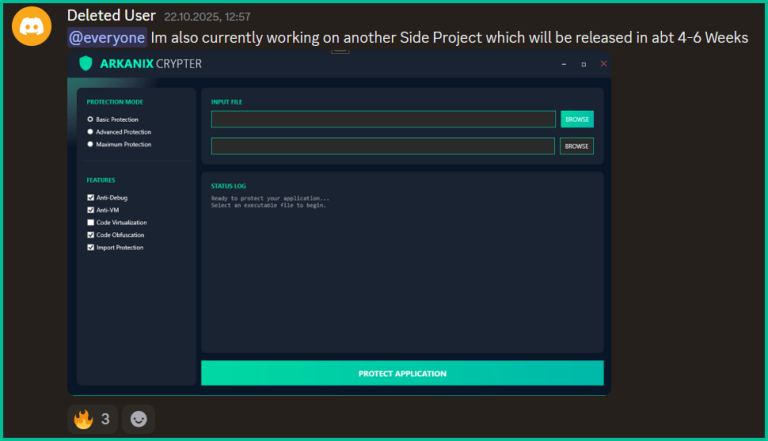
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
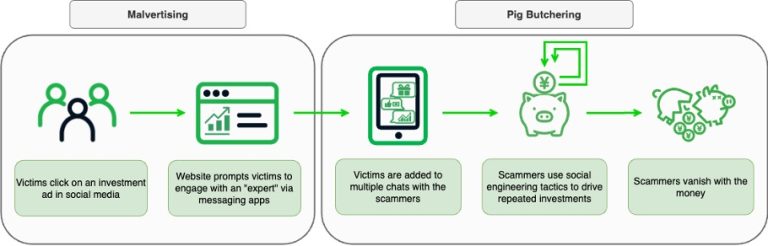
Infoblox Threat Intel exposes a highly scalable hybrid scam merging automated malvertising with "pig butchering" to drain global crypto investors' funds.

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.

Silent Push's Traffic Origin technology strips away VPN masks to reveal the true location of threat actors. Detect North Korean & Russian proxies now.
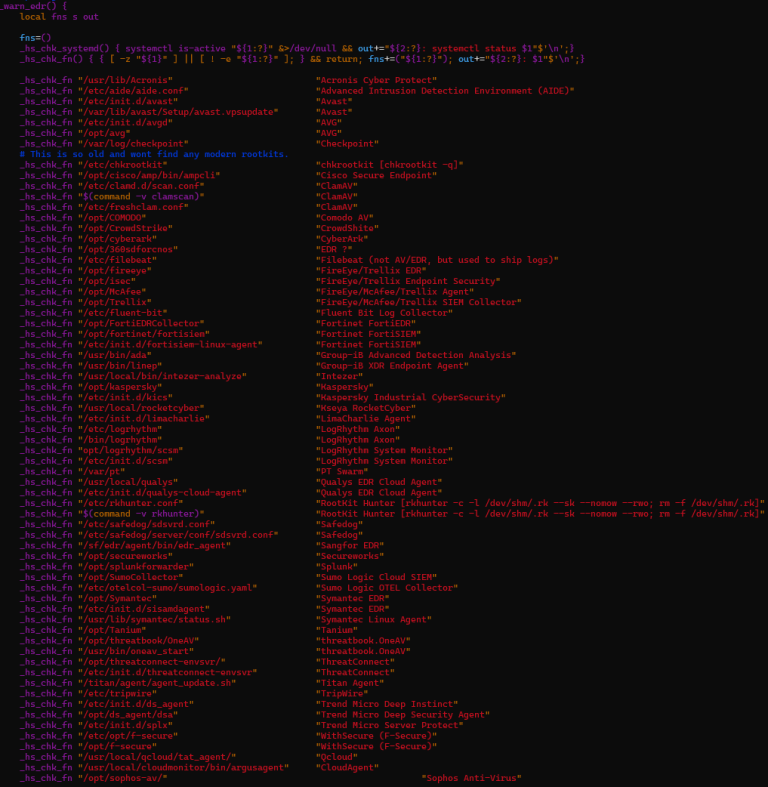
Cyble uncovers "ShadowHS," a fileless Linux malware weaponizing hackshell. It uses GSocket tunneling to evade firewalls and kill rival bots.

Team Cymru exposes the carding supply chain: How criminals use the Soviet .su domain and bulletproof hosting to run resilient fraud markets.

Russian group BlueDelta targets energy researchers in Europe & Middle East. Learn how they abuse free web services for credential harvesting.

Attackers exploit complex mail routing to spoof "internal" emails using Tycoon2FA. Learn how to fix misconfigured DMARC policies and stop the breach.

Nearly 1M users compromised: Discover how the popular Office Assistant tool uses Mltab malware to hijack browsers, steal data, and exploit digital signatures.

CloudSEK’s TRIAD unmasks Silver Fox APT, a China-linked group using Valley RAT to target India while hiding behind misattributed tax phishing lures.