
 Do Son
The EU Council hits Chinese and Iranian cyber threat actors with severe sanctions for hacking critical infrastructure and spreading Olympic disinformation.
threat intelligence

Uncontrolled access to weaponizable AI empowers both cybercriminals and state-sponsored actors. Learn how defenders can prepare for this emerging threat.

A critical 9.8 CVSS vulnerability (CVE-2026-21994) in Oracle's Edge Cloud Infrastructure Toolkit allows unauthenticated remote attackers a total takeover.
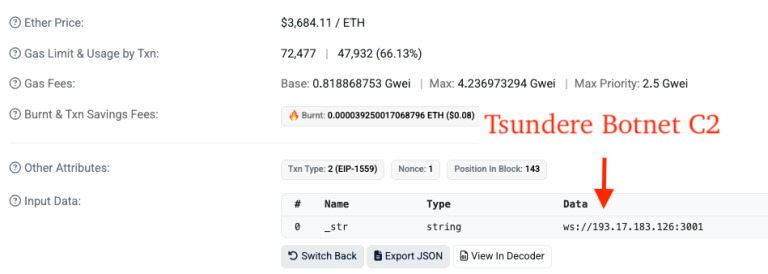
eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

Bishop Fox publicly disclosed details of a critical 9.1 CVSS zero-click SQL injection in FortiClient EMS (CVE-2026-21643). Patch to 7.4.5 immediately.

 ddos-admin
Discover CVE Watchtower's new enterprise suite featuring 30-day threat analytics, predictive EPSS scoring, Jira/ServiceNow webhooks, and a private REST API.

Socket Research exposes how GlassWorm malware abuses Open VSX dependencies for transitive delivery of an RCE backdoor using Solana blockchain dead drops.

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.

Microsoft Defender Experts warn of Storm-2561 using SEO poisoning to distribute fake enterprise VPN clients like Pulse Secure, stealing user credentials.

CISA adds a Wing FTP Server flaw (CVE-2025-47813) to its KEV catalog. The actively exploited cookie vulnerability exposes internal server paths. Update now.

OFAC sanctions a North Korean IT worker network and global facilitators for defrauding U.S. businesses of nearly $800M to fund the regime's WMD programs.
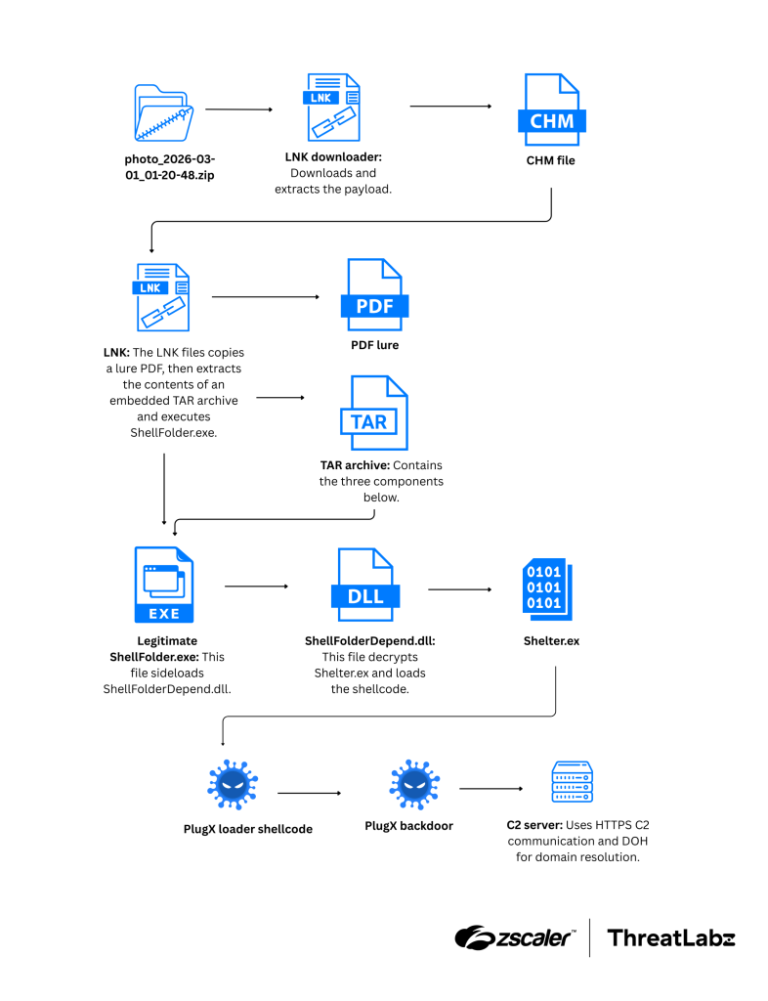
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.
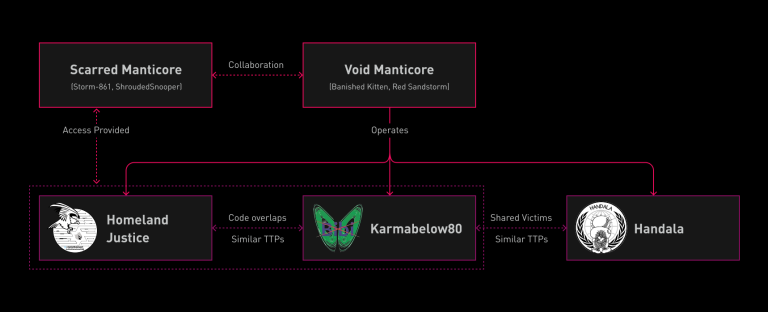
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.
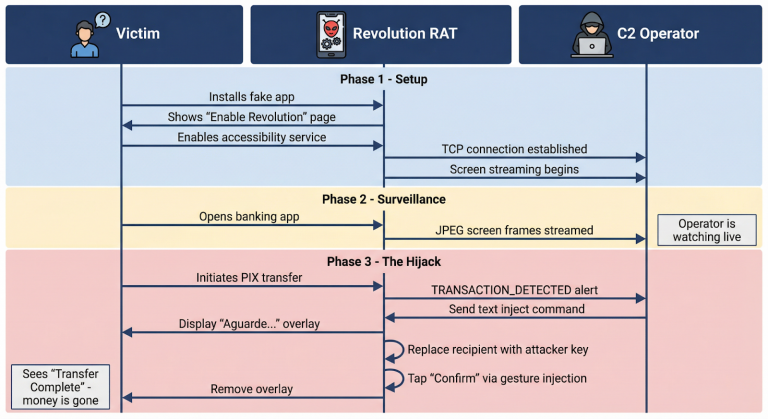
Zimperium's zLabs exposes PixRevolution, a novel Android banking trojan using real-time surveillance to hijack Brazil's PIX instant payments.
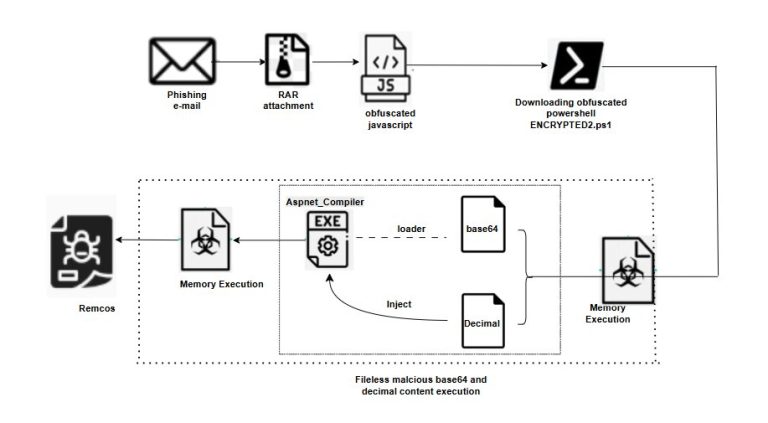
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.
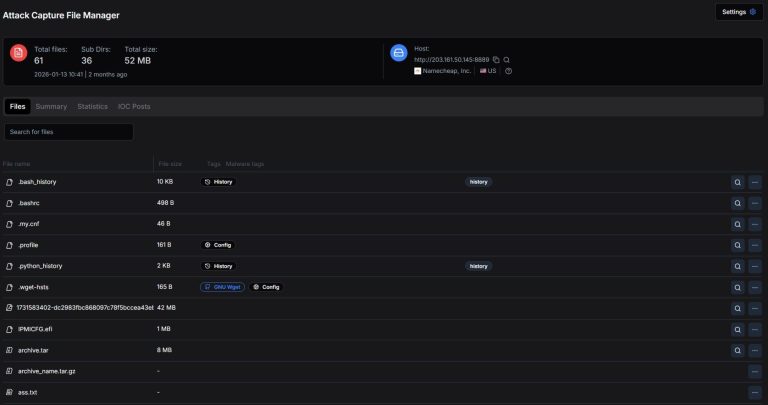
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.
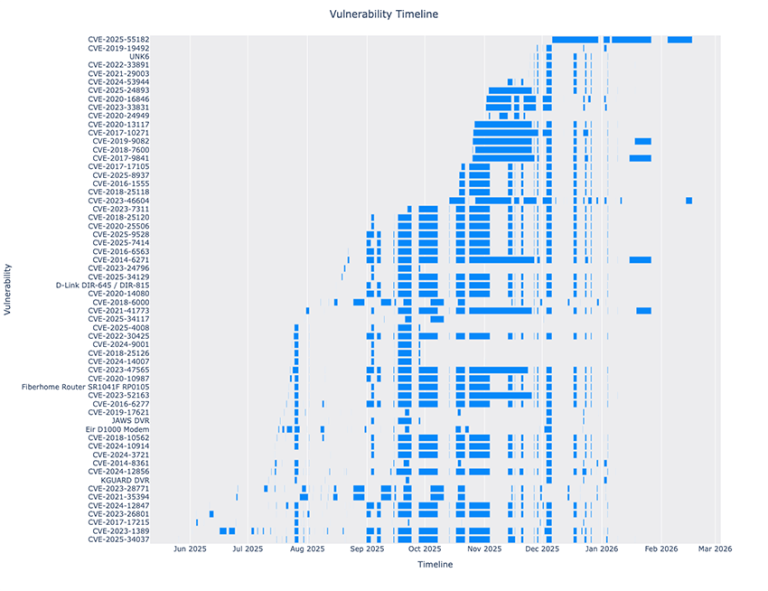
BitSight exposes RondoDox, a relentless IoT botnet using a "shotgun approach" with 174 exploits to hijack residential devices for massive DoS attacks.
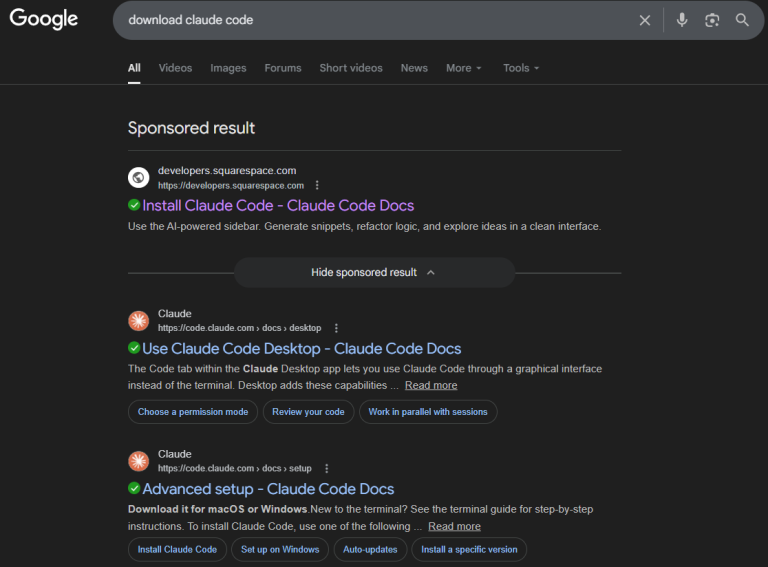
Bitdefender exposes a malvertising campaign targeting developers searching for Claude Code. Fake Google Ads deploy Windows stealers and macOS backdoors.

BlueVoyant exposes Blitz Brigantine's new tactics: using email bombing, Microsoft Teams lures, and covert DNS MX tunneling to deploy AOBackdoor.
Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground
Check Point Research reveals Iranian state hackers (Void Manticore) are weaponizing RaaS and criminal malware like Rhadamanthys for plausible deniability.
Black Lotus Labs uncovers KadNap, a stealthy P2P botnet infecting over 14,000 Asus routers to fuel the Doppelgänger dark web proxy network.

SentinelOne DFIR reveals how attackers exploit FortiGate NGFW flaws to extract credentials, abuse Active Directory, and establish persistent network access.