 Do Son
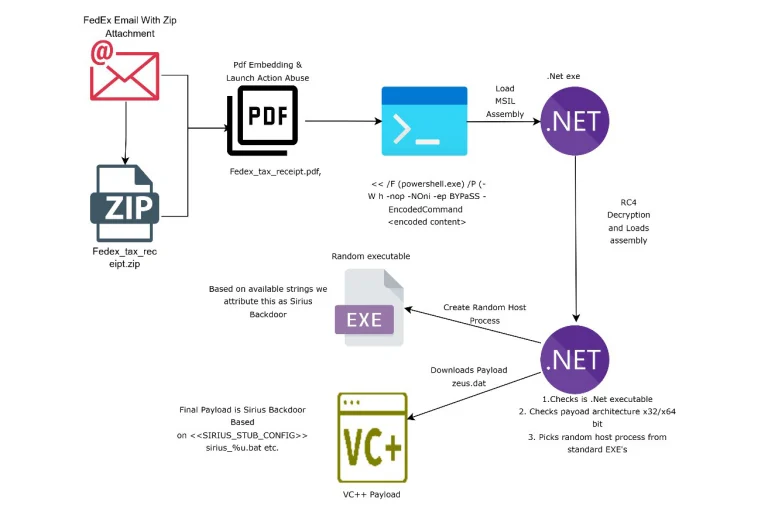
Trellix uncovers the Sirius Backdoor in fake FedEx tax invoices. See how the fileless Sirius Backdoor blinds EDRs and survives Windows OS resets.
Trellix

Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.
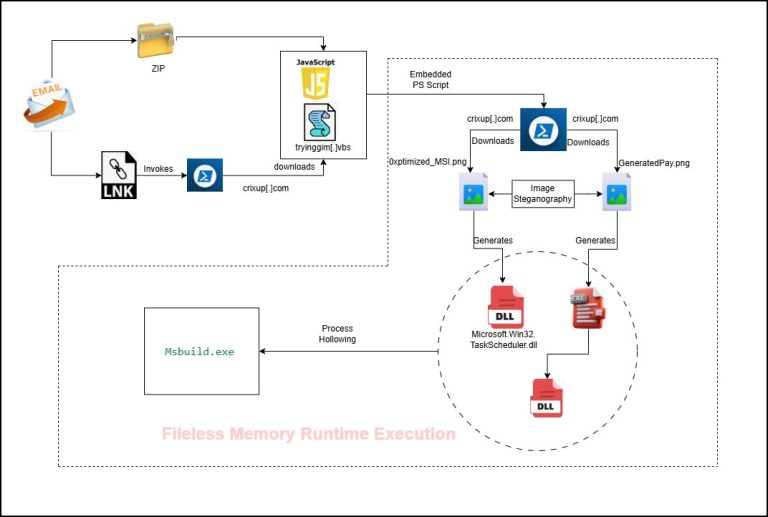
Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.
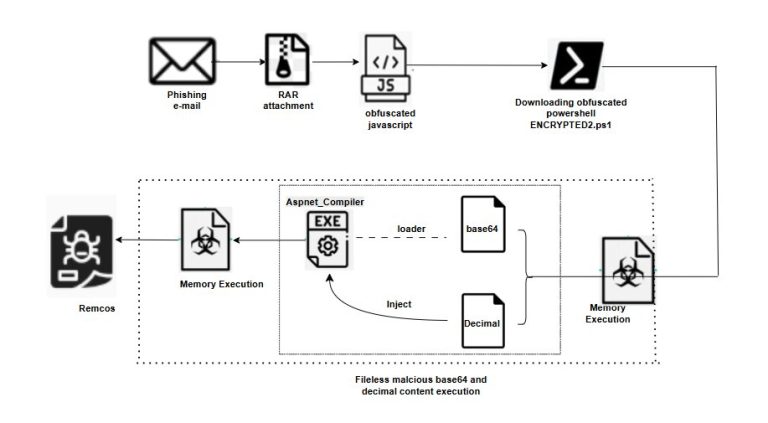
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.

APT28 (Fancy Bear) weaponized CVE-2026-21509 in 24 hours to target NATO. New "BeardShell" and "NotDoor" malware steals emails. Patch Office now.

Attackers exploit legitimate ahost.exe via DLL sideloading to deploy RATs & stealers. Trusted dev utility bypasses security scanners. Watch out.

Trellix warns: "Browser-in-the-Browser" phishing creates perfect fake Facebook login pop-ups. Learn how this invisible trap steals credentials.

New CrazyHunter ransomware targets healthcare with BYOVD tactics and rapid encryption. Trellix reveals how this "greedy" threat cripples hospitals.

XWorm V6.0 has resurfaced with 35+ plugins, including ransomware functionality. The modular RAT uses stealth injection and obfuscated PowerShell to bypass AMSI.

A new report reveals a sophisticated XWorm backdoor campaign that uses .lnk files and a multi-stage infection chain to gain stealthy and persistent control of Windows systems.
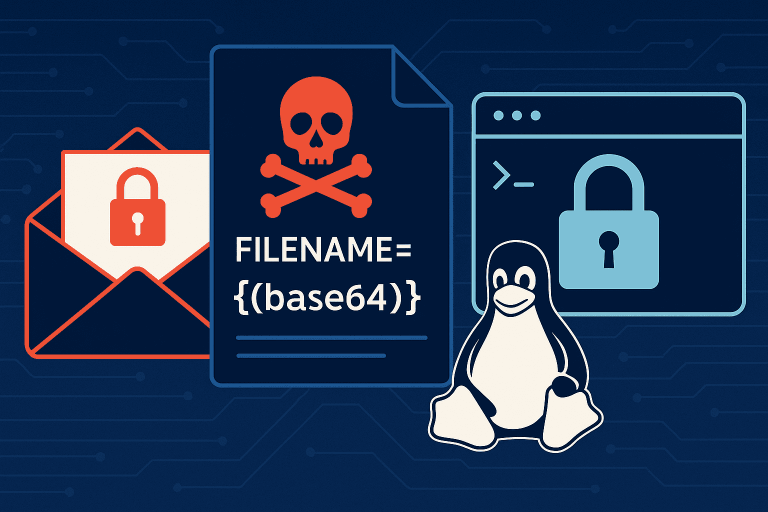
A new report reveals a dangerous Linux malware campaign that uses malicious filenames to execute a stealthy, fileless attack without the victim's knowledge.

A new report reveals a North Korean espionage campaign targeting embassies with spear phishing and a sophisticated C2 channel hidden on GitHub.

Trellix uncovers 0bj3ctivityStealer, a sophisticated info-stealer using phishing, custom PowerShell, and steganography to evade detection and exfiltrate sensitive data.

Trellix has uncovered SquidLoader, a highly obfuscated malware targeting Hong Kong financial institutions to deploy Cobalt Strike beacons for persistent control.

DoNot APT (APT-C-35) expands its cyber-espionage to a European foreign affairs ministry, using spear-phishing with Google Drive links to deliver the LoptikMod backdoor.

Trellix uncovers "OneClik," a sophisticated APT campaign abusing Microsoft ClickOnce and AWS cloud services to deploy Go-language backdoors, targeting energy, oil, and gas sectors.

Trellix analysis reveals Lumma Stealer's latest tactics: code obfuscation, API hashing, ETW evasion, anti-VM. Learn how this InfoStealer avoids detection.

These vulnerabilities, identified as CVE-2024-11481 (CVSS score 8.2) and CVE-2024-11482 (CVSS score 9.8), affect ESM version 11.6.10

CVE-2024-5671 and CVE-2024-5731 leave unprotected systems vulnerable to remote code execution and unauthorized access