 Do Son
CVE-2026-63077 is a critical TeamCity RCE rated CVSS 9.8. Unauthenticated attackers can run OS commands. Update TeamCity On-Premises to a fixed build.
unauthenticated
A critical Feast Feature Server flaw (CVE-2026-23537) lets unauthenticated attackers perform arbitrary file write and risk remote code execution. Act now.

GeoServer patched a High-severity XXE flaw (CVE-2025-58360, CVSS 8.2) in its WMS GetMap operation. The flaw allows unauthenticated remote attackers to read arbitrary files and perform SSRF. Update to v2.27.0.

A critical flaw (CVE-2025-58434) in FlowiseAI allows unauthenticated attackers to hijack any account. The bug has a CVSS 9.8 score, and a PoC has been released.

A critical flaw in Ruijie Reyee RG-ES series switches allows unauthenticated remote attackers to modify login credentials and gain full admin access. CVE-2025-56752 has a CVSS 9.4 score.

Dell has released a critical security advisory for ThinOS 10, with a CVSS 9.6 flaw that allows unauthenticated remote attackers to bypass protection mechanisms.

Fortinet released a critical patch for FortiWeb (CVE-2025-25257). This unauthenticated SQL injection flaw allows remote code execution. PoC Releases!

Fortinet released a critical patch for FortiWeb (CVE-2025-25257, CVSS 9.6). This unauthenticated SQL injection flaw allows remote code execution; update immediately!

Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.

A critical RCE flaw (CVE-2025-47812, CVSS 10.0) in Wing FTP Server allows unauthenticated attackers to execute arbitrary Lua code via NULL byte injection, compromising the server
A critical flaw (CVE-2025-6561, CVSS 9.8) in Hunt Electronic DVRs allows unauthenticated remote attackers to access configuration files and obtain plaintext admin credentials.
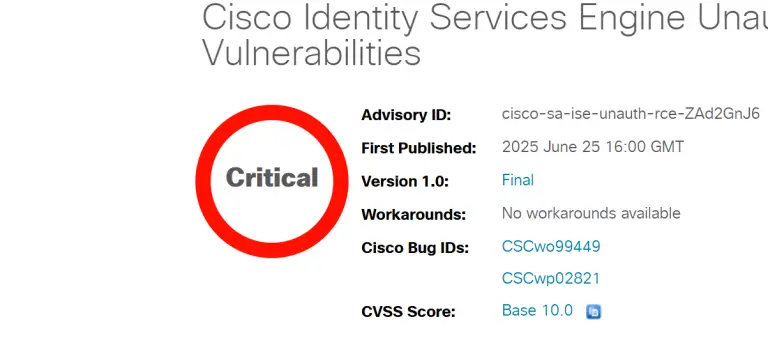
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.

A critical flaw (CVE-2025-48703) in CentOS Web Panel allows unauthenticated RCE via authentication bypass and command injection, risking over 200,000 servers.

JPCERT/CC warns of critical flaws in ELECOM wireless LAN routers, including unauthenticated RCE (CVSS 9.8) via Telnet/SOAP. Many affected models are unsupported; replace them immediately.

A critical flaw (CVE-2025-34037, CVSS 10.0) in Linksys E-Series routers allows unauthenticated remote command injection. TheMoon worm is actively exploiting it to infect devices.

A critical flaw (CVE-2025-52562, CVSS 10.0) in Convoy KVM panel allows unauthenticated remote code execution via directory traversal.

A critical path traversal flaw (CVE-2025-34022, CVSS 9.3) in Selea TARGA ANPR cameras allows unauthenticated remote access to sensitive files. PoC is public

A critical RCE flaw (CVE-2025-49132, CVSS 10.0) in Pterodactyl game server panel allows unauthenticated arbitrary code execution. Malicious actors are already exploiting it.

Unauthenticated RCE flaw in Mitel SIP phones (CVSS 9.8) lets attackers gain root via ringtone upload. Exploit PoC shows full system compromise.

A critical Cisco IOS XE WLC flaw (CVE-2025-20188, CVSS 10) allows unauthenticated RCE via arbitrary file uploads. Update or disable Out-of-Band AP Image Download.

A critical Tenda W18Ev2 router flaw allows unauthenticated RCE via admin password change. PoC available, no patch yet.

Mimo (Hezb) is exploiting an unauthenticated RCE (CVE-2025-32432) in Craft CMS to deploy webshells, cryptominers, and proxyware. Patch now!