 Do Son
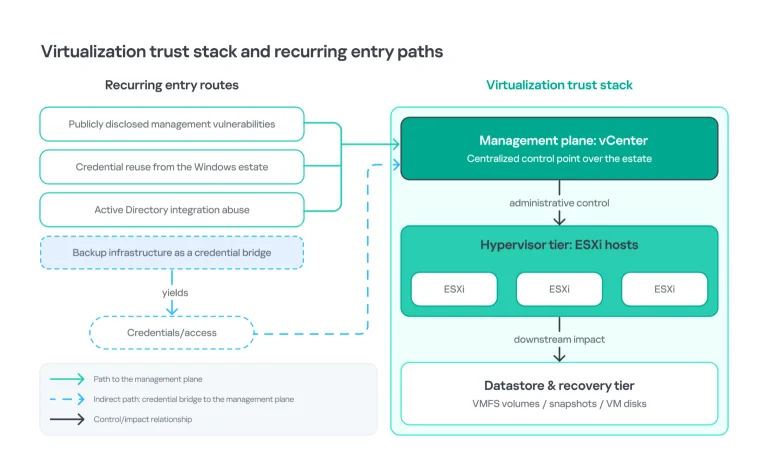
Kaspersky GERT analyzes a BlackNevas ESXi ransomware attack. See how the VMware BlackNevas ESXi ransomware abused vCenter Host Profiles to wipe VMs.
VMware ESXi
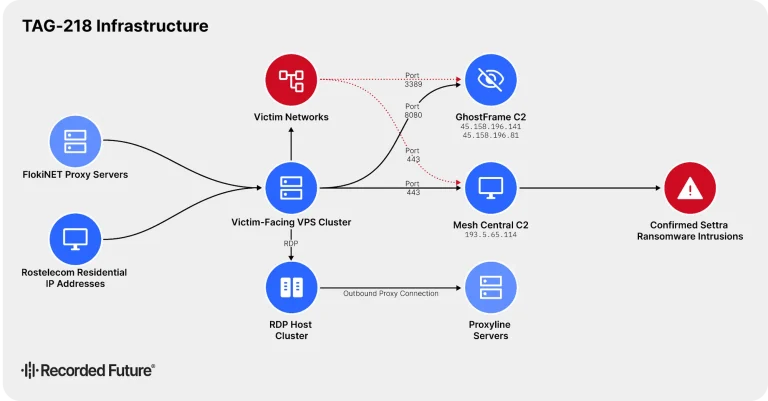
Recorded Future uncovered the GhostFrame ESXi implant Settra ransomware framework used by TAG-218 to hijack hypervisors and steal VM credentials.
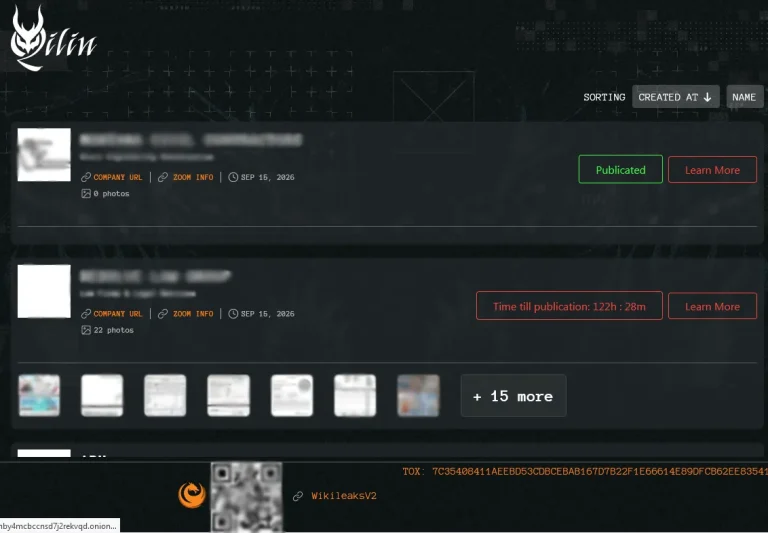
Acronis analyzes Qilin ransomware after 900+ attacks in 2026. See how ESXi Qilin ransomware scripts hijack VMware hosts and leak data on WikiLeaksV2.
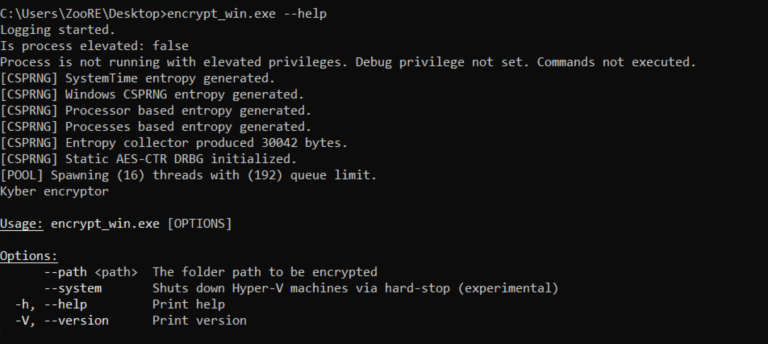
Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.

Huntress exposes "VSOCKpuppet" VM escape: Attackers used a hidden zero-day toolkit to breach VMware ESXi hosts and bypass network monitoring.

Akira ransomware is actively exploiting the unpatched/misconfigured SonicWall flaw (CVE-2024-40766) and using the rare "UnPAC the Hash" Kerberos technique for lateral movement.

AhnLab has uncovered Kawa4096, a Go-based ransomware targeting Windows, Linux, and VMware ESXi. The malware uses advanced crypto and covert backup deletion.

AhnLab has uncovered BlackLock, a Go-based ransomware targeting Windows, Linux, and VMware ESXi. The malware uses advanced crypto and covert backup deletion.

SCATTERED SPIDER targets U.S. airlines with ransomware, vishing, and VMware exploits—CrowdStrike warns of a rising threat across cloud identities.
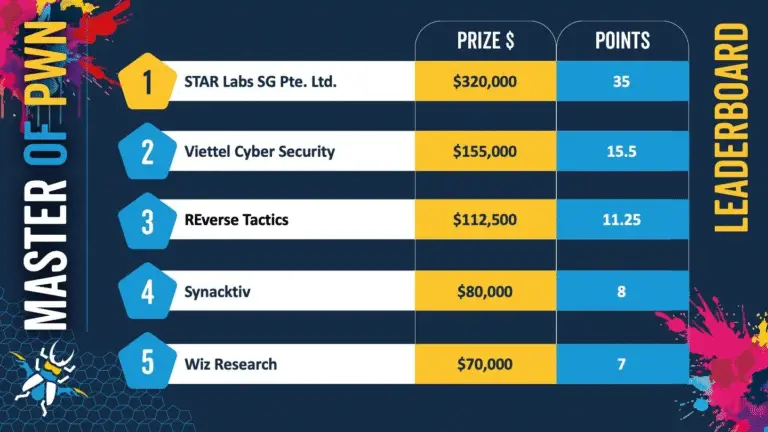
Pwn2Own Berlin saw VMware ESXi and Windows 11 compromised, along with Firefox. Researchers earned over $1M for 30+ zero-day exploits.

Discover the rise of Akira, a highly active Ransomware-as-a-Service (RaaS) group targeting organizations worldwide.

Trend Micro's threat-hunting team has uncovered a new Linux variant of the TargetCompany ransomware, marking a significant escalation

CVE-2024-22273 affects VMware ESXi, Workstation, and Fusion—foundational tools for virtual machine creation and management