 Do Son
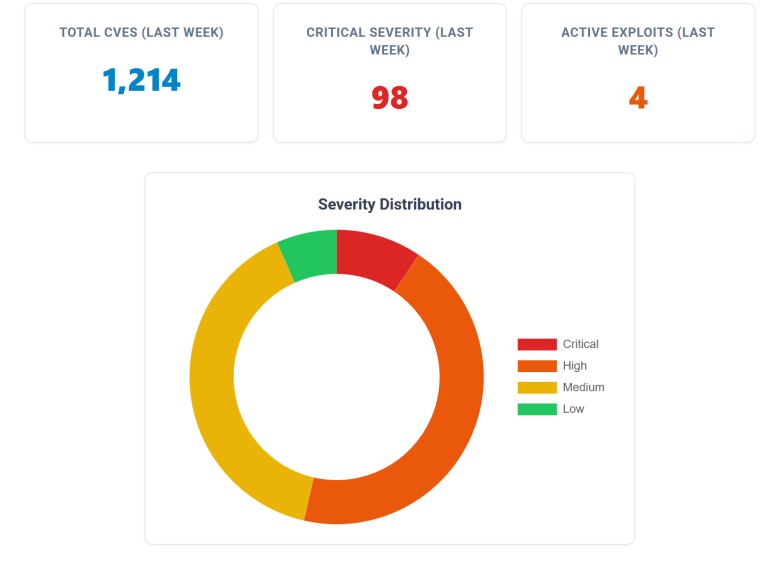
This week's digest: 1,214 new bugs, including active exploits on 2009 Excel fossils and critical 10.0 flaws in new AI/MCP infrastructure. Priority: Patch now.
vulnerability management
Froxlor faces two critical flaws, including a CVSS 10. Learn how path traversal and config injection allow persistent RCE. Patch your server management today!

Faced with a massive surge in CVEs, NIST has overhauled the NVD. Starting April 2026, only high-risk flaws get full analysis. Check the new triage rules.
Google ADK (CVE-2026-4810) faces a critical 9.3 CVSS RCE flaw. Unauthenticated attackers can hijack AI agents on GKE & Cloud Run. Update and redeploy now!
CISA adds 7 active exploits to the KEV catalog, from legacy Office bugs to 2026 Fortinet zero-days. Patch these high-risk flaws now to secure your network.

SAP’s April 2026 updates fix a critical 9.9 CVSS SQL injection in Business Warehouse and 19 other security flaws. Audit your S/4HANA and BPC systems today.

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!

Apache OpenMeetings 9.0.0 fixes critical flaws including hard-coded "remember-me" keys and REST login credential exposure. Secure your video suite today!

Sonatype patches a critical 9.4 CVSS RCE in Nexus Repository 3 (CVE-2026-3199). Secure your supply chain—upgrade to version 3.91.0 immediately!

Apache Tomcat discloses 10 vulnerabilities including encryption bypasses and Kubernetes token leaks. Upgrade now to secure your Java-based web applications.

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!

1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.
CISA adds 5 actively exploited flaws to its KEV catalog, including a critical 10.0 CVSS Craft CMS bug and Apple zero-days linked to DarkSword malware.

 ddos-admin
Discover CVE Watchtower's new enterprise suite featuring 30-day threat analytics, predictive EPSS scoring, Jira/ServiceNow webhooks, and a private REST API.

CISA adds a Wing FTP Server flaw (CVE-2025-47813) to its KEV catalog. The actively exploited cookie vulnerability exposes internal server paths. Update now.
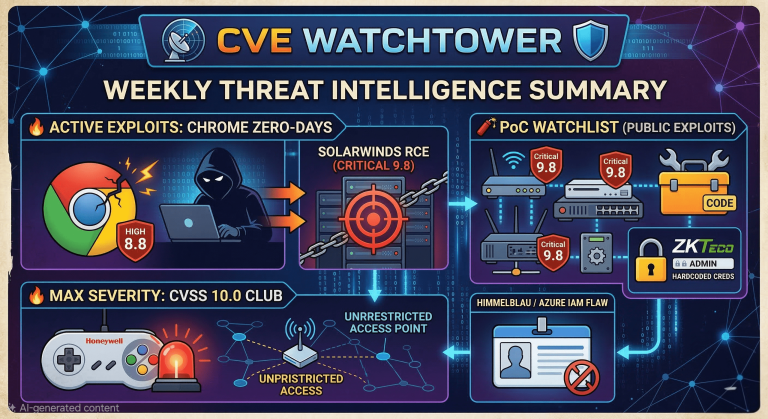
Google Chrome zero-days and a CVSS 10.0 building controller flaw top this week's 1,388 new CVEs. Patch the perimeter before threat actors automate the exploit.

Winter CMS urgently patches a critical 10.0 CVSS privilege escalation flaw (CVE-2026-27591) allowing low-level backend users to gain full system control.

Protect your Spark clusters: Apache Livy 0.9.0 patches two important file access and path traversal vulnerabilities (CVE-2025-60012 & CVE-2025-66249).
Google has finalized its $32B acquisition of Wiz, the largest in its history. Discover how this "code-to-cloud" platform secures AI in a multi-cloud world.
CISA warns of a critical 10.0 CVSS RCE flaw (CVE-2025-68613) in n8n workflow automation. Update to version 1.122.0 immediately to prevent server takeover.

GitLab issues urgent security updates (18.9.2, 18.8.6, 18.7.6) fixing critical XSS (CVE-2026-1090) and DoS flaws. Patch self-managed instances today.

Urgent: WordPress 6.9.2 patches 10 critical security flaws, including XSS, SSRF, and path traversal. Update your site immediately to prevent exploitation.