
 Do Son
Two critical CSF plugin vulnerabilities, CVE-2026-65638 and CVE-2026-65639, allow remote code execution. Patch your ConfigServer firewall immediately.
Vulnerability

Dell patched critical Dell ObjectScale vulnerabilities, led by CVE-2026-70416. Fix these Dell ObjectScale vulnerabilities to stop remote code execution.

GeoVision patched critical GeoVision camera vulnerabilities across its IP cameras. Patch these GeoVision camera vulnerabilities to stop attacks.

Dell patched critical Dell Networking OS10 vulnerabilities, including CVE-2026-63695. Update your Dell SmartFabric OS10 switches to prevent session theft.

GitLab patched critical GitLab vulnerabilities, led by CVE-2026-85706 with a CVSS 10.0 score. Update your server now to protect source code from exposure.

Wiz detected JFrog Artifactory vulnerabilities exploited in the wild. Patch JFrog Artifactory vulnerabilities now to stop remote administrative takeovers.
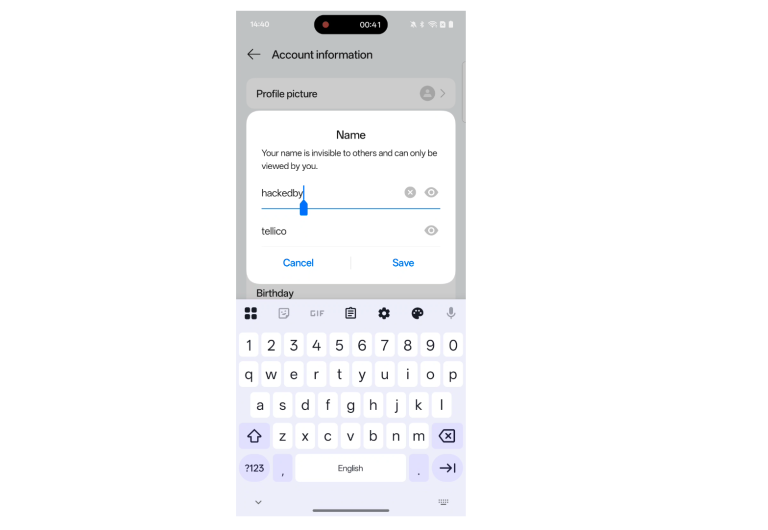
A disclosed OnePlus session takeover vulnerability threatens OnePlus 13R Android security, allowing malicious apps to steal tokens and modify user data.
NVIDIA fixed critical Triton Inference Server vulnerabilities. Patch your Triton Inference Server vulnerabilities now to stop denial of service attacks.
Critical Apache Artemis vulnerabilities, including CVE-2026-67593 and other ActiveMQ Artemis flaws, expose systems to denial of service and data exposure.
Arista released fixes for critical Arista EOS vulnerabilities. Learn how these Arista EOS vulnerabilities impact enterprise switches and edge devices.
Okta fixed critical Okta vulnerabilities across multiple tools. Patch these Okta vulnerabilities today to prevent code execution and authorization bypass.
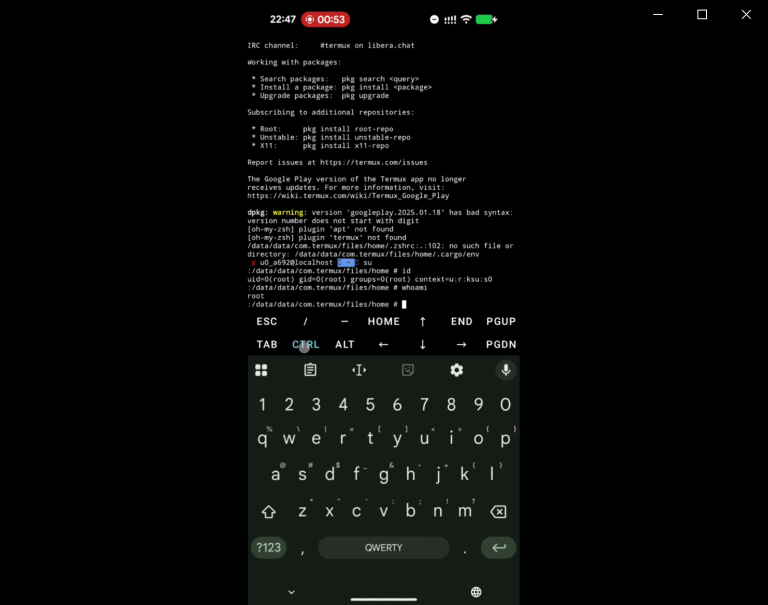
The LSPromise exploit chain provides a 100% success rate for local privilege escalation to root on Android 17. Details and PoC are publicly disclosed.
A new PAN-OS buffer overflow flaw, tracked as CVE-2026-0310, exposes firewalls to remote code execution. Patch your network devices immediately.
Cisco Talos warns of Cisco FMC vulnerabilities actively exploited in the wild. Attackers chain CVE-2026-20079 and CVE-2026-20316 to deploy ransomware.
Check Point fixed critical Check Point VPN vulnerabilities. Update gateways to prevent remote code execution under CVE-2026-85102 and CVE-2026-85103.
Details and PoC for a Cisco Secure Boot bypass vulnerability are public. Learn how this Cisco Secure Boot bypass affects UCS servers and appliances.
The September 2026 Android Security Bulletin patches critical RCE flaws like CVE-2026-28604 in the System component. Update to patch level 2026-09-05.
Four Apache Impala vulnerabilities expose systems to remote code execution and authentication bypass. Upgrade to Impala 4.5.2 to secure your clusters now.
Details and PoC for CVE-2026-84372 are publicly disclosed. This Predis command injection flaw via CRLF smuggling allows complete cluster compromise.
A critical MapLibre XSS vulnerability allows zero-click code execution in 2.7M weekly downloads. Discover how CVE-2026-85061 works and how to patch now.
A critical CVE-2026-67401 cPanel SQL injection flaw in EmailTrack allows authenticated users to gain full control of the server. Patch your system today.
A critical Hawtio Operator vulnerability, tracked as CVE-2026-78234, allows in-cluster service impersonation. Discover the impact and mitigation steps.