 Do Son
QNAP QuMagie vulnerabilities let unauthenticated attackers access media files, causing information disclosure. Patch QuMagie and License Center now.
Vulnerability
QNAP patched 14 NAS vulnerabilities in QTS, QuTS hero, and QVP, including command injection and credential-theft flaws. Update your QNAP NAS now.
Attackers exploit ArcGIS Account Recovery flaws. Read this security bulletin to secure your enterprise by disabling default accounts and enabling SMTP.
Attackers are actively exploiting a critical Gravity SMTP vulnerability (CVE-2026-4020) causing sensitive information exposure. Update your plugin now.
A critical Apache Shiro LDAP Injection vulnerability in DefaultLdapRealm, CVE-2026-49268, allows authentication bypass. Update your framework immediately.

New patches fix critical Spring HATEOAS flaws including CVE-2026-41006 and CVE-2026-41007 to prevent heap exhaustion and bypasses.

A critical Jenkins security advisory 2026 warns of deserialization and XSS flaws like CVE-2026-53435. Patch your CI/CD pipelines immediately!

Patch your systems now. Progress Sitefinity critical vulnerabilities reached CVSS 10.0. Apply the latest Sitefinity security update immediately.
Learn about the new Notepad++ security flaws. Public Notepad++ exploit code triggers arbitrary code execution. Update to version v8.9.6.1 now.
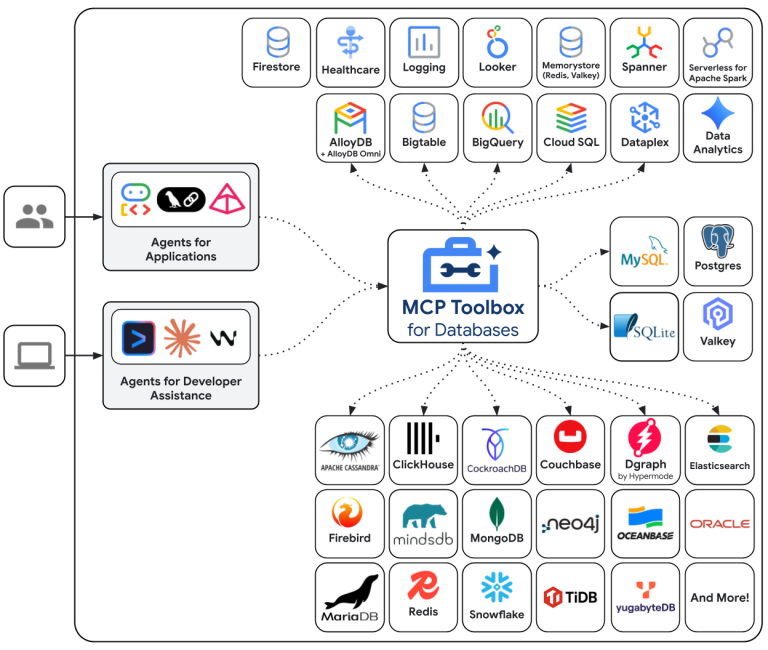
A critical MCP Toolbox vulnerability exposes enterprise databases. Learn how this security flaw allows session hijacking and how to fix it.

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

A critical Angular hostname hijacking vulnerability allows SSRF attacks. Discover the impact on platform-server and how to patch your apps.
Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!
PHP releases urgent security patches for a 9.5 severity RCE in the SOAP extension and a PHP-FPM XSS flaw. Update to 8.2.31, 8.3.31, 8.4.21, or 8.5.6 now!
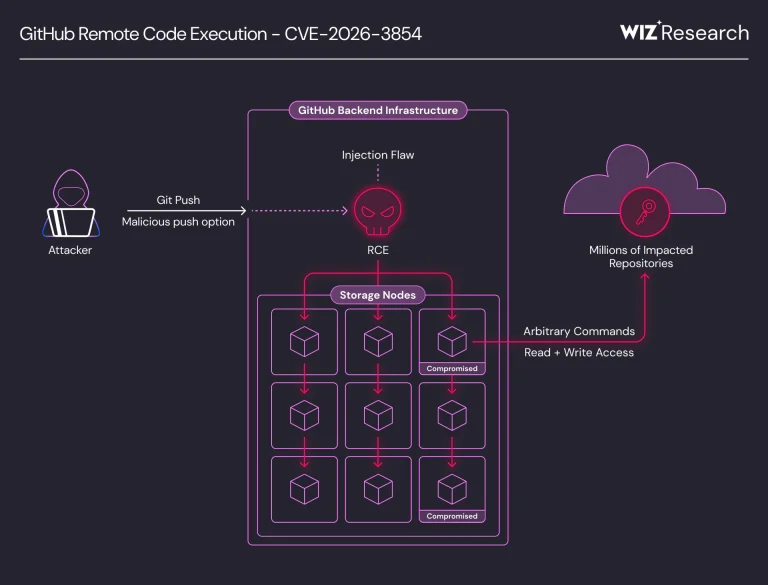
Wiz Research reveals CVE-2026-3854, a critical GitHub RCE. One git push could expose millions of repos. GHES users must patch to v3.19.3 immediately.
Paperclip’s 9.8 CVSS flaw and cross-tenant leaks expose AI agents to total takeover. Learn how a simple command could compromise your entire business.
Sonatype Nexus Repository (CVE-2026-5189) faces a critical 9.2 CVSS flaw. A hardcoded database credential grants full host access. Patch to v3.71.0 now!

Use-after-free flaw in Rsync versions 3.0.1–3.4.1 allows DoS and info leaks via malicious xattr traffic. Learn how a simple qsort fix secures your syncs.
Critical Remote Command Injection flaws in PHP Composer's Perforce integration (CVE-2026-40176 & CVE-2026-40261) could lead to full system compromise. Patch now.
A maximum10 CVSS score: Paperclip's RCE flaw allows unauthenticated server takeover in 6 API calls. Secure your AI workforce and update to v2026.410.0 now!

Critical 9.3 CVSS flaw (CVE-2026-34078) in Flatpak allows apps to escape sandboxes and access all host files. Secure your Linux system—update to v1.16.4 now!

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!