
 Do Son
Atlassian warns of a high-severity RCE vulnerability (CVE-2026-21570) in Bamboo Data Center. Patch now to secure your CI/CD pipelines from malicious code.
Vulnerability

A critical 9.6 CVSS vulnerability in jsPDF (CVE-2026-31938) allows attackers to inject malicious scripts via XSS. Update to version 4.2.1 immediately.
Two critical flaws in Langflow (CVE-2026-33017 & CVE-2026-33309) allow unauthenticated remote code execution and arbitrary file writes. Secure servers now.
Ubiquiti warns of a critical 10.0 CVSS Path Traversal flaw (CVE-2026-22557) in UniFi Network Applications allowing total system takeover. Patch immediately.

A critical 9.0 CVSS vulnerability (CVE-2026-3564) in ConnectWise ScreenConnect exposes server cryptographic keys. On-premise users must update to 26.1 now.

Craft CMS patches CVE-2026-32267, a critical 7.7 CVSS flaw where a simple Live Preview token grants low-privilege users full admin access. Update today.

Two critical flaws in Spring AI (CVE-2026-22729 & CVE-2026-22730) allow attackers to bypass access controls via JSONPath and SQL injection. Update now.

A critical 10.0 CVSS logic flaw in File Browser (CVE-2026-32760) grants unauthenticated users automatic admin rights upon signup. Update to 2.62.0 now.

CrackArmor exposes 12.6M Linux servers to root escalation. Qualys TRU discovers 9 AppArmor flaws letting users bypass security and escape containers.
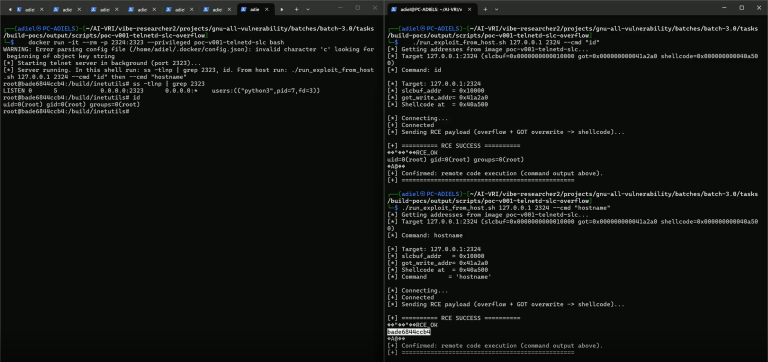
A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.

A pre-auth flaw in OpenSSH's GSSAPI Key Exchange (CVE-2026-3497) exposes Ubuntu and Debian servers to heap corruption and data leaks. Patch now.

A critical SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin exposes 400K+ sites to database theft. Update to version 4.1.0 immediately.

A critical 10.0 CVSS flaw (CVE-2026-3611) in Honeywell IQ4x BMS controllers leaves web HMIs exposed without authentication. Secure your systems immediately.
A critical 9.6 CVSS XSS vulnerability (CVE-2025-40943) in Siemens SIMATIC S7-1500 CPUs allows attackers to inject malicious code via trace files.

SAP's latest security update addresses 15 flaws, including critical RCE (CVE-2019-17571) and deserialization (CVE-2026-27685) vulnerabilities. Patch now.
Two critical flaws in Budibase (CVE-2026-31816, CVE-2026-30240) allow unauthenticated API access and secret exfiltration via path traversal. Patch immediately.

A critical 9.8 CVSS authentication bypass (CVE-2026-0953) in Tutor LMS Pro is being actively exploited in the wild. Update to version 3.9.6 immediately.

A critical 8.5 CVSS command injection flaw (CVE-2025-15568) in TP-Link Archer AXE75 routers allows complete root-level network takeover. Patch immediately.
A high 8.8 CVSS flaw (CVE-2026-3288) in ingress-nginx allows arbitrary code execution and massive Kubernetes secret leakage. Patch immediately.
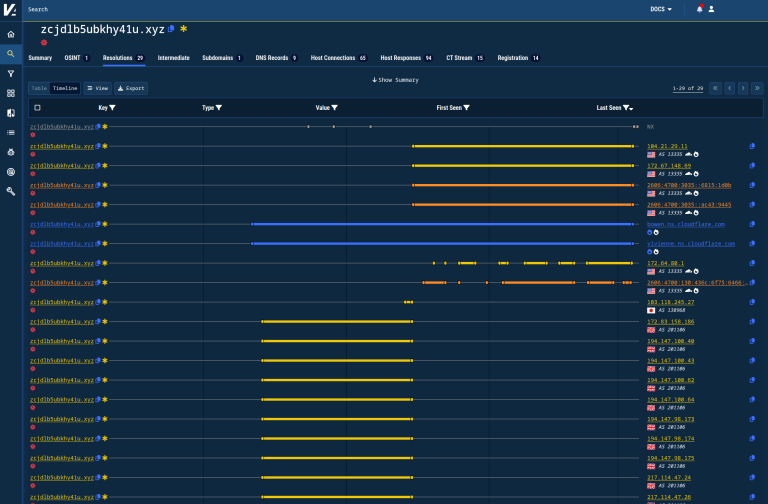
Validin reveals how the Coruna iOS exploit kit evolved from targeted surveillance to mass crypto-draining and geopolitical watering hole attacks.

SICK PSIRT warns of critical vulnerabilities (CVE-2026-2330, CVE-2026-2331) in Lector85x and Lector83x scanners allowing full device takeover. Update now.
A critical 9.3 CVSS flaw (CVE-2026-25921) in Gogs' LFS handling allows attackers to silently overwrite repository files, risking severe supply-chain attacks.