 Do Son
A critical 9.4 CVSS buffer overflow flaw (CVE-2026-1678) in Zephyr RTOS's DNS parser allows unauthenticated RCE on IoT devices. Patch immediately.
Vulnerability
A critical 9.3 CVSS reflected XSS flaw (CVE-2026-29183) in SiYuan's dynamic icon API lets attackers steal private notes via SVG injection. Update now.

A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.

A critical 9.8 CVSS flaw (CVE-2026-27944) in Nginx UI lets hackers download and decrypt full system backups via an open API. Update and rotate secrets!

A critical 9.8 CVSS flaw (CVE-2026-29058) in AVideo-Encoder allows unauthenticated remote attackers to execute arbitrary system commands. Patch now.

Researchers discovered three major flaws in Amazon’s AWS-LC cryptographic library, allowing hackers to bypass digital signature validation. Update now.
An integer overflow flaw (CVE-2025-66168) in Apache ActiveMQ's MQTT module allows authenticated attackers to crash brokers. Update your systems immediately.
A critical 10.0 CVSS zero-click flaw (CVE-2026-20079) in Cisco Secure FMC gives unauthenticated attackers root access. Patch your systems immediately.
A critical 10.0 CVSS flaw (CVE-2026-29000) in the pac4j-jwt library allows attackers to forge JWTs and bypass authentication. Patch immediately.
A critical 10.0 CVSS unauthenticated RCE flaw (CVE-2026-20131) in Cisco Secure FMC allows hackers root access via insecure Java deserialization. Patch now.
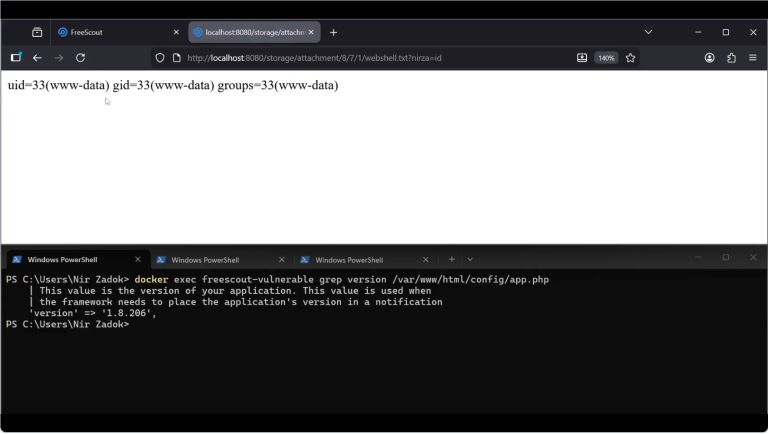
A critical 10.0 CVSS unauthenticated remote code execution flaw (CVE-2026-28289) in FreeScout allows full server takeover via an invisible character exploit.
A critical 9.4 CVSS flaw (CVE-2026-1775) in Labkotec LID-3300IP ice detectors allows hackers to hijack wind turbines and airports. Hardware upgrade needed.
Nokia discovers a critical 9.1 RCE flaw (CVE-2026-28370) in OpenStack Vitrage's RCA service. Patch immediately to prevent total host server takeovers.

A critical 9.8 CVSS flaw (CVE-2026-1492) in the WordPress User Registration & Membership plugin lets unauthenticated attackers create admin accounts.
Langflow 1.8.0 patches a critical 9.8 CVSS RCE vulnerability (CVE-2026-27966) where a hardcoded "allow_dangerous_code" setting enables prompt injection attacks.

Angular patches a critical 9.2 CVSS SSRF vulnerability (CVE-2026-27739). Attackers can manipulate Host headers to steal credentials and probe internal networks.

Critical SQL injection flaw (CVE-2026-26198) in ormar Python ORM allows unauthenticated attackers to leak entire databases. Update to version 0.23.0 immediately!

Critical path traversal flaws (CVE-2026-26065, CVE-2026-26064) in the Calibre e-book manager allow RCE via malicious PDB and ODT files. Update to 9.3.0.

ASUS removes "File Shredder" from Business Manager due to CVE-2025-13348 (CVSS 8.5). The feature is gone in V3.0.37.0. Check your commercial PCs.

Microsoft patches "Reprompt," a critical Copilot flaw. Attackers could steal sensitive data with just one click on a legitimate link.

Apache Kyuubi patches a high-severity 8.8 CVSS flaw (CVE-2025-66518) that allows unauthorized local file access via path traversal. Update to v1.10.3!

D4mianWayne details CVE-2025-68615, a 9.8 critical flaw in Net-SNMP allowing unauthenticated RCE. Update to v5.9.5 or v5.10.pre2 now!