
 Do Son
Two WordPress Core vulnerabilities (XSS and Info Exposure) affecting versions up to 6.8.2 were accidentally exposed before patches were ready.
Vulnerability

A critical flaw (CVE-2025-41715) in WAGO Device Sphere allows an unauthenticated remote attacker to gain unauthorized access and potentially compromise its database.

CISA has added a high-severity V8 zero-day (CVE-2025-10585) to its exploited vulnerabilities catalog. An urgent Chrome update is available to patch the flaw.
A high-severity flaw in the Salesforce CLI installer (CVE-2025-9844) allows for arbitrary code execution and privilege escalation on affected systems.

A critical, unpatched OnePlus flaw (CVE-2025-10184) allows any app to read SMS data without permission, breaking MFA protections. PoC is available.

A critical XSS flaw (CVE-2025-59545) in DNN's Prompt module allows attackers to execute code and hijack admin sessions. All users must update immediately.

Google has released an urgent update for Chrome, patching three high-severity flaws in its V8 JavaScript engine, two of which were discovered by AI.

SolarWinds has released an urgent hotfix for its Web Help Desk software, patching an unauthenticated RCE vulnerability (CVE-2025-26399) that bypasses earlier fixes.

A critical XSS flaw in the Lectora e-learning platform (CVE-2025-9125) allows for malicious code injection, posing a risk of session hijacking and redirection.

Libraesva has issued an urgent advisory for a command injection flaw in its ESG. The bug, which has been exploited, allows remote command execution via a malicious email.

A new technique, "EDR-Freeze," uses a built-in Windows feature to suspend antivirus and EDR processes, giving attackers a critical window to operate undetected.

A critical flaw (CVE-2025-41243) in Spring Cloud Gateway with a CVSS 10.0 score allows unauthenticated RCE via SpEL injection. A PoC has been released.
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
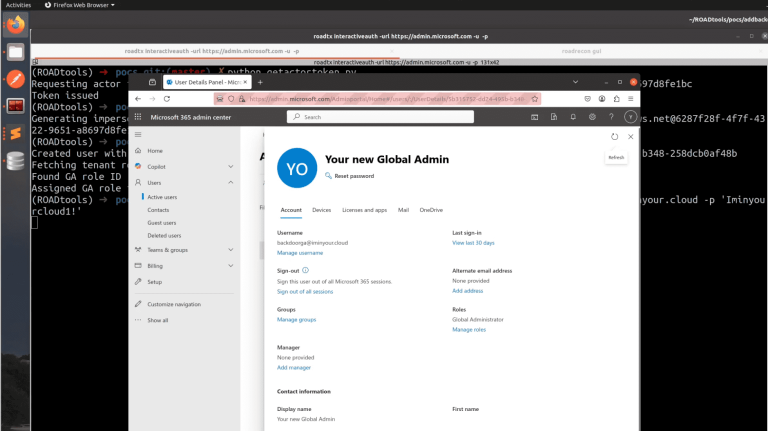
A critical flaw (CVE-2025-55241) in Microsoft Entra ID could have allowed a compromise of every tenant worldwide by bypassing security with "Actor tokens."

A new report reveals a CWMP service flaw in TP-Link routers that can be exploited for RCE. Researchers have published a detailed write-up and a PoC on GitHub.

Nokia has issued a security advisory for two high-severity flaws (RCE and authentication bypass) in its CBIS and NCS platforms. Immediate patching is urged.

A critical vulnerability in HubSpot’s Jinjava template engine (CVE-2025-59340) could lead to remote code execution. Patch immediately to secure your site.

CISA has released a new report detailing how attackers are exploiting Ivanti EPMM flaws to deploy malicious listeners and gain remote code execution.

A new 10.0 CVSS score vulnerability in Fortra's GoAnywhere MFT platform allows attackers to execute remote code. Learn how to protect your systems now.

CISA issued a security advisory for Delta Electronics DIALink vulnerabilities, including a critical 10.0 CVSS flaw that could allow authentication bypass.

Jenkins has patched multiple flaws, including a high-severity DoS vulnerability in its bundled Jetty server that could allow unauthenticated attackers to crash the service.

Google has released an urgent Chrome update, patching a V8 zero-day (CVE-2025-10585) being exploited in the wild, along with other high-severity flaws.

Two critical vulnerabilities in Planet Technology’s Industrial Cellular Gateways could allow unauthenticated attackers to take over devices, exposing critical infrastructure.