 Do Son
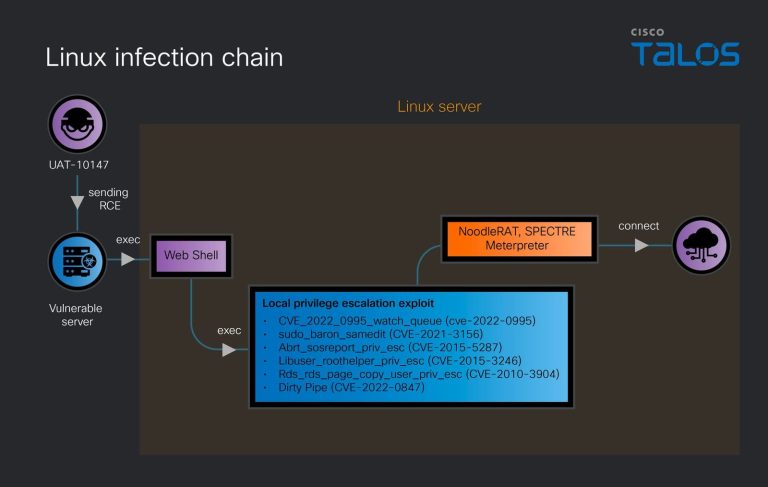
Cisco Talos revealed how UAT-10147 agentic AI attacks target global servers. Learn how UAT-10147 agentic AI tools automate intrusions and data theft.
Web Server Security
Seven Apache Tomcat vulnerabilities are patched, including an authentication bypass (CVE-2026-55957). Update to a fixed Tomcat release now.
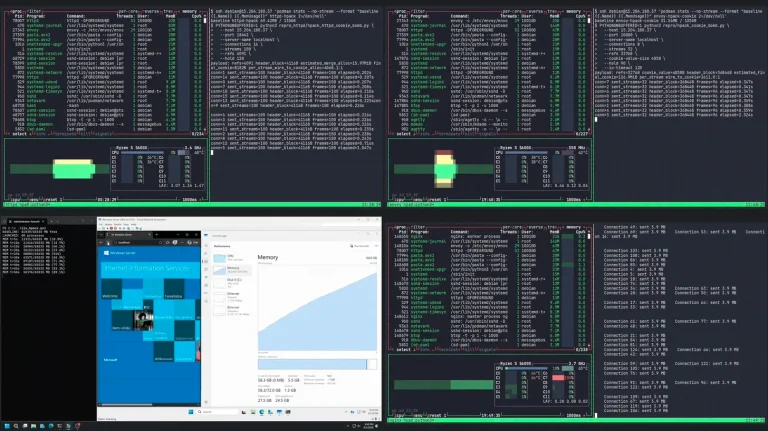
Researchers disclosed a public PoC for an HTTP/2 'bomb' that exhausts server resources and causes denial of service. Mitigation steps inside.

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.

PolyShell Exposed: Public PoC and active exploitation disclosed for critical Magento RCE. With no official patch, your storefront is at risk. Secure it now!
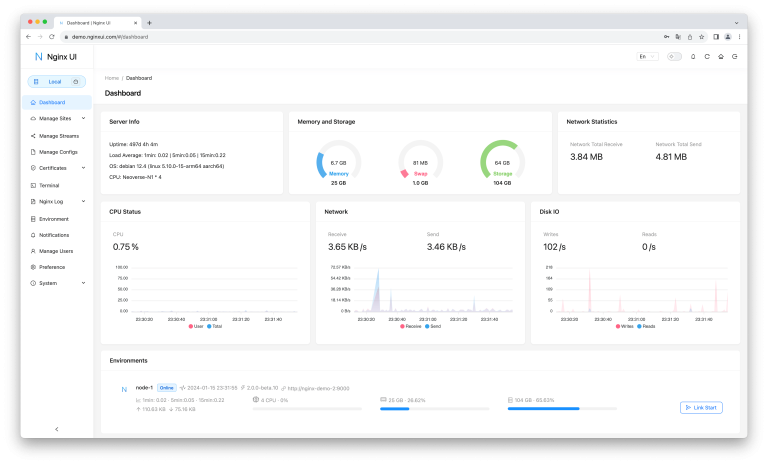
Public PoC code and full details are out for a 9.8 CVSS flaw in Nginx UI (CVE-2026-33032). With no official patch, servers are at risk. Secure yours now!

F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!
Apache Tomcat rolls out urgent updates for versions 9, 10, and 11 to fix legacy HTTP/0.9 protocol confusion and SNI certificate bypass flaws. Patch now.
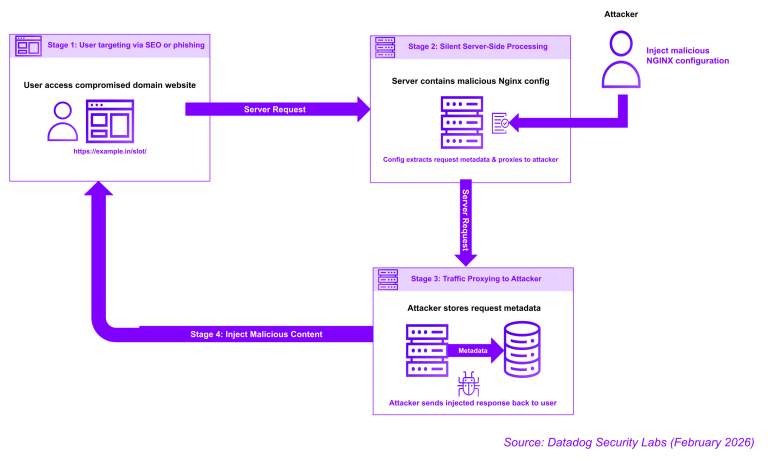
Hackers are hijacking NGINX servers via malicious config injections. Datadog warns of silent traffic redirection for SEO poisoning. Check your proxy_pass.
F5 warns of NGINX flaw CVE-2026-1642 (CVSS 8.2). MITM attackers can inject data into upstream TLS responses. Update to v1.29.5 immediately.

New "directory shadowing" malware creates physical folders to hijack WordPress URLs. It feeds gambling spam to Googlebots while staying invisible.