 Do Son
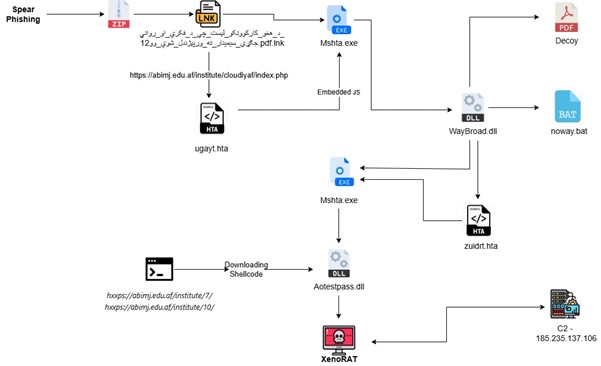
A deep look at the SideCopy XenoRAT malware attack targeting the Afghan Ministry of Finance. Learn how Operation XENOFISCAL bypasses defenses.
XenoRAT
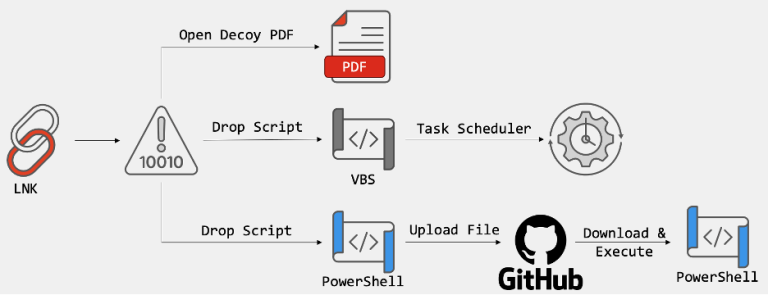
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.

North Korean APT Kimsuky is using GitHub private repos, Dropbox, and XenoRAT malware via spearphishing to compromise victims and conduct cyber-espionage.

Learn about the implications of the new XenoRAT variant, utilizing Excel XLL files for delivery and posing a threat to enterprise networks.
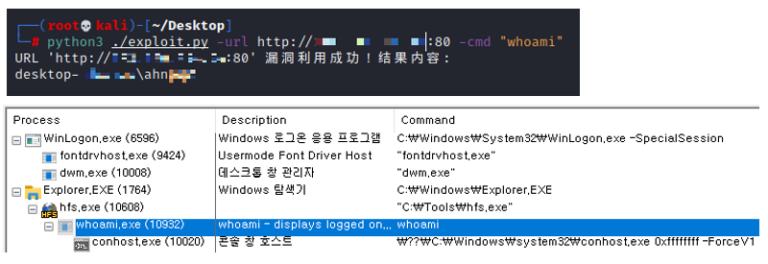
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware