 Do Son
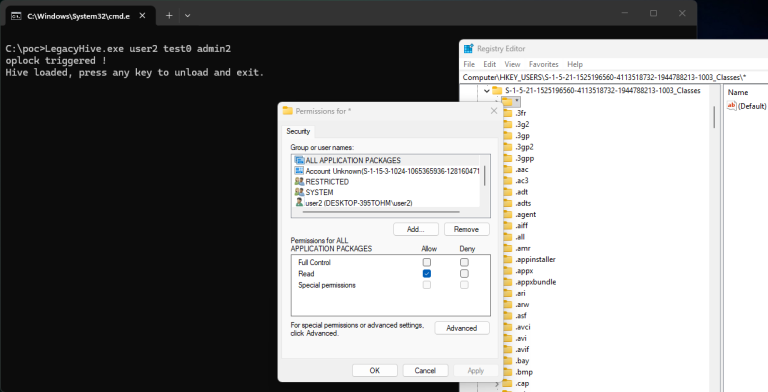
LegacyHive exploit code is public. This unpatched Windows privilege escalation flaw from Nightmare-Eclipse defeats the July 2026 patch.
zero-day

Microsoft's July 2026 Patch Tuesday fixes 570 flaws. Zero-days CVE-2026-56155 and CVE-2026-56164 are exploited in the wild. Patch now.
A threat actor exploited a Cisco SD-WAN zero-day (CVE-2026-20245) to gain root access. Learn how this attack happened and how to secure your networks.
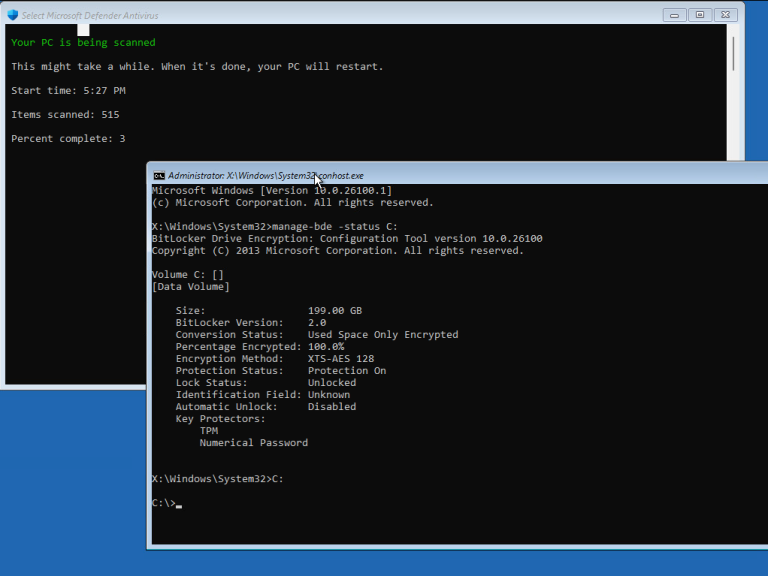
A new GreatXML BitLocker bypass PoC exploit is publicly disclosed. Learn how this Windows Defender vulnerability grants unrestricted volume access.

A critical Check Point VPN vulnerability is actively exploited in the wild, allowing unauthenticated attackers to bypass user login requirements.

Read our weekly threat intelligence briefing. This active vulnerability management report covers June 2026 CISA KEV additions and new zero-day exploits.
A critical Cisco SD-WAN vulnerability is actively exploited in the wild. Learn how to inspect logs and secure your deployment immediately.

Google patches a critical Android zero day flaw in the June 2026 security bulletin. Learn how to secure your device from active exploitation now.
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
CVE-2026-42897 exploited in the wild. A 8.1 CVSS OWA flaw allows RCE via malicious emails. Verify your Exchange Emergency Mitigation (EM) status now!

Cisco Catalyst SD-WAN CVE-2026-20182 (CVSS 10) exploited in the wild. Attackers bypassing auth to seize admin control. Upgrade your network fabric now!

CVE-2026-32661 exploited in the wild. A 9.8 CVSS flaw in GUARDIANWALL MailSuite allows unauthenticated RCE. Apply Canon's official patches immediately.
Urgent: Public PoC exploit code released for YellowKey (BitLocker bypass) and GreenPlasma (SYSTEM elevation). Windows 11 and Server 2025 are at high risk.

The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!
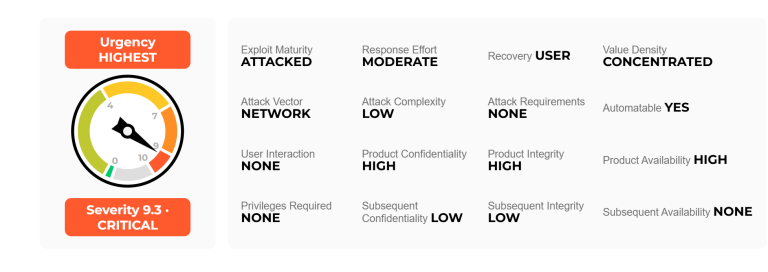
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!
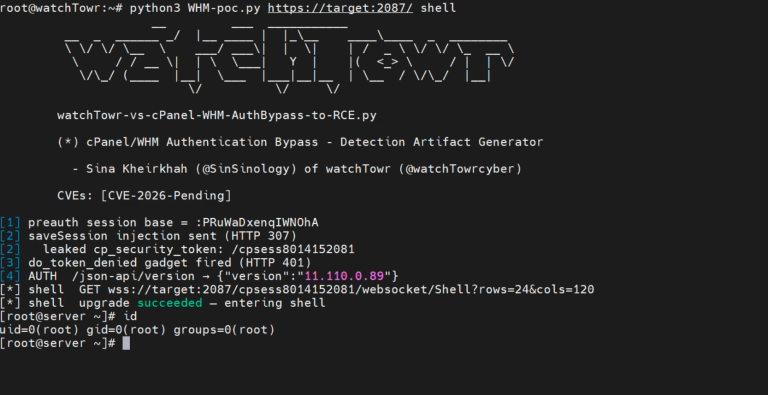
cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.

Unpatched CVE-2026-5757 in Ollama allows unauthenticated heap memory exfiltration via crafted GGUF files. No patch available—secure your LLM servers now.
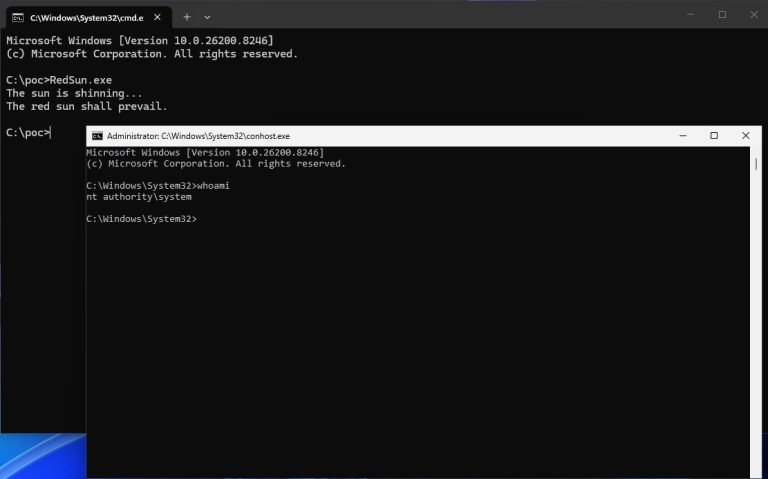
Windows Defender "RedSun" zero-day revealed! This unpatched EoP flaw turns antivirus into a delivery tool for malicious payloads. PoC is public—patch now!
AVideo’s YPTSocket plugin faces a critical CVSS 10 vulnerability. Unauthenticated attackers can hijack every active session at once. No patch is available.
Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates

Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates
Microsoft’s April 2026 Patch Tuesday fixes 163 flaws, including an exploited SharePoint spoofing bug (CVE-2026-32201). Patch by April 28 per CISA mandate.
CISA adds 7 active exploits to the KEV catalog, from legacy Office bugs to 2026 Fortinet zero-days. Patch these high-risk flaws now to secure your network.