 Do Son
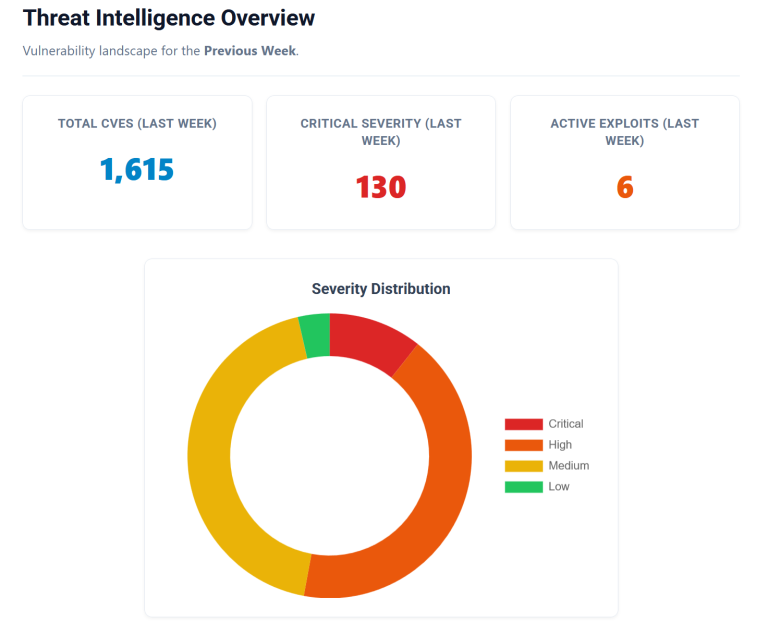
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.
zero-day

Weaver E-cology 10.0 faces a critical 9.3 CVSS RCE (CVE-2026-22679). Unauthenticated attackers can hijack servers via a debug endpoint. Patch immediately!

A critical Adobe Reader zero-day allows attackers to steal local files and achieve system control via malicious PDFs. Learn how the unpatched exploit works.

Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!

Apple releases iOS 18.7.7 to combat the "DarkSword" exploit kit. Protect your legacy iPhone or iPad from this state-level threat by updating today.

Google warns that CVE-2026-5281 is currently being exploited in the wild. Update Chrome to version 146.0.7680.177 immediately to fix this high-severity flaw.
Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.

Public PoC code and full details are out for a 9.8 CVSS flaw in Nginx UI (CVE-2026-33032). With no official patch, servers are at risk. Secure yours now!

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!
AVideo faces a security crisis with 5 unpatched critical flaws (CVSS 10.0). Attackers can hijack streams and execute code. Learn how to protect your server.

This week in cybersecurity: 1,348 new vulnerabilities discovered, including seven critical 10.0 CVSS flaws and the highly active DarkSword exploit chain.

CrackArmor exposes 12.6M Linux servers to root escalation. Qualys TRU discovers 9 AppArmor flaws letting users bypass security and escape containers.

Google releases an emergency Chrome update to patch two actively exploited zero-day vulnerabilities (CVE-2026-3909 & CVE-2026-3910). Update immediately.

Microsoft's March 2026 Patch Tuesday addresses 93 vulnerabilities, including two public zero-days affecting SQL Server and .NET. Patch your systems now.

A critical 10.0 CVSS flaw (CVE-2026-20127) in Cisco Catalyst SD-WAN is actively exploited in the wild. A public PoC is now available. Patch immediately!

Google Threat Intelligence uncovers "Coruna", a repurposed iOS exploit kit now used by state-sponsored and financially motivated hackers to steal crypto.

CISA adds actively exploited Qualcomm (CVE-2026-21385) and VMware (CVE-2026-22719) flaws to its KEV catalog. See the impact and patch deadlines inside.

HPE warns of a critical CVSS 10.0 vulnerability (CVE-2026-23600) in AutoPass License Server. Remote attackers can bypass authentication. Patch to 9.19 now!

Google’s March 2026 Android update fixes 129 flaws, including CVE-2026-21385—a high-severity Qualcomm vulnerability currently being exploited in the wild.
An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.
Cisco Talos warns of CVE-2026-20127, a CVSS 10 flaw in Catalyst SD-WAN exploited since 2023. UAT-8616 bypassed authentication to hijack global network fabrics.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.