U.S. Offers $10 Million Reward for Information on GRU Hackers Targeting Critical Infrastructure
 Do Son
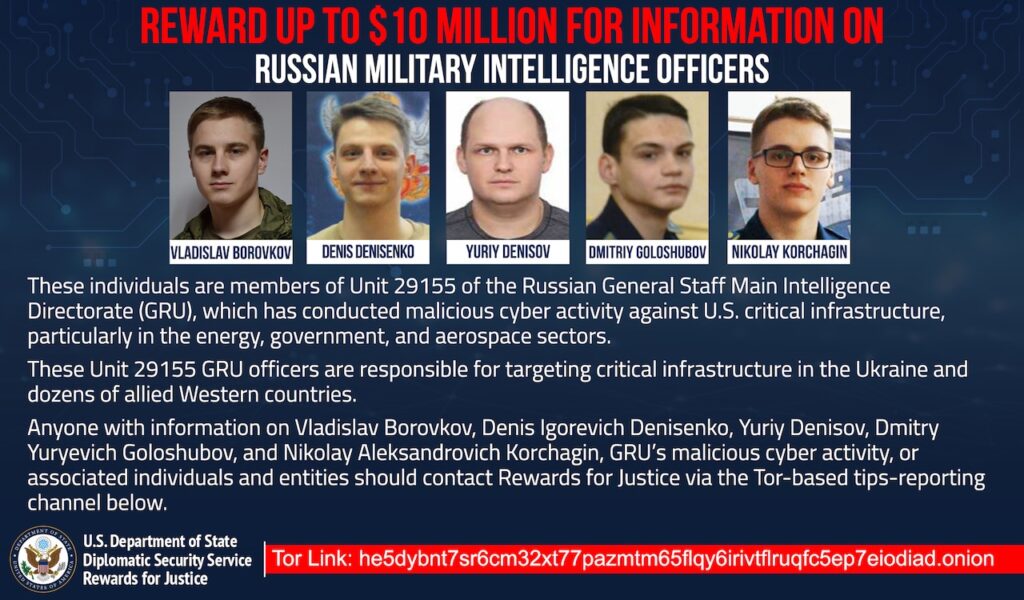
The U.S. State Department’s Rewards for Justice program has announced a reward of up to $10 million for information leading to the identification or location of five Russian military intelligence officers accused of conducting malicious cyber activities against U.S. critical infrastructure.
The spotlight is on five Russian military intelligence officers tied to Unit 29155 of the Russian General Staff Main Intelligence Directorate (GRU). The operatives include:
- Vladislav Borovkov (Боровков Владислав)
- Denis Igorevich Denisenko (Денисенко Денис Игоревич)
- Yuriy Denisov (Денисов Юрий)
- Dmitriy Yuryevich Goloshubov (Голошубов Дмитрий Юрьевич)
- Nikolay Aleksandrovich Korchagin (Корчагин Николай Александрович)
These individuals are believed to be key players behind some of the most destructive cyberattacks in recent history. According to U.S. authorities, they were responsible for deploying the WhisperGate malware in cyberattacks that compromised Ukrainian government systems ahead of Russia’s 2022 invasion of Ukraine. These attacks targeted critical Ukrainian infrastructure, disrupting government functions and private sector operations.
The GRU’s malicious cyber activities extend far beyond Ukraine. Intelligence reveals that these operatives also set their sights on U.S. critical infrastructure, scanning for vulnerabilities, mapping networks, and identifying weaknesses across sectors such as energy, government, and aerospace. Their goal? To compromise systems, steal data, and cause disruptions that would serve Russia’s strategic interests.
The WhisperGate malware, a destructive tool used by these operatives, exemplifies their methods—stealthy infiltration followed by targeted attacks to disable systems or exfiltrate sensitive information. It is suspected that this malware has been deployed not only in Ukraine but also across Western allied nations, where critical infrastructure systems have been under siege.
In addition to the U.S. and Ukraine, these GRU operatives have been linked to cyber campaigns targeting critical infrastructure in dozens of Western allied countries. Their tactics typically involve unauthorized access to victims’ computers, followed by the deployment of destructive malware or other cyber tools to cripple systems and sow chaos.
The GRU’s Unit 29155 is notorious for its role in cyber warfare, and this latest revelation underscores how cyber operations have become a key element of modern geopolitical conflicts. These operations often aim to create instability, undermine trust in governmental institutions, or extract strategic benefits for Russia, particularly in times of heightened international tensions.
The Rewards for Justice program is now offering significant financial incentives for information that could help locate or identify these GRU officers. The $10 million reward underscores the gravity of these cyberattacks, particularly their impact on U.S. national security.
Related Posts:
- CIA: Russian intelligence agency GRU was behind the NotPetya attack
- US Denounces Russian Cyberattacks Targeting Germany, EU Nations
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
