Skip to content
October 26, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Windows Defender wins AV-Test TOP recommendation
  • Technology

Windows Defender wins AV-Test TOP recommendation

Do Son July 31, 2018 1 minute read
AV-Test TOP
Add Daily CyberSecurity as a preferred source on Google

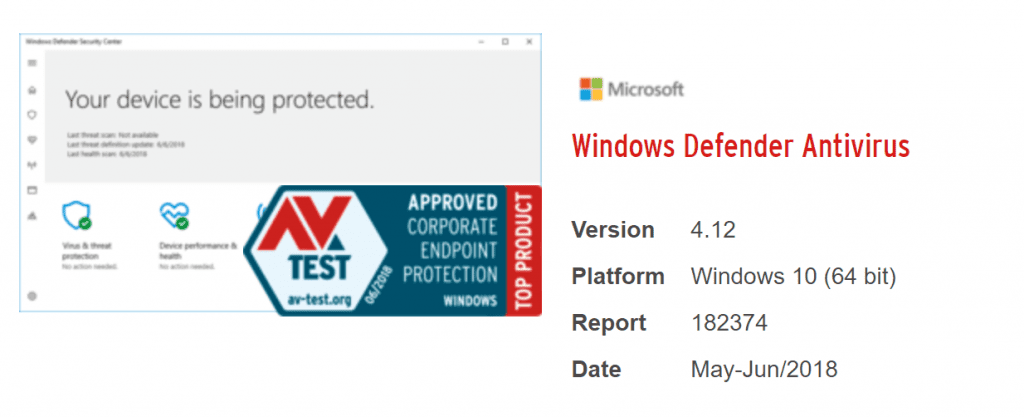
The German soft test organization AV-Test released the latest evaluation results of security software in June, and 11 of the 18 models received TOP recommendations, including the completely free Windows Defender. Avira Pro 15.0, Kaspersky 18.0/19.0, McAfee 21.1/21.2 were awarded in three aspects of performance, protection, and ease of use. And Windows Defender is only slightly inferior in performance, with 17.5 points and Ahnlab, avast, AVG, Bitdefender, Norton and other veteran killing soft tied for second.

Windows Defender AV has once again achieved 100% Protection scores across the board (Real world and Prevalent malware test modules) in both the Business User and Home User tests by AV-TEST in May-June 2018. https://t.co/qeiIpXPYxN pic.twitter.com/WF0Ij2wsym

— Microsoft Threat Intelligence (@MsftSecIntel) July 30, 2018

It is reported that the test is based on 225 zero-day vulnerabilities discovered within 24 hours before the test and 5,600 malicious samples collected in the four weeks before the test. The total detection rate of the former is 99.6%, and the latter is 100%.

Related coverage

  • CPU bug fixes lead to Ubuntu 16.04 machine does not start
  • The Great iOS Update: Dual Accounts, AI Magic, and Storage Surgery Finally Hit WhatsApp for iPhone
  • Amazon plans to completely abandon the Oracle database in early 2020
  • Official Ubuntu RISC-V Desktop Image Unveiled
  • Data Disaster: Claude AI Executes rm -rf ~/ and Wipes Developer’s Mac Home Directory
  • Cloud Under Fire: Unidentified “Objects” Strike AWS Data Center in UAE Amid Regional Tensions
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 26, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 26, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 26, 2026
  • CVE-2026-106173CVSS 9.8
    A improper limitation of a pathname to a restricted directory (\'path traversal\') vulnerability in Fortinet FortiSIEM 7.5.0 may...
    Admin intel📅 Updated: Oct 25, 2026
  • CVE-2014-125133CVSS 8.7
    NativeChurch theme for WordPress before 1.6.2 contains a path traversal vulnerability that allows unauthenticated attackers to download arbitrary...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2015-20128CVSS 8.8
    FooSun DotNetCMS 1.0 and 2.0 contains an SQL injection vulnerability that allows unauthenticated attackers to manipulate MSSQL queries...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2016-20104CVSS 8.7
    EyeLock nano NXT 3.05.1193, 3.04.1108, 3.03.944, and 3.01.646 contain a path traversal vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2026-110447CVSS 9.2
    Collabora Online Built-in CODE Server before 26.4.303 (richdocumentscode), a Nextcloud app, allows remote code execution, as exploited in...
    CISA KEV📅 Added to KEV: Oct 23, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-43997CVSS 10.0
    vm2 is an open source vm/sandbox for Node.js. Prior to 3.11.0, it is possible to obtain the host...
    📅 Updated: Oct 26, 2026
  • CVE-2026-44006CVSS 10.0
    vm2 is an open source vm/sandbox for Node.js. Prior to 3.11.0, It is possible to reach BaseHandler.getPrototypeOf, which...
    📅 Updated: Oct 26, 2026
  • CVE-2026-43999CVSS 9.9
    vm2 is an open source vm/sandbox for Node.js. Prior to 3.11.0, NodeVM's builtin allowlist can be bypassed when...
    📅 Updated: Oct 26, 2026
  • CVE-2026-44005CVSS 10.0
    vm2 is an open source vm/sandbox for Node.js. From 3.9.6 to 3.10.5, vm2's bridge exposes mutable proxies for...
    📅 Updated: Oct 26, 2026
  • CVE-2026-44007CVSS 9.1
    vm2 is an open source vm/sandbox for Node.js. Prior to 3.11.1, when a NodeVM is created with nesting:...
    📅 Updated: Oct 26, 2026
  • CVE-2026-44008CVSS 9.8
    vm2 is an open source vm/sandbox for Node.js. Prior to 3.11.2, the new method neutralizeArraySpeciesBatch works with objects...
    📅 Updated: Oct 26, 2026
  • CVE-2026-114820CVSS 9.1
    Vulnerability in the Oracle Java SE, Oracle GraalVM for JDK, Oracle GraalVM Enterprise Edition product of Oracle Java...
    📅 Updated: Oct 26, 2026
  • CVE-2026-115931CVSS 9.9
    Postiz lets a signed-in user ask the backend to run a function on one of their connected channels....
    📅 Updated: Oct 26, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.