Skip to content
September 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Zstandard, fast real-time compression algorithm increases Ubuntu installation speed ​​by 10%
  • Technology

Zstandard, fast real-time compression algorithm increases Ubuntu installation speed ​​by 10%

Do Son March 15, 2018 2 minutes read
Zstandard
Add Daily CyberSecurity as a preferred source on Google

Debian and Ubuntu developer Julian Andres Klode said: “Canonical plans to implement Facebook’s open source compression algorithm, zstd by default in future versions of the Ubuntu Linux operating system.”

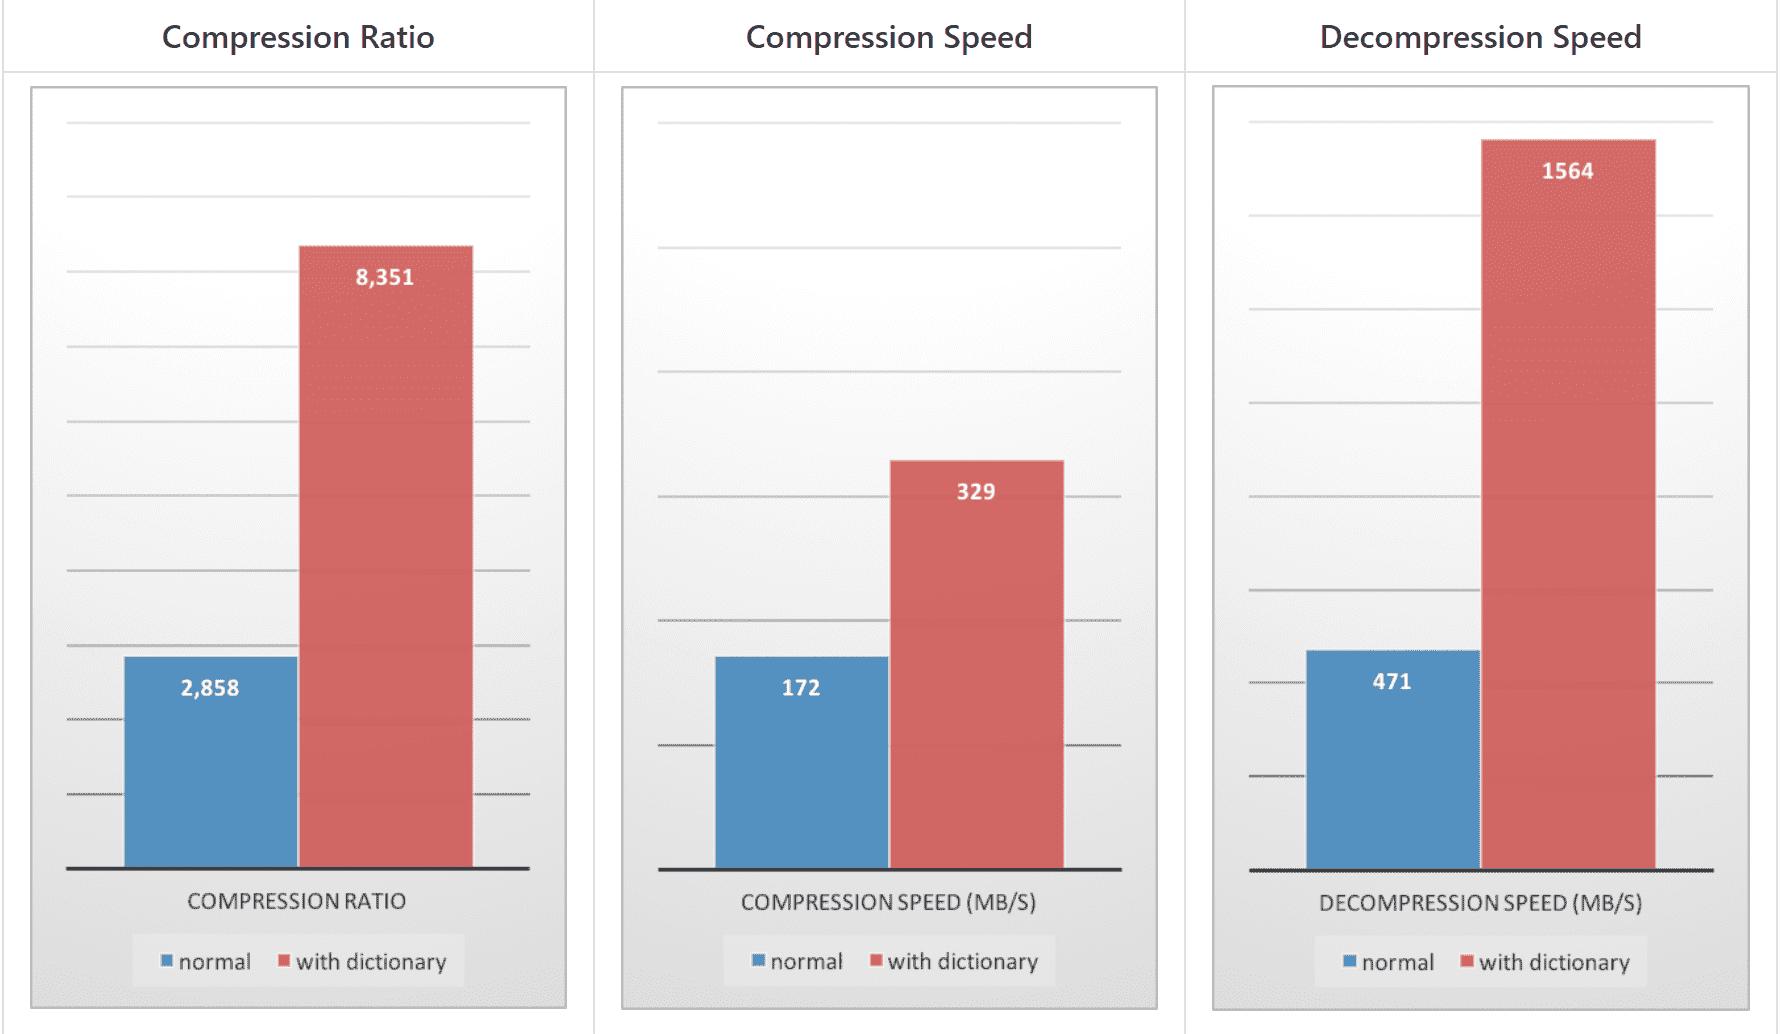
The algorithm was developed by Yann Collet at Facebook, an open source, lossless data compression algorithm designed to provide fast real-time compression and decompression speeds even faster than xz or gzip. Zstd supports up to 19 compression levels, offers 2.877 compression ratios, compression ratios up to 430 MB/s and decompression speeds up to 1110 MB/s.

Julian Andres Klode and Balint Reczey report that they have managed to increase the speed of standard 64-bit installations of Ubuntu 18.04 LTS (Bionic Beaver) by 10% and the zstd configuration settings to a maximum of 19 levels. Even better, when you disable the “eatmydata” library for fsync and related packages, the installation speed is increased by approximately 40%.

Debian GNU / Linux and Ubuntu operating system’s dpkg and apt command line package management system support Facebook’s zstd compression algorithm. In addition, Canonical plans to enable it by default in future Ubuntu releases, starting with the release of Ubuntu 18.10 this fall, but the report also stated that zstd has increased the size of Ubuntu installations by approximately 6%.

Zstd support is also implemented in the upcoming Ubuntu 18.04 LTS (Bionic Beaver) operating system, Ubuntu 18.04 LTS (Bionic Beaver) is expected to be released on April 26, 2018. Two developers stated that their zstd implementation for dpkg and apt can support multiple frames, meaning that Debian packages will eventually be compressed and decompressed in parallel.

Source: Softpedia

Related coverage

  • Qualcomm CEO: Intel’s Foundry Is Not Ready for Our Chips
  • The Great iOS Update: Dual Accounts, AI Magic, and Storage Surgery Finally Hit WhatsApp for iPhone
  • Microsoft will focus on building AI and cloud platforms in the future instead of Windows
  • Amazon’s Medical Move: New “Health AI” Assistant Turns Data into Doctor Visits
  • Celebrating 24 years of FreeDOS: Founder shares common FreeDOS commands
  • Intel’s 14A Process Will Be Its Most Expensive and Advanced Yet
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Ubuntu Zstandard

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intel📅 Updated: Sep 27, 2026
  • CVE-2026-88771
    Remote code execution due to improper input validation that can allow an unauthenticated attacker to execute arbitrary commands.
    Admin intel📅 Updated: Sep 27, 2026
  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-88771CVSS 9.5
    Improper input validation vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway. This issue affects ADC: before 14.1-73.37,...
    📅 Updated: Sep 27, 2026
  • CVE-2026-88772CVSS 9.5
    Vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway. This issue affects ADC: before 14.1-73.37, before 13.1-64.23, before...
    📅 Updated: Sep 27, 2026
  • CVE-2026-88773CVSS 9.3
    Inconsistent interpretation of HTTP requests ('HTTP Request/Response smuggling') vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway. This...
    📅 Updated: Sep 27, 2026
  • CVE-2026-100741CVSS 9.8
    Eval injection in the JScript event-script dispatcher in Progressive Robot Ltd's hMailServer, versions 6.0.0 through 6.3.3 on Windows,...
    📅 Updated: Sep 27, 2026
  • CVE-2026-96625CVSS 9.1
    fedify-dev/fedify repository advisory GHSA-q9f8-5hc7-898f
    📅 Updated: Sep 27, 2026
  • CVE-2026-94130CVSS 9.3
    Joomla Extension - joomlaboat.com - Unauthenticated SQL injection in YouTube Gallery extension < 5.7.3 - An SQL injection...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97161CVSS 9.2
    Joomla Extension - lomart.fr - Various path traversal / file access vectors in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-97163CVSS 10.0
    Joomla Extension - lomart.fr - Unauthenticated remote code installation in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.