
 Do Son
Apple is testing a "Deep Red" finish for the iPhone 18 Pro to follow Cosmic Orange's success. Meanwhile, the iPhone Fold sticks to classic Black and White.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
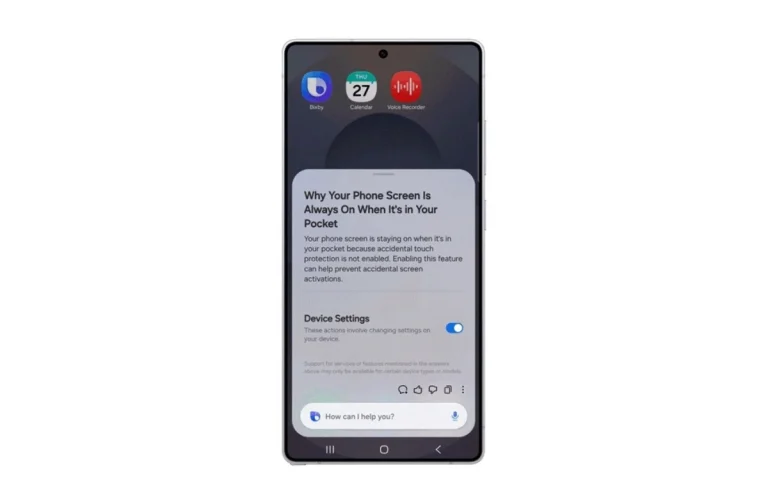
Bixby is back! The One UI 8.5 beta transforms Bixby into a Conversational Agent that understands natural language and controls your phone without menu-diving.

Jony Ive and OpenAI are building a camera-equipped smart speaker for 2027. Discover the $6.5B design deal bringing "Face ID" and visual AI into your home.

YouTube’s Gemini "Ask" feature hits smart TVs and consoles! Ask voice questions about recipes or lyrics without pausing. The passive TV era is officially over.
NVIDIA is playing the long game in India. By partnering with the $75M Activate fund, they are locking in the next generation of AI giants before they even exist.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.

Critical path traversal flaws (CVE-2026-26065, CVE-2026-26064) in the Calibre e-book manager allow RCE via malicious PDB and ODT files. Update to 9.3.0.
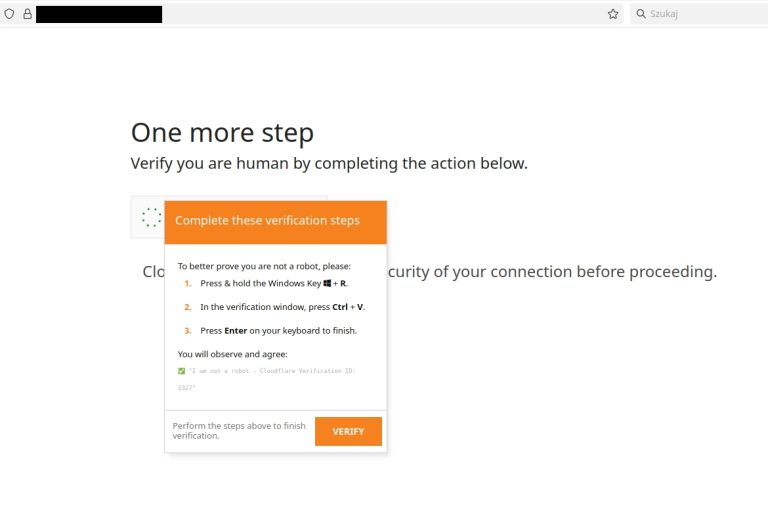
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
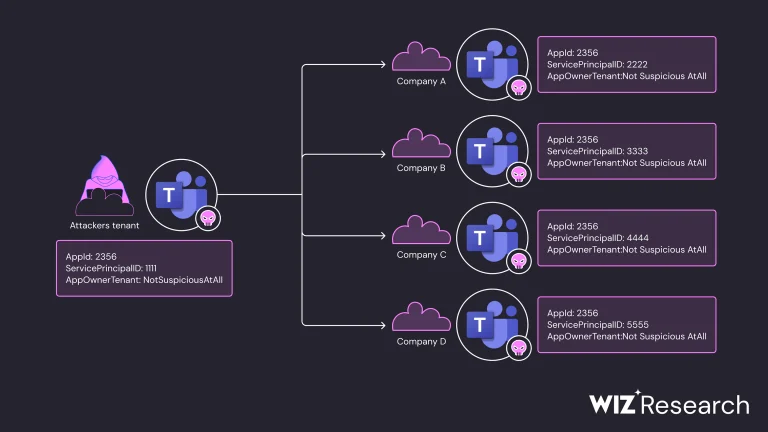
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
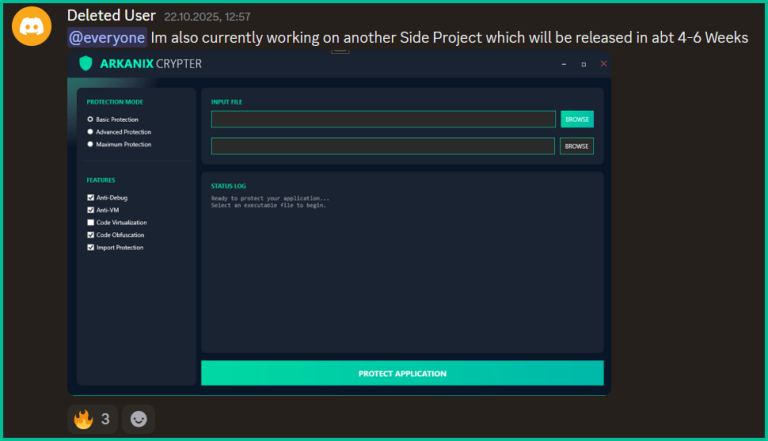
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.

A critical PDF Object Injection flaw (CVE-2026-25755) in jsPDF allows attackers to bypass AcroJS sandboxes. Update to version 4.2.0 immediately.
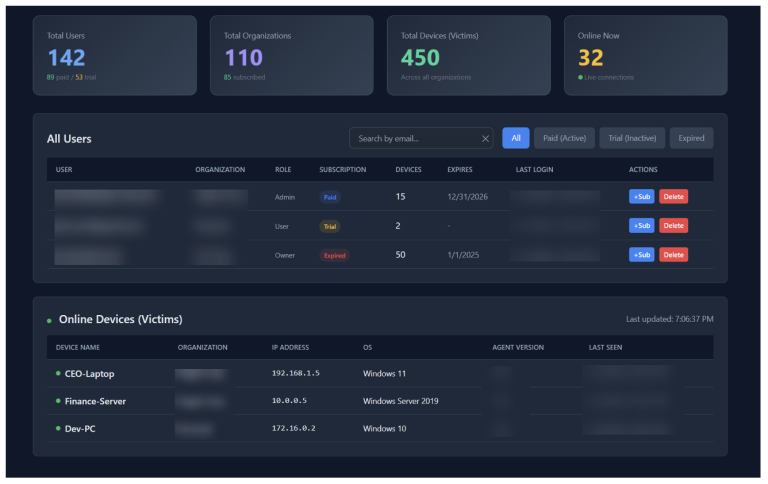
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

Group-IB exposes an industrialized mobile banking fraud campaign in Indonesia. GoldFactory hackers use fake Coretax apps and Gigabud.RAT to drain accounts.
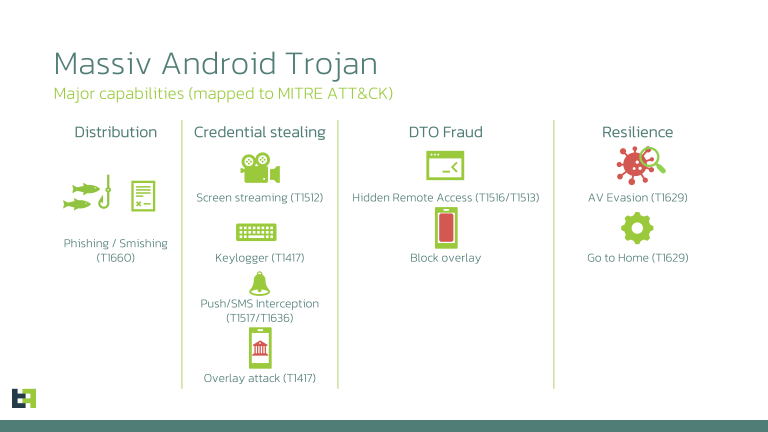
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

Technical analysis of energy monitoring and load prioritization strategies for maintaining smart home stability during grid outages.

Ukrainian hacker Oleksandr Didenko receives a 60-month sentence for orchestrating a massive laptop farm scheme aiding North Korean IT operatives.

Google patches Chrome zero-day CVE-2026-2441, an actively exploited memory flaw. With PoC exploit code now publicly disclosed, update to v145 immediately.

Apache Tomcat rolls out urgent updates for versions 9, 10, and 11 to fix legacy HTTP/0.9 protocol confusion and SNI certificate bypass flaws. Patch now.

Critical flaws in Live Server, Code Runner, and more expose 128M+ developers to file theft and remote code execution. Is your VS Code workspace secure?