
 Do Son
Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Zyxel issues urgent patches for a critical 9.8 severity flaw (CVE-2025-13942) in UPnP functions that allows remote attackers to execute OS commands. Patch now!

SolarWinds patches four critical 9.1 CVSS RCE vulnerabilities in Serv-U. Attackers can create admin users and execute code as root. Update to 15.5.4 now!

Broadcom warns of a high-severity RCE flaw (CVE-2026-22719) in VMware Aria Operations. Attackers can execute commands during system migrations. Patch now!
The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft

The Distillation War: Anthropic Accuses DeepSeek and Chinese Rivals of ‘Industrial-Scale’ Data Theft
Anthropic claims DeepSeek and other Chinese AI firms used 24,000 accounts to "pilfer" Claude's data. Inside the high-stakes battle for LLM training secrets.

Researcher @goyaramen exposes "ARXON," an AI-automated pipeline using LLMs to manage simultaneous global attacks on Fortinet devices. The future of scale is here.

Google releases Chrome v145.0.7632.116 to patch high-severity flaws in Media, DevTools, and the Tint graphics engine. Update now to prevent memory leaks.

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.

CISA warns of critical flaws in EOL USR-W610 IoT servers. CVE-2026-25715 allows full admin control via blank passwords. No patches planned; isolate now.
FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.

GitLab reveals how North Korean fake IT workers use 'Contagious Interview' scams to bypass hiring, steal data, and hijack executive digital identities.

Critical prototype pollution flaw (CVE-2026-27212) in the Swiper npm package allows RCE, DoS, and auth bypass. Update to version 12.1.2 immediately.

Researchers extract LUKS decryption keys in plaintext from Moxa UC-1222A devices via a novel TPM bus sniffing attack (CVE-2026-0714). Secure your hardware.
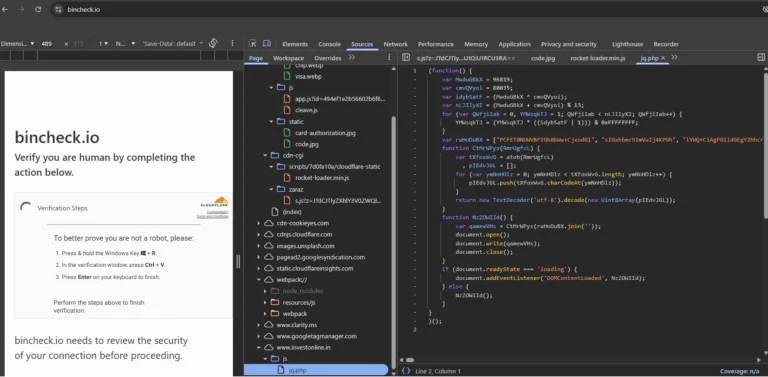
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.

OpenAI’s $500B Stargate venture has stalled. Sam Altman is now pivoting to a $30B Oracle "Plan B" to survive the brutal 2026 battle for energy and silicon.

Samsung’s Galaxy S26 debuts a "multi-agent" AI world. Call "Hey Plex" for real-time web search as Samsung Notes and Gallery sync with Perplexity’s brain.

Google has suspended thousands of Antigravity accounts linked to OpenClaw. Paid developers are hitting 403 errors with zero warning. Is your AI workflow safe?
IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.

Critical Undertow HTTP server flaw CVE-2025-12543 (CVSS 9.6) impacts HPE Telco Service Activator, allowing cache poisoning and session hijacking. Patch now.
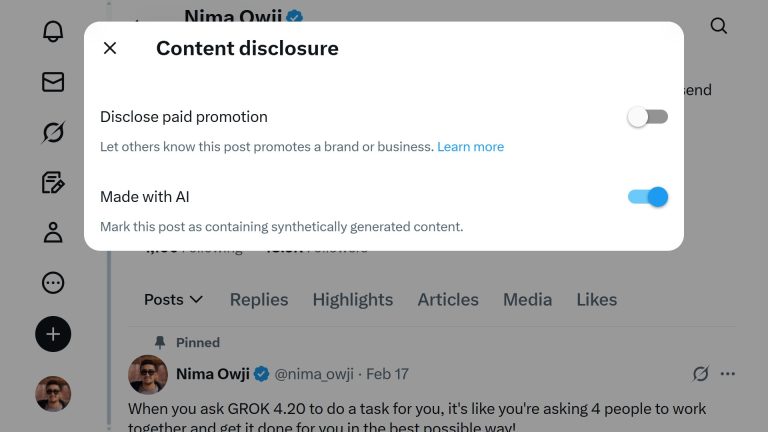
X is testing a new "AI-Generated" toggle for all posts. Fail to disclose synthetic content, and Community Notes could trigger a permanent account suspension.

Anthropic's Claude Code Security moves beyond pattern matching to "reason" through code, unearthing 500+ vulnerabilities missed by decades of human review.