
 Do Son
Transitioning your bank’s legacy system to a modern digital banking solution increases more than just available computing capacity. It...
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

See our list of free Database Comparison Software. You’ll find a complete list of products that come...

“Is it ok to ask someone to write my essays? Who can do my essay for me...

In the business world, there are a lot of acronyms that get thrown around and it can...

Google Play Store is a great resource for downloading Android apps, but is it safe? How do...

David Hoyt of Hoyt LLC conducted an in-depth analysis of the vulnerability and publicly disclosed CVE-2022-26730 PoC code.

CVE-2022-33684 can be exploited to launch a MITM attack and gain access to the communication channel between endpoints
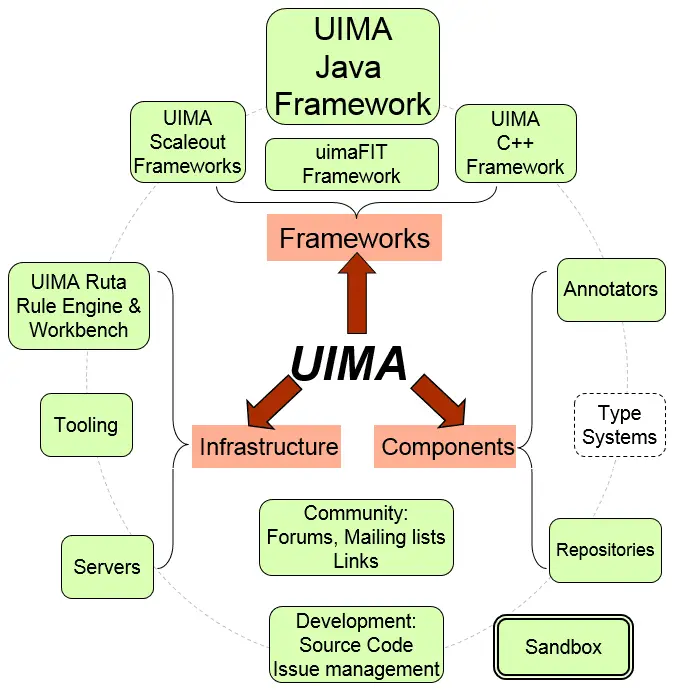
CVE-2022-32287 allows attacker to traverse directories on the system, caused by improper validation of user-supplied input in a FileUtil class

With the growing digitalization of systems, businesses need to ensure that they are secure and capable of...
To complete deals more efficiently and fast, companies use the services of virtual data rooms. These are...

Passwords don’t cut it anymore. About 80% of hacking-related breaches can be traced down to weak passwords,...

CVE-2022-20961 (CVSS score: 8.8) was caused by insufficient CSRF protections for the web-based management interface of an affected device

By sending a specially crafted HTTP request, an attacker could exploit CVE-2022-20958 to execute arbitrary code on the system
The well-known cloud storage provider Dropbox recently had a major security incident. Its employees received phishing emails

CVE-2022-43995 affecting plugins/sudoers/auth/passwd.c in Sudo could have resulted in the user gaining root privileges.

CVE-2022-3602 could result in a crash or potentially remote code execution depending on the stack layout for any given platform/compiler
CVE-2022-31692 is an authorization rule bypass vulnerability in a specific version of the Spring framework

The FIFA World Cup is set to be the biggest event of the year. This year it’s...

Zscaler ThreatLabz researcher team conducted an in-depth analysis of the vulnerability and publicly disclosed CVE-2022-37969 PoC

Video calling technology has taken over the world, and people can see and hear each other via...

Apache Flume released the latest security bulletin on October 26, which contains a remote code execution vulnerability (CVE-2022-42468).

OpenSSL project will announce the vulnerability CVE and other vulnerability details. The highest severity vulnerability fixed in OpenSSL is critical