
 Do Son
Group-IB provides a detailed examination of this breach, shedding light on the tactics employed by the emerging threat actor known as EstateRansomware
Cyber Security

A new, insidious phishing scam impersonating India's RTO has been detected, preying on unsuspecting Android users via WhatsApp

This includes the use of LNK files, MSbuild for loading the fileless backdoor, and novel methods for disabling event logging

Halcyon's research team has identified a new ransomware group dubbed "Volcano Demon," responsible for a series of recent attacks

CRIL has revealed a surge in cyberattacks exploiting the patched Microsoft Defender SmartScreen vulnerability (CVE-2024-21412)

The AhnLab Security Intelligence Center (ASEC) has issued a warning about a new backdoor malware called HappyDoor

Trend Micro, a global leader in cybersecurity, has issued a warning about a recent wave of attacks targeting misconfigured Jenkins servers

Cloudflare's popular 1.1.1.1 public DNS resolver service experienced disruptions, leaving a small percentage of users worldwide unable to access the service

Victims whose files have been encrypted by the Mallox ransomware Linux variant may be able to recover their data using the decryptors
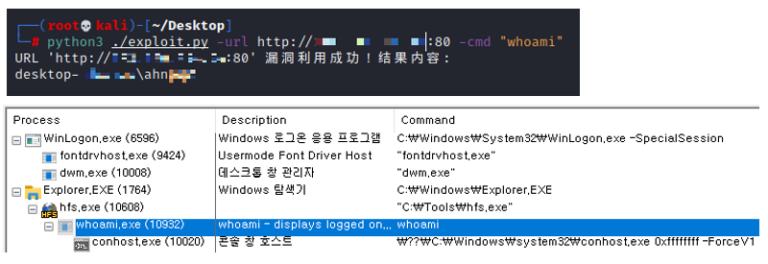
ASEC has observed a variety of attacks targeting HFS servers, including: Cryptomining, RATs and Backdoors, and Infiltration of GoThief malware

The team has observed a surge in malicious PDF files distributed via email, which contain embedded QR codes

Nearly three years after the notorious ProxyLogon and ProxyShell vulnerabilities caused widespread havoc on Microsoft Exchange servers
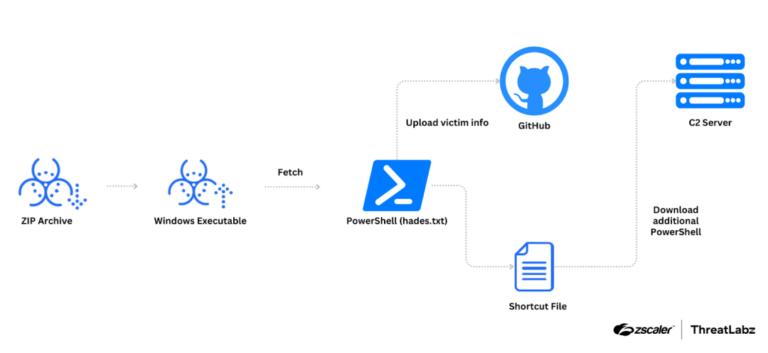
The group is deploying a malicious Google Chrome extension called "TRANSLATEXT" to steal sensitive information from South Korean academics

Chrome 127 and all subsequent versions will no longer trust newly issued digital certificates from the U.S private software company, Entrust

Water Sigbin employs various techniques, including creating scheduled tasks, adding exclusions to Windows Defender

threat actors are increasingly exploiting publicly available Cobalt Strike profiles to mask their malicious activities and bypass security measures

MerkSpy Spyware can silently record keystrokes, capture screenshots, and even steal login credentials from popular web browsers like Chrome

Rapid7 has uncovered a sophisticated supply chain attack targeting users of well-known Windows software tools Notezilla, RecentX, & Copywhiz

UAC-0184, leverages sophisticated techniques like DLL sideloading and the use of Python-related files to deliver the notorious XWorm RAT

"8220" mining gang, dubbed "k4spreader," represents a significant evolution in their arsenal, combining advanced persistence mechanisms
A new and sophisticated cyber attack campaign has surfaced, leveraging a weaponized Microsoft Word document to deliver the notorious Remcos RAT

Upon activation, StrelaStealer methodically scans the compromised system, first targeting Thunderbird email clients.