
 Do Son
Dubbed the "Smishing Triad," this group is leveraging stolen databases and impersonating Pakistan Post to defraud unsuspecting victims
Cyber Security

ASEC has published a report detailing a significant shift in the tactics employed by the Bondnet threat actor

The Black Basta ransomware group may have exploited a previously unknown vulnerability (CVE-2024-26169) in Windows Error Reporting Service

Cybersecurity researchers at Trend Micro have unveiled a previously undocumented backdoor malware dubbed "Noodle RAT,"

This vulnerability is currently being actively exploited by malicious actors in a widespread ransomware campaign known as "TellYouThePass."

Tracked as UNC5537, this financially motivated threat actor has systematically compromised hundreds of Snowflake customer accounts

Mustang Panda has been conducting a series of targeted attacks since April 2024, focusing on entities with interests in tax compliance and education

A surge in cyber activity associated with the Sticky Werewolf group, a threat actor with suspected geopolitical or hacktivist ties

A new variant of an ongoing cryptojacking campaign targeting misconfigured Kubernetes clusters has been uncovered

Sophos researchers have uncovered a sophisticated and long-running cyberespionage campaign, dubbed Operation Crimson Palace

Researchers have identified a concerning resurgence of attacks targeting known vulnerabilities in the ThinkPHP web application framework

Trustwave SpiderLabs has uncovered a dangerous cyberattack campaign targeting users of the popular network scanning tool, Advanced IP Scanner

Cybersecurity researchers have uncovered a novel cryptojacking campaign dubbed "Commando Cat," actively targeting Docker Remote API servers

A CoinMiner, a type of malware that hijacks systems to mine cryptocurrency, unwittingly left a backdoor open

A massive DNS probing operation, dubbed "Secshow," has been underway since June 2023, targeting open DNS resolvers worldwide

Trend Micro's threat-hunting team has uncovered a new Linux variant of the TargetCompany ransomware, marking a significant escalation

UNC1151 employed DLL loaders that downloaded an encrypted JPG file, which was then decrypted to deploy a final payload executable.
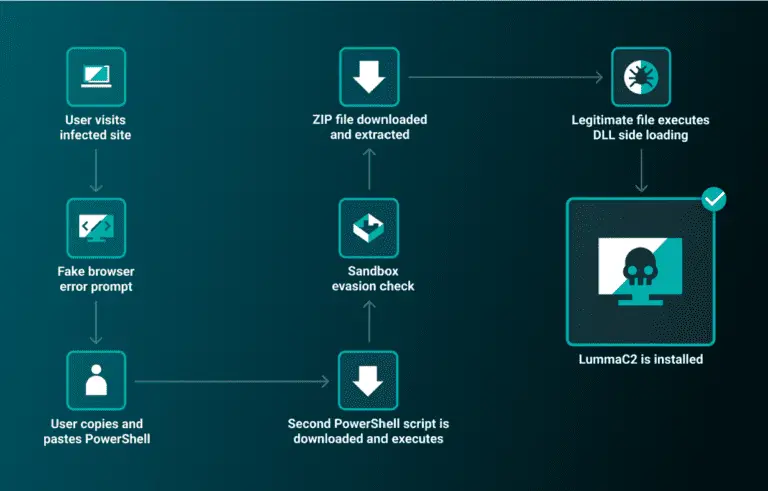
The ReliaQuest Threat Research Team has unveiled a new execution technique used in the ongoing ClearFake campaign

This multi-stage malware strategy ultimately delivers the notorious "Cobalt Strike" payload, establishing communication with a C2 server

WordPress, the world's most popular CMS, is facing a wave of targeted attacks exploiting critical vulnerabilities in several plugins

Hugging Face, a leading provider of open-source machine learning and AI tools, disclosed a security breach affecting its Spaces platform

BlueDelta even managed to bypass two-factor authentication and CAPTCHA challenges by leveraging compromised Ubiquiti routers