
 Do Son
LilacSquid deploys a series of malicious tools, including MeshAgent, a customized version of QuasarRAT, dubbed "PurpleInk,"
Cyber Security

A critical vulnerability (CVE-2024-3273) discovered in multiple end-of-life D-Link network-attached storage (NAS) devices

The campaign utilizes a complex DLL side-loading technique involving legitimate files from the IObit anti-malware solution to execute malicious payloads

XLab's CTIA System uncovered the abuse of the Kiteshield packer by various cyber threat actors targeting Linux environments

Rebirth botnet operates as a sophisticated cybercrime enterprise, offering a range of DDoS attack services through a web-based storefront

Cybersecurity firm ReliaQuest has published a detailed analysis of a BlackSuit ransomware attack that occurred in April 2024

A widespread email scam campaign is targeting students, faculty, healthcare workers, and others with offers of free pianos, leading victims

A distinctive aspect of Operation Diplomatic Specter is the use of previously undocumented backdoors, named TunnelSpecter and SweetSpecter

Moonstone Sleet deployed a new ransomware variant named FakePenny. This ransomware was used to target a company

Netskope Threat Labs has revealed a disturbing trend of malicious actors exploiting Cloudflare Workers to launch sophisticated phishing campaigns

In a parallel effort, Sharp Dragon targeted governmental organizations in the Caribbean, using compromised networks from Southeast Asia

Forcepoint X-Labs has issued an urgent warning regarding a surge in sophisticated phishing emails targeting government departments across the APAC region

NetbyteSEC Detecx (NBS) team exposed a sophisticated malware campaign orchestrated by the notorious SharpPanda APT group

Mandiant has revealed a concerning trend among China-linked cyber espionage groups: the use of ORB networks to enhance their espionage capabilities

CatDDoS-related gangs have leveraged a wide array of vulnerabilities across multiple vendor devices like Apache, Cisco, D-Link, Huawei, ...

The researchers likened the analysis of Unfading Sea Haze's malware arsenal to a "museum exposition of cyberespionage relics,"

One of the most notable aspects of CLOUD#REVERSER is its use of Google Drive and Dropbox for C2 communication and data exfiltration
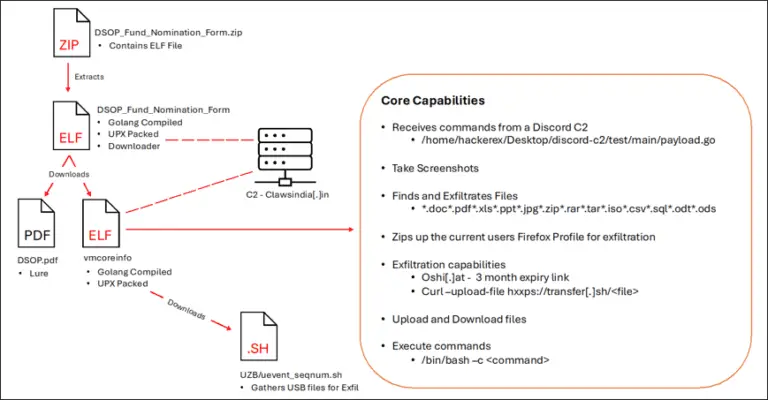
Researchers revealed a sustained campaign by Pakistani-based cyber espionage group APT36 targeting critical Indian government

The persistent cyber threat known as Kinsing malware has taken a new and sophisticated approach to its cryptojacking campaign

A recent attack by the Ransomhub ransomware gang has amplified concerns about the vulnerability of these critical systems

Ikaruz Red Team has been active in the Philippines, conducting attacks through various methods including defacements, small-scale DDoS attacks

UAC-0006 is known for its use of the SMOKELOADER malware, a versatile tool often used to deliver additional malicious payloads