
 Do Son
CRIL identified a sophisticated campaign employing a tiny, stealthy backdoor, now suspected to be the work of the infamous Turla APT group
Cyber Security

These Docusign Phishing Templates are being traded on cybercrime forums, particularly on a Russian cybercrime forum

The emergence of Void Manticore and its collaboration with Scarred Manticore underscores the escalating threat posed by state-sponsored cyber actors

Elastic Security Labs has shed light on a complex and insidious crypto-mining operation codenamed REF4578, with its core payload, GHOSTENGINE

The attackers exploited a known flaw in Microsoft Exchange Server, known as ProxyShell, to inject the keylogger into the server’s main page

A new report reveals a disturbing trend in cyber attacks: the increasing use of Microsoft OneNote files to deliver malicious payloads

Cybersecurity researchers at Elastic Security Labs have issued a warning about the increasing prominence of LATRODECTUS, a malware loader

The North Korean state-sponsored group Springtail (also known as Kimsuky) has added a new Linux backdoor, dubbed Gomir, to its arsenal

This novel use of Tesseract is part of a broader strategy by ViperSoftX to install additional malware strains, including Quasar RAT

A recent analysis by S-RM, a global cybersecurity consultancy, has shed light on the escalating sophistication of...

Each tasked with managing activities and establishing communication with compromised IPs to facilitate the distribution of XMRig cryptominers

The campaign, dubbed UNK_SweetSpecter, utilizes a Remote Access Trojan (RAT) known as SugarGh0st to infiltrate systems and exfiltrate sensitive data
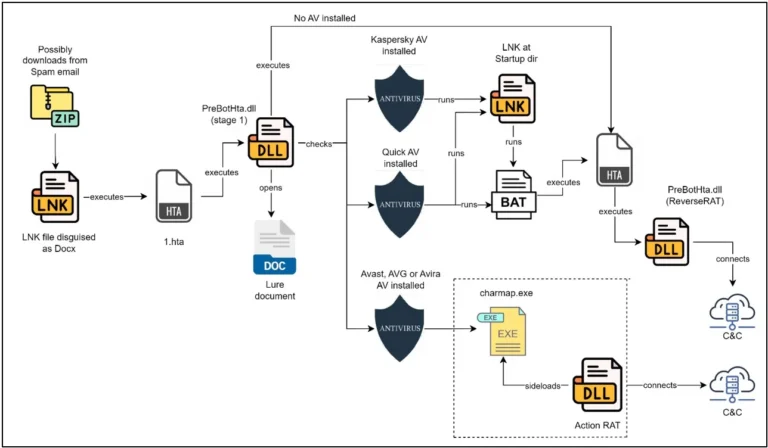
Upon further investigation, CRIL uncovered the use of malicious LNK files in the SideCopy malware campaign. These files, once executed

The campaign exploits GitHub, a legitimate platform for software development, to distribute various malware families

The campaign's success lies in its ability to bypass MFA, a security measure designed to protect accounts from unauthorized access

One of the most prevalent scams involves the Instagram influencer program, designed to connect content creators with brand partnerships

The Russia-linked Advanced Persistent Threat groups continues to evolve, posing a significant threat to Operational Technology globally
Forcepoint's X-Labs research team has uncovered a sophisticated and stealthy phishing campaign orchestrated by the notorious Darkgate malware

A widespread malvertising campaign is actively targeting individuals searching for popular utilities like WinSCP and PuTTY

Microsoft Threat Intelligence has uncovered a sophisticated ransomware campaign orchestrated by the cybercriminal group Storm-1811

Proofpoint uncovered a massive campaign distributing LockBit Black ransomware through millions of emails via the Phorpiex botnet

Ebury is used to deploy additional malware, including malicious Apache and nginx modules that facilitate web traffic redirection