
 Do Son
Cybersecurity researchers are tracking a significant escalation in activity from the GOLD IONIC ransomware group
Cyber Security
This vulnerability, found in the TP-Link Archer AX21's web management interface, allows hackers to inject malicious code without needing the router's password

To increase their attacks' success rate, TA427 often impersonates respected members of the foreign policy community.

A new report by cybersecurity firm Resecurity highlights a marked increase in misinformation campaigns and hacktivist activity targeting the Philippines

A newly exposed attack campaign, dubbed "Connect:fun," is raising alarms in the media sector, Forescout Research – Vedere Labs warns

A sophisticated and coordinated cyber phishing campaign has been targeting major financial institutions across Southeast Asia

This pervasive campaign, aptly named "SteganoAmor" due to its use of steganography—a method of hiding malware within innocuous-looking files
A potent new banking trojan dubbed "Coyote" is sweeping through Brazil's financial sector, prompting urgent warnings

The main component of this multi-stage attack is the FatalRAT malware. This grants the attackers remote control over a victim's computer

Apple has sent warnings to a growing number of users, alerting them about highly sophisticated mercenary spyware attacks

Cybercriminals, demonstrating both ingenuity and malice, have initiated a campaign that manipulates GitHub's search functionality to distribute malware

The cornerstone of this campaign is the deployment of Rhadamanthys, an information-stealing malware previously unseen in TA547's arsenal

Threat actors are compromising these popular data stores to install the potent Metasploit Meterpreter backdoor.

The timing of the artifacts associated with this campaign suggests that Starry Addax may be ramping up its operations.

They're using malicious ads disguised as legitimate software downloads on Google Search to infect the computers of unsuspecting system administrators

The infamous "Muddled Libra" hacking group is setting its sights on a new frontier: the cloud and Software-as-a-Service (SaaS)

The attackers used a malware strain dubbed LazyStealer to pilfer login credentials, demonstrating that even unsophisticated tools

CVE-2023-48788, a vulnerability within the Fortinet FortiClient EMS, a security management solution pivotal

Threat actors deploy malware to hijack legitimate systems, turning them into unwilling participants in the scanning of networks for vulnerabilities

Threat actors behind this operation are strategically leveraging the ScrubCrypt tool, notorious for its antivirus evasion capabilities

A sophisticated campaign spearheaded by MuddyWater, an entity known for its state-sponsored activities, unveiling the DarkBeatC2 framework
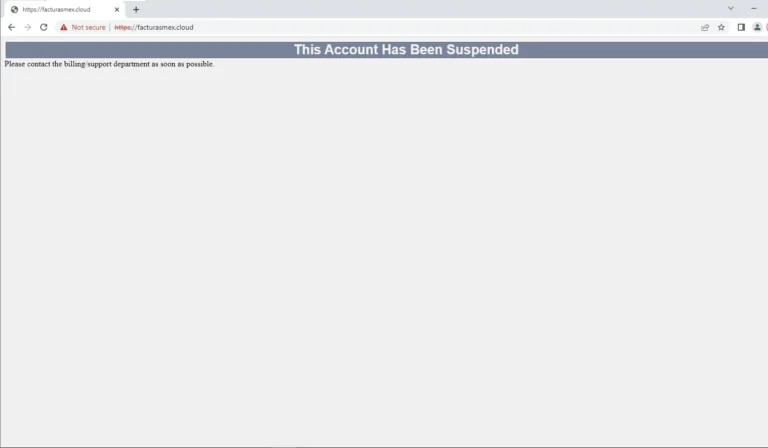
An orchestrated phishing scheme has surfaced, exploiting the illusion of suspended web pages to deliver a nasty payload of malware