
 Do Son
In a disturbing trend uncovered by Bitdefender Labs, malicious actors are weaponizing the growing fascination with AI to spread sophisticated malware
Cyber Security

In a joint report by Proofpoint's Threat Research team and Team Cymru, a potent new malware dubbed "Latrodectus" has been exposed

Before its recent activities in the APAC and MENA regions, JSOutProx had been implicated in targeted attacks against Indian Cooperative Banks

Researchers have uncovered a sophisticated cybercrime operation dubbed "CoralRaider," pinpointing the threat actors as likely based in Vietnam

attacks exploiting unpatched vulnerabilities result in significantly more severe outcomes than those leveraging compromised credentials

The expansion of the fake e-shop campaign to target 18 banks in Malaysia, coupled with its reach into Vietnam and Myanmar

threat actors are targeting consumer users, particularly younger audiences drawn to popular video games, by promoting cracked software

Check Point Research has lifted the veil of anonymity surrounding two cybercrime actors responsible for recent Agent Tesla malware campaigns
A new report highlights a disturbing increase in targeted phishing attacks launched by a loosely affiliated group of cybercriminals
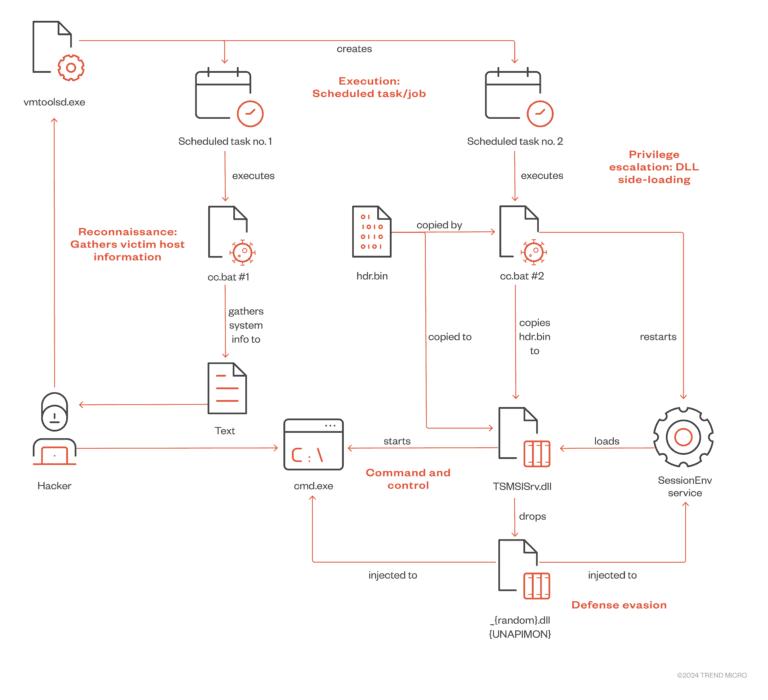
In a cyberespionage campaign attributed to Earth Freybug, security researchers from Trend Micro observed a unique malware, dubbed UNAPIMON

Cisco has issued a critical warning about a widespread password spraying campaign targeting Remote Access VPN (RAVPN)

A report by CyberArk reveals a sinister trend: the rise of 'infostealer' malware specifically designed to steal web session cookies.

CRIL have exposed a worrying nexus between recent Solana wallet draining attacks and the notorious MS Drainer malware

PyPi, a vital repository for open-source software, has taken the drastic step of temporarily halting new user registrations and project creation

A new report from EclecticIQ analysts has uncovered a sophisticated cyber espionage campaign dubbed "Operation FlightNight"

In a shift of tactics that demonstrates their adaptability, Stately Taurus dispatched another malicious package, "Note PSO.scr," on March 5

Researchers at Lumen Technologies' Black Lotus Labs have uncovered a newly updated version of the "TheMoon" malware

Industrial Espionage: The most alarming scenario is a targeted attack designed to steal sensitive data (credentials, design plans, etc.)

GEOBOX system is designed for simplicity. With a user manual providing step-by-step instructions, even those with limited technical

over 170,000 Python developers have fallen victim to a sophisticated malware scheme designed to steal sensitive data

The employment of WINELOADER, endowed with features overlapping with other APT29 malware families such as BURNTBATTER and MUSKYBEAT
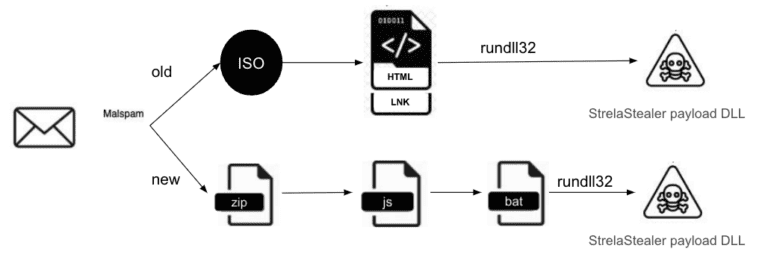
Researchers at Unit 42 have uncovered a major new attack campaign deploying an updated version of the StrelaStealer malware