
 Do Son
The recently disclosed vulnerabilities in ScreenConnect (CVE-2024-1709, CVE-2024-1708) necessitate immediate action
Cyber Security

VOLTZITE, a threat group known for persistent targeting of global critical infrastructure sectors, continues to refine its methods

The notorious 8220 Gang has resurfaced, targeting cloud infrastructure in a campaign demonstrating significant advancements

Researchers at Talos and CERT.NGO have pulled back the curtain on new malicious components deployed by the notorious Turla APT group

Trustwave SpiderLabs' Email Security team has uncovered a sophisticated Phishing-as-a-Service (PaaS) platform known as Tycoon Group

The primary malware, dubbed "TrollAgent," was a data thief developed in GoLang and capable of stealing a wide array of information

Lucifer DDoS botnet is exploiting misconfigurations and vulnerabilities in Apache Hadoop and Apache Druid (CVE-2021-25646)

Carpet-Bombing DDoS attacks inundate entire CIDR blocks, cloaking their malicious intent in a veil of complexity and making detection

Masquerading an internal sale of a BMW vehicle, APT29 distributed over 200 emails, embedding the RAR file that served as the Trojan horse

Domains associated with Operation Texonto were found linked to potential influence operations aimed at Russian citizens

The Lazarus Group, a skilled North Korean state-sponsored hacking collective, continues to aggressively target entities in the global defense sector

Key to APT group Earth Preta is a custom malware dubbed DOPLUGS, a critical tool leveraged in a range of recent intrusions.

UK's National Crime Agency has confirmed that Lockbit's operations have been disrupted due to the international joint law enforcement effort

Italian Computer Security Incident Response Team has issued a critical warning about a resurgence of the "Helpdesk Support" phishing campaign

According to Qrator Labs, 2023 was a year of marked transformation in the world of Distributed Denial of Service (DDoS) attacks.

TAG-70 threat actor leverages sophisticated techniques to infiltrate and exploit, revealing a saga of digital warfare

A recent Malwarebytes Labs investigation unveiled a significant campaign of fraudulent ads served to users through Google searches

Armed with a diverse arsenal of malware, including the notorious AppleSeed and AlphaSeed strains, Kimsuky's tactics have evolved
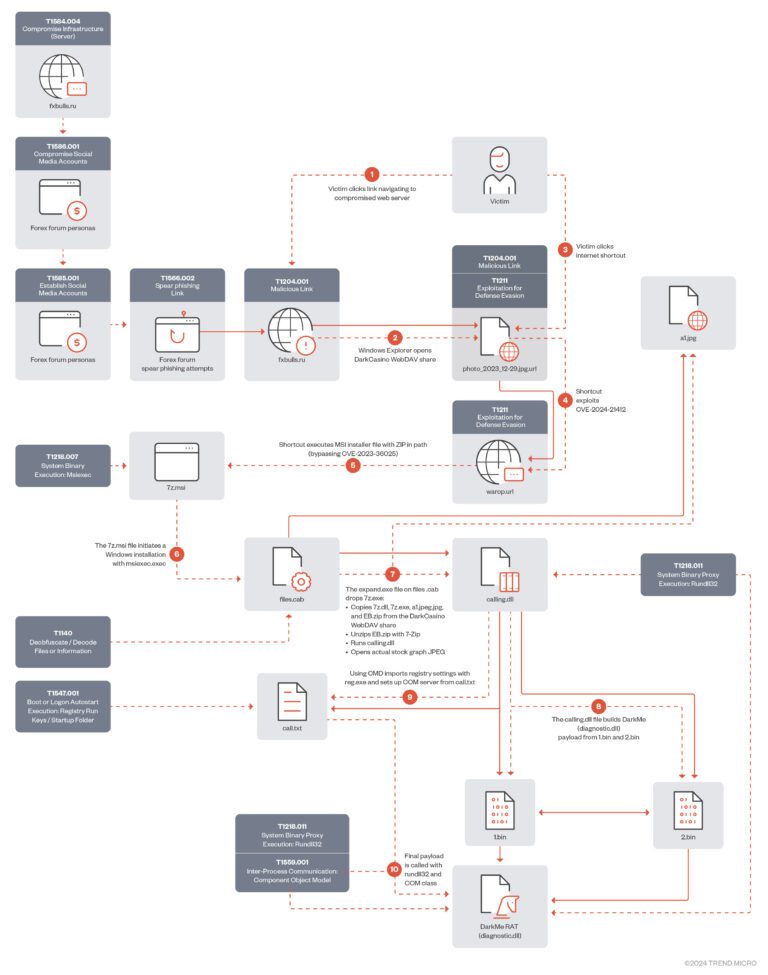
This flaw, exploited by Water Hydra, served as a linchpin in a complex 0-day attack chain, leading to a bypass of Defender SmartScreen

One notable aspect of CharmingCypress's tactics is their use of unusual social-engineering tactics in their phishing campaigns

A formidable malware known as Glupteba has been lurking, evolving, and spreading its tentacles across the globe

Arctic Wolf Labs uncovered threat actors are leveraging CVE-2023-22527 to deploy C3RB3R ransomware alongside a suite of other malicious payloads