 Do Son
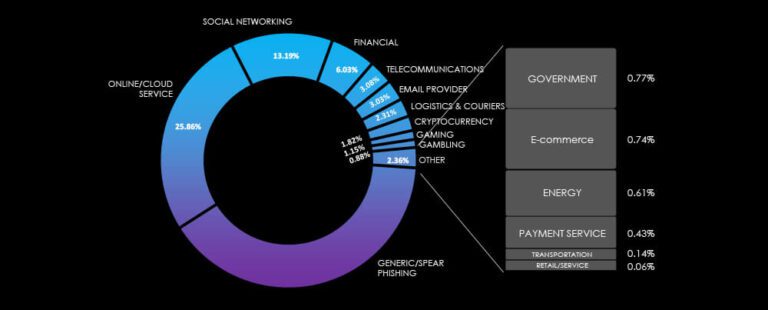
CYFIRMA Industries Report offers an illuminating look into the current state of cyber threats, in the professional goods & services industry
Cyber Security

Dubbed 'Operation Japan,' this campaign unfolds against the backdrop of Japan's controversial decision to release treated water

The Turkish espionage campaigns in the Netherlands represent a significant shift in the landscape of international cyber warfare

Kimsuky, has unleashed a sophisticated spearphishing campaign, targeting hundreds of influential individuals globally

GXC Team has enhanced its capabilities for automated operations, targeted social engineering, and bypassing cybersecurity measures

At the heart of the UAC-0050 threat group's arsenal is RemcosRAT, a malware for remote surveillance and control.

Advent of scheduled task tampering as a persistence mechanism underscores the need for continuous evolution in threat-hunting

These actors have been utilizing the ms-appinstaller protocol handler as a vector for malware, potentially leading to ransomware distribution

Panasonic Avionics Corporation, revealed that they suffered a cyberattack at the end of 2022, which may have led to the leak of personal information

Central to Kimsuky's operations is AppleSeed, a backdoor malware that facilitates remote system control. It can execute commands

CVE-2023-41990 was addressed with improved handling of caches. This issue is fixed in tvOS 16.3, iOS 16.3 and iPadOS 16.3
NASA has released the edition of a guide on best practices for cybersecurity in space, as announced in a press release on the website

In the vast expanse of the digital ocean, a new wave of cyber attacks has emerged, targeting the seemingly unassuming Linux SSH servers.

As UAC-0050 adapts and refines its tactics, utilizing services of a Malaysian provider and the autonomous system AS44477 for hosting
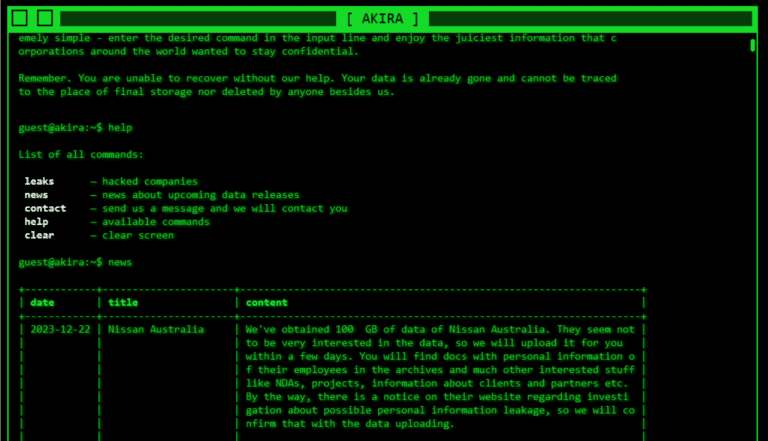
The ransomware group Akira has declared responsibility for the recent cyberattack on the systems of Nissan in Australia and New Zealand

Dubbed Operation RusticWeb, this campaign, uncovered in October 2023, demonstrates a nuanced approach to cyber espionage.

An emerging Iranian hacking group named Cyber Toufan recently disclosed stolen data from 49 Israeli companies.

The campaign unfolded stealthily, leveraging the relatively new Nim programming language to construct a malicious backdoor

Europol undertook a concerted effort to notify 443 online retailers about the compromise of their customers' payment card data
At present, Ubisoft is reluctant to disclose detailed information about this data breach. Several days have elapsed since the incident

Cyber threat actor UAC-0099 has been actively targeting Ukraine since mid-2022, according to insights from the Deep Instinct Threat Lab

BattleRoyal cluster is notable for its diverse attack chains designed to deliver malware efficiently. DarkGate serves as the gateway